Pre-Winter Sale 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: save70

Free and Premium Cisco 350-701 Dumps Questions Answers

Page: 1 / 60
Total 801 questions

Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) Questions and Answers

Question 1

An engineer wants to generate NetFlow records on traffic traversing the Cisco ASA. Which Cisco ASA

command must be used?

Options:

A.

flow-export destination inside 1.1.1.1 2055

B.

ip flow monitor input

C.

ip flow-export destination 1.1.1.1 2055

D.

flow exporter

Buy Now
Question 2

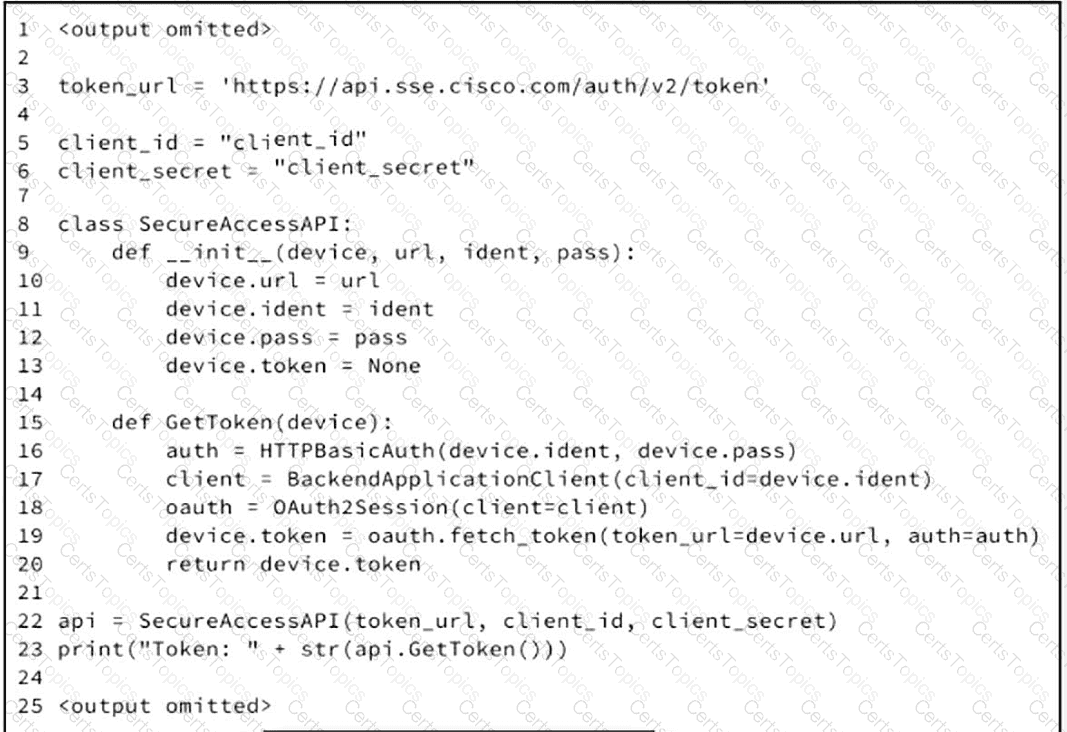
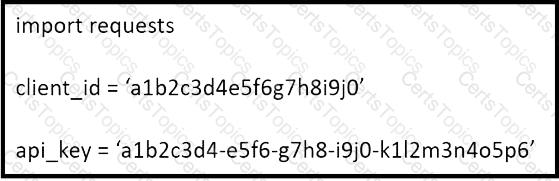
Refer to the exhibit.

An engineer creates a Python script to make an API call to Cisco Secure Access. Which output should be expected from the script?

Options:

A.

Endpoint token

B.

Device URL

C.

Access token

D.

Client secret

Question 3

An engineer is trying to decide between using L2TP or GRE over IPsec for their site-to-site VPN implementation. What must be un solution?

Options:

A.

L2TP is an IP packet encapsulation protocol, and GRE over IPsec is a tunneling protocol.

B.

L2TP uses TCP port 47 and GRE over IPsec uses UDP port 1701.

C.

GRE over IPsec adds its own header, and L2TP does not.

D.

GRE over IPsec cannot be used as a standalone protocol, and L2TP can.

Question 4

What is a commonality between DMVPN and FlexVPN technologies?

Options:

A.

FlexVPN and DMVPN use IS-IS routing protocol to communicate with spokes

B.

FlexVPN and DMVPN use the new key management protocol

C.

FlexVPN and DMVPN use the same hashing algorithms

D.

IOS routers run the same NHRP code for DMVPN and FlexVPN

Question 5

A network engineer is trying to figure out whether FlexVPN or DMVPN would fit better in their environment.

They have a requirement for more stringent security multiple security associations for the connections, more efficient VPN establishment as well consuming less bandwidth. Which solution would be best for this and why?

Options:

A.

DMVPN because it supports IKEv2 and FlexVPN does not

B.

FlexVPN because it supports IKEv2 and DMVPN does not

C.

FlexVPN because it uses multiple SAs and DMVPN does not

D.

DMVPN because it uses multiple SAs and FlexVPN does not

Question 6

What is the role of Cisco Umbrella Roaming when it is installed on an endpoint?

Options:

A.

To protect the endpoint against malicious file transfers

B.

To ensure that assets are secure from malicious links on and off the corporate network

C.

To establish secure VPN connectivity to the corporate network

D.

To enforce posture compliance and mandatory software

Question 7

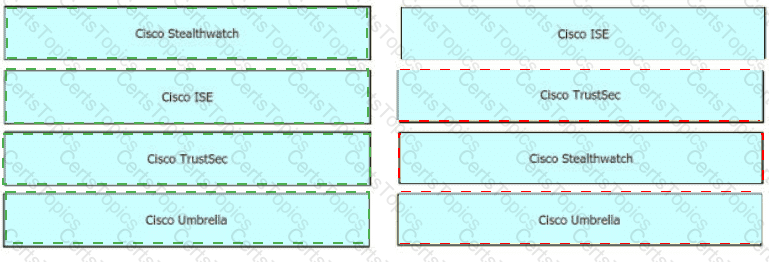
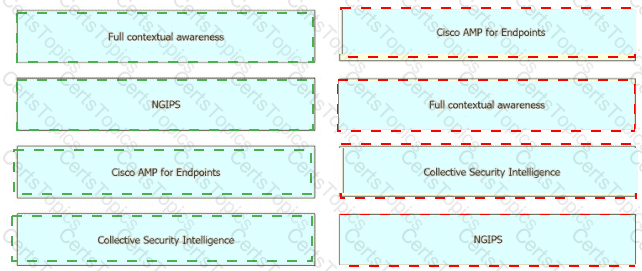
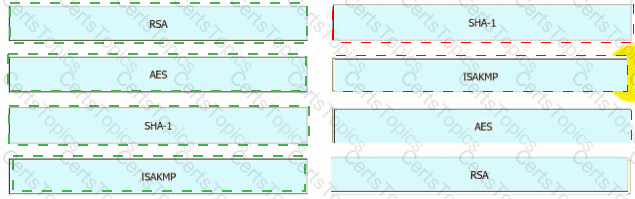
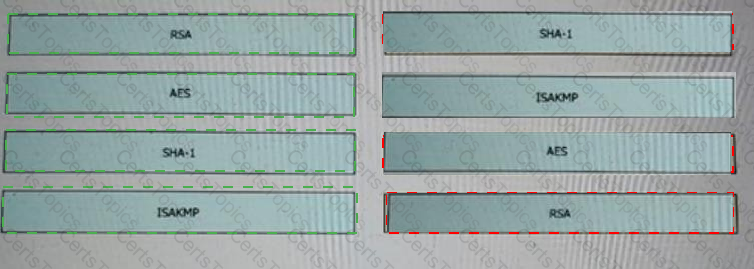
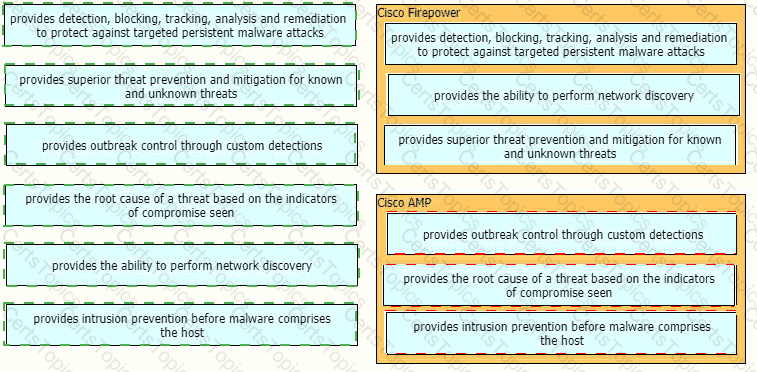
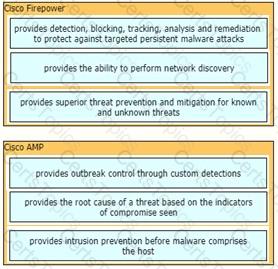
Drag and drop the solutions from the left onto the solution ' s benefits on the right.
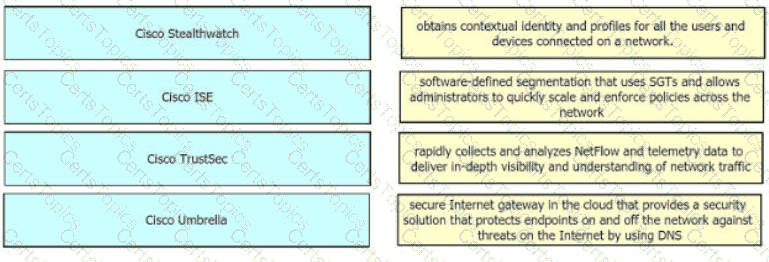
Options:

Question 8

A network engineer has entered the snmp-server user andy myv3 auth sha cisco priv aes 256

cisc0380739941 command and needs to send SNMP information to a host at 10.255.254.1. Which command achieves this goal?

Options:

A.

snmp-server host inside 10.255.254.1 version 3 andy

B.

snmp-server host inside 10.255.254.1 version 3 myv3

C.

snmp-server host inside 10.255.254.1 snmpv3 andy

D.

snmp-server host inside 10.255.254.1 snmpv3 myv3

Question 9

An engineer is configuring cloud logging using a company-managed Amazon S3 bucket for Cisco Umbrella logs. What benefit does this configuration provide for accessing log data?

Options:

A.

It is included m the license cost for the multi-org console of Cisco Umbrella

B.

It can grant third-party SIEM integrations write access to the S3 bucket

C.

No other applications except Cisco Umbrella can write to the S3 bucket

D.

Data can be stored offline for 30 days.

Question 10

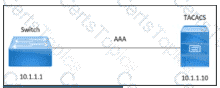
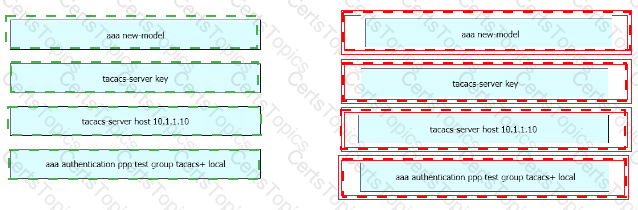
Refer to the exhibit.

An engineer must configure a Cisco switch to perform PPP authentication via a TACACS server located at IP address 10.1.1.10. Authentication must fall back to the local database using the username LocalUser and password C1Sc0451069341l if the TACACS server is unreachable.

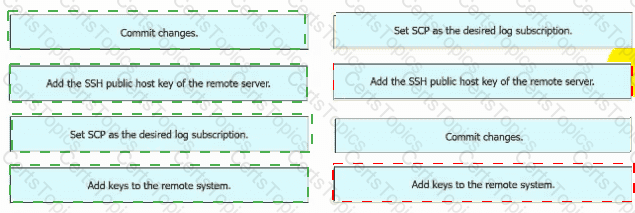
Drag and drop the commands from the left onto the corresponding configuration steps on the right.
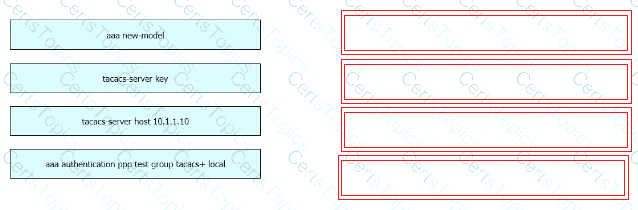
Options:

Question 11

How does Cisco Umbrella archive logs to an enterprise owned storage?

Options:

A.

by using the Application Programming Interface to fetch the logs

B.

by sending logs via syslog to an on-premises or cloud-based syslog server

C.

by the system administrator downloading the logs from the Cisco Umbrella web portal

D.

by being configured to send logs to a self-managed AWS S3 bucket

Question 12

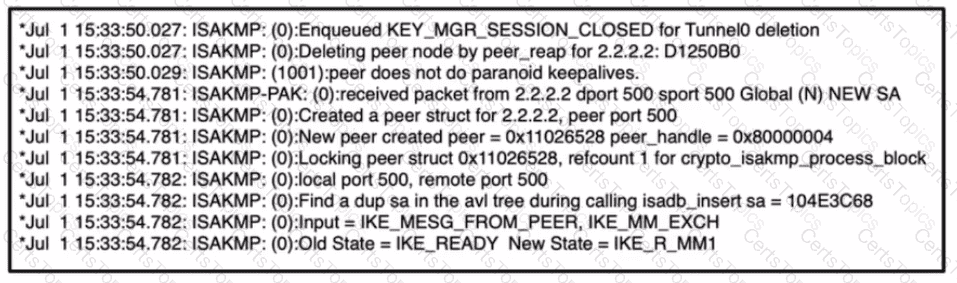
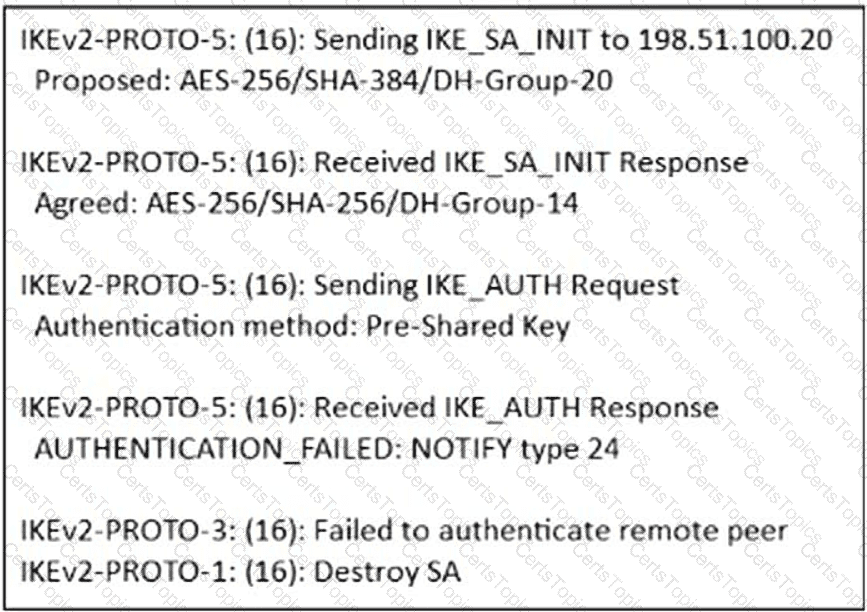
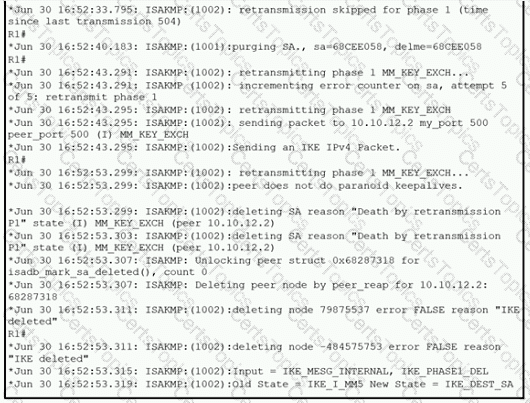
Refer to the exhibit,

which command results in these messages when attempting to troubleshoot an iPsec VPN connection?

Options:

A.

debug crypto isakmp

B.

debug crypto ipsec endpoint

C.

debug crypto Ipsec

D.

debug crypto isakmp connection

Question 13

Which Cisco platform provides an agentless solution to provide visibility across the network including encrypted traffic analytics to detect malware in encrypted traffic without the need for decryption?

Options:

A.

Cisco Advanced Malware Protection

B.

Cisco Stealthwatch

C.

Cisco Identity Services Engine

D.

Cisco AnyConnect

Question 14

An engineer must modify an existing remote access VPN using a Cisco AnyConnect Secure Mobility client solution and a Cisco Secure Firewall. Currently, all the traffic generate by the user Is sent to the VPN tunnel and the engineer must now exclude some servers and access them directly instead. Which element must be modified to achieve this goat?

Options:

A.

NAT exemption

B.

encryption domain

C.

routing table

D.

group policy

Question 15

An administrator needs to configure the Cisco ASA via ASDM such that the network management system

can actively monitor the host using SNMPv3. Which two tasks must be performed for this configuration?

(Choose two.)

Options:

A.

Specify the SNMP manager and UDP port.

B.

Specify an SNMP user group

C.

Specify a community string.

D.

Add an SNMP USM entry

E.

Add an SNMP host access entry

Question 16

What is provided by the Secure Hash Algorithm in a VPN?

Options:

A.

integrity

B.

key exchange

C.

encryption

D.

authentication

Question 17

Which Dos attack uses fragmented packets to crash a target machine?

Options:

A.

smurf

B.

MITM

C.

teardrop

D.

LAND

Question 18

Which Talos reputation center allows for tracking the reputation of IP addresses for email and web traffic?

Options:

A.

IP and Domain Reputation Center

B.

File Reputation Center

C.

IP Slock List Center

D.

AMP Reputation Center

Question 19

Which SNMPv3 configuration must be used to support the strongest security possible?

Options:

A.

asa-host(config)#snmp-server group myv3 v3 privasa-host(config)#snmp-server user andy myv3 auth sha cisco priv des ciscXXXXXXXXasa-host(config)#snmp-server host inside 10.255.254.1 version 3 andy

B.

asa-host(config)#snmp-server group myv3 v3 noauthasa-host(config)#snmp-server user andy myv3 auth sha cisco priv aes 256 ciscXXXXXXXXasa-host(config)#snmp-server host inside 10.255.254.1 version 3 andy

C.

asa-host(config)#snmpserver group myv3 v3 noauthasa-host(config)#snmp-server user andy myv3 auth sha cisco priv 3des ciscXXXXXXXXasa-host(config)#snmp-server host inside 10.255.254.1 version 3 andy

D.

asa-host(config)#snmp-server group myv3 v3 privasa-host(config)#snmp-server user andy myv3 auth sha cisco priv aes 256 ciscXXXXXXXXasa-host(config)#snmp-server host inside 10.255.254.1 version 3 andy

Question 20

Which method of attack is used by a hacker to send malicious code through a web application to an unsuspecting user to request that the victim ' s web browser executes the code?

Options:

A.

buffer overflow

B.

browser WGET

C.

SQL injection

D.

cross-site scripting

Question 21

An administrator configures a new destination list in Cisco Umbrella so that the organization can block specific domains for its devices. What should be done to ensure that all subdomains of domain.com are blocked?

Options:

A.

Configure the *.com address in the block list.

B.

Configure the *.domain.com address in the block list

C.

Configure the *.domain.com address in the block list

D.

Configure the domain.com address in the block list

Question 22

Which two conditions are prerequisites for stateful failover for IPsec? (Choose two)

Options:

A.

Only the IKE configuration that is set up on the active device must be duplicated on the standby device; theIPsec configuration is copied automatically

B.

The active and standby devices can run different versions of the Cisco IOS software but must be the sametype of device.

C.

The IPsec configuration that is set up on the active device must be duplicated on the standby device

D.

Only the IPsec configuration that is set up on the active device must be duplicated on the standby device;the IKE configuration is copied automatically.

E.

The active and standby devices must run the same version of the Cisco IOS software and must be thesame type of device

Question 23

What are two ways a network administrator transparently identifies users using Active Directory on the Cisco WSA? (Choose two.)

Options:

A.

Create an LDAP authentication realm and disable transparent user identification.

B.

Create NTLM or Kerberos authentication realm and enable transparent user identification.

C.

Deploy a separate Active Directory agent such as Cisco Context Directory Agent.

D.

The eDirectory client must be installed on each client workstation.

E.

Deploy a separate eDirectory server; the dent IP address is recorded in this server.

Question 24

What is the term for having information about threats and threat actors that helps mitigate harmful events that would otherwise compromise networks or systems?

Options:

A.

trusted automated exchange

B.

Indicators of Compromise

C.

The Exploit Database

D.

threat intelligence

Question 25

What provides the ability to program and monitor networks from somewhere other than the DNAC GUI?

Options:

A.

NetFlow

B.

desktop client

C.

ASDM

D.

API

Question 26

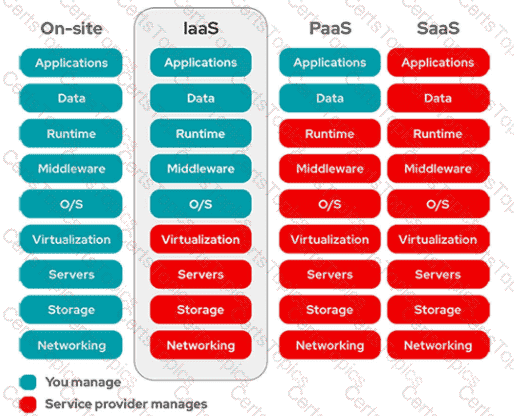
Which cloud service model offers an environment for cloud consumers to develop and deploy applications

without needing to manage or maintain the underlying cloud infrastructure?

Options:

A.

PaaS

B.

XaaS

C.

IaaS

D.

SaaS

Question 27

A manufacturing company contracted an external software vendor to develop an application that dynamically creates marketing messages personalized to the business and audience. To ensure that communication between the sender and recipient email addresses does not create false positives, an exception rule must be configured in Cisco Secure Email Threat Defense. Which configuration must be performed?

Options:

A.

Implement an Exception Rule with a wildcard email address.

B.

Add a Policy Exception Rule with a Sender/Recipient pair set.

C.

Apply a sender-based Policy Exception Rule.

D.

Configure a recipient-based Policy Exception Rule.

Question 28

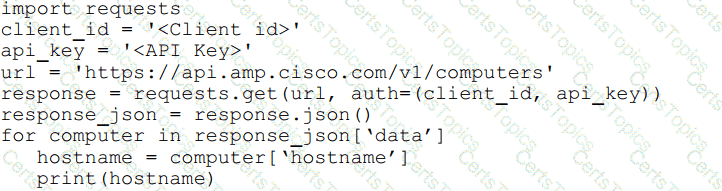
Refer to the exhibit.

What will happen when the Python script is executed?

Options:

A.

The hostname will be translated to an IP address and printed.

B.

The hostname will be printed for the client in the client ID field.

C.

The script will pull all computer hostnames and print them.

D.

The script will translate the IP address to FODN and print it

Question 29

A network engineer is deploying multiple Cisco Secure Firewall Threat Defense devices across two data centers. The solution has the following requirements:

    Management must have no Internet dependency.

    Management must remain accessible during major outages.

    Policy management must be centralized.

Which solution must be implemented to meet the requirements?

Options:

A.

Deploy an on-premises Cisco Secure Firewall Management Center high-availability pair with a dedicated out-of-band network.

B.

Deploy one Cisco Secure Firewall Management Center per data center with in-band network management.

C.

Use Cisco Security Cloud Control over the Internet with no on-premises managers.

D.

Manage each firewall locally with Cisco Secure Firewall Device Manager over the production network.

Question 30

What are two ways a network administrator transparently identifies users using Active Directory on the Cisco WSA? (Choose two.) The eDirectory client must be installed on each client workstation.

Options:

A.

Create NTLM or Kerberos authentication realm and enable transparent user identification

B.

Deploy a separate Active Directory agent such as Cisco Context Directory Agent.

C.

Create an LDAP authentication realm and disable transparent user identification.

D.

Deploy a separate eDirectory server: the client IP address is recorded in this server

Question 31

A customer has various external HTTP resources available including Intranet Extranet and Internet, with a

proxy configuration running in explicit mode. Which method allows the client desktop browsers to be configured

to select when to connect direct or when to use the proxy?

Options:

A.

Transport mode

B.

Forward file

C.

PAC file

D.

Bridge mode

Question 32

Which two are valid suppression types on a Cisco Next Generation Intrusion Prevention System? (Choose two)

Options:

A.

Port

B.

Rule

C.

Source

D.

Application

E.

Protocol

Question 33

Which Cisco platform onboards the endpoint and can issue a CA signed certificate while also automatically configuring endpoint network settings to use the signed endpoint certificate, allowing the endpoint to gain network access?

Options:

A.

Cisco ISE

B.

Cisco NAC

C.

Cisco TACACS+

D.

Cisco WSA

Question 34

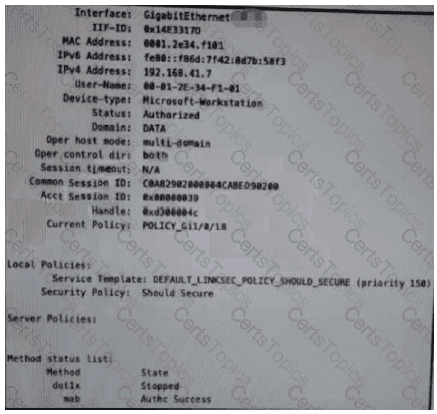
Refer to the exhibit.

Which configuration item makes it possible to have the AAA session on the network?

Options:

A.

aaa authentication login console ise

B.

aaa authentication enable default enable

C.

aaa authorization network default group ise

D.

aaa authorization exec default ise

Question 35

An engineer is deploying a Cisco Secure Email Gateway and must ensure it reaches the Cisco update servers to retrieve new rules. The engineer must now manually configure the Outbreak Filter rules on an AsyncOS for Cisco Secure Email Gateway. Only outdated rules must be replaced. Up-to-date rules must be retained. Which action must the engineer take next to complete the configuration?

Options:

A.

Select Outbreak Filters

B.

Perform a backup/restore of the database

C.

Use the outbreakconfig command in CLI

D.

Click Update Rules Now

Question 36

Which two commands are required when configuring a flow-export action on a Cisco ASA? (Choose two.)

Options:

A.

flow-export event-type

B.

policy-map

C.

access-list

D.

flow-export template timeout-rate 15

E.

access-group

Question 37

Which threat intelligence standard contains malware hashes?

Options:

A.

structured threat information expression

B.

advanced persistent threat

C.

trusted automated exchange or indicator information

D.

open command and control

Question 38

An administrator configures a Cisco WSA to receive redirected traffic over ports 80 and 443. The organization requires that a network device with specific WSA integration capabilities be configured to send the traffic to the WSA to proxy the requests and increase visibility, while making this invisible to the users. What must be done on the Cisco WSA to support these requirements?

Options:

A.

Configure transparent traffic redirection using WCCP in the Cisco WSA and on the network device

B.

Configure active traffic redirection using WPAD in the Cisco WSA and on the network device

C.

Use the Layer 4 setting in the Cisco WSA to receive explicit forward requests from the network device

D.

Use PAC keys to allow only the required network devices to send the traffic to the Cisco WSA

Question 39

Which deployment model is the most secure when considering risks to cloud adoption?

Options:

A.

Public Cloud

B.

Hybrid Cloud

C.

Community Cloud

D.

Private Cloud

Question 40

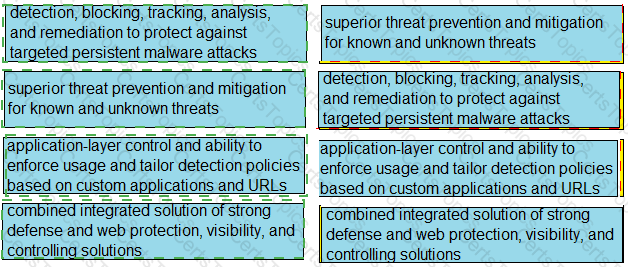
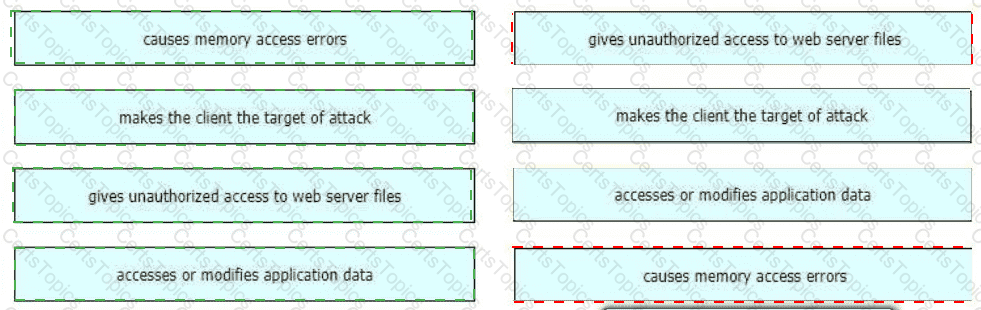
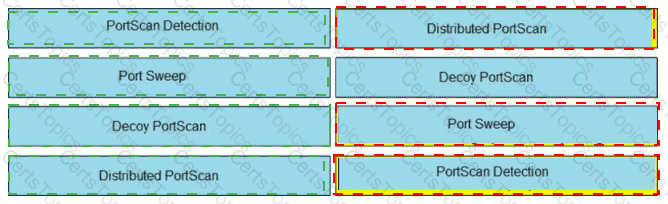
Drag and drop the security solutions from the left onto the benefits they provide on the right.
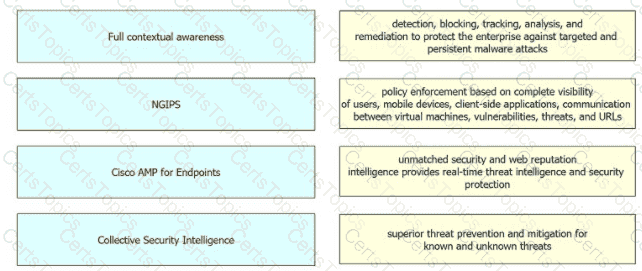
Options:

Question 41

An engineer adds a custom detection policy to a Cisco AMP deployment and encounters issues with the

configuration. The simple detection mechanism is configured, but the dashboard indicates that the hash is not 64 characters and is non-zero. What is the issue?

Options:

A.

The engineer is attempting to upload a hash created using MD5 instead of SHA-256

B.

The file being uploaded is incompatible with simple detections and must use advanced detections

C.

The hash being uploaded is part of a set in an incorrect format

D.

The engineer is attempting to upload a file instead of a hash

Question 42

Which feature requires that network telemetry be enabled?

Options:

A.

per-interface stats

B.

SNMP trap notification

C.

Layer 2 device discovery

D.

central syslog system

Question 43

Which protocol provides the strongest throughput performance when using Cisco AnyConnect VPN?
Options:

A.

TLSv1.2

B.

TLSv1.1

C.

BJTLSv1

D.

DTLSv1

Question 44

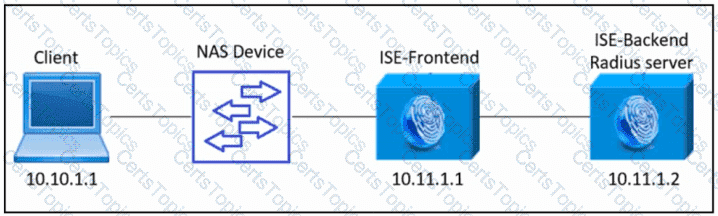
Refer to the exhibit. An engineer must configure a new Cisco ISE backend server as a RADIUS server to provide AAA for all access requests from the client to the ISE-Frontend server.

Which Cisco ISE configuration must be used?

Options:

A.

Set 10.11.1.2 as a network device in ISE-Frontend. Set port 1700/2083 for RADIUS authentication.

B.

Set 10.11.1.1 as the external RADIUS server in ISE-Frontend. Set ports 1812/1813 for authentication and accounting.

C.

Set 10.11.1.2 as the external RADIUS server in ISE-Frontend. Set ports 1812/1813 for authentication and accounting.

D.

Set 10.11.1.1 as a network device in ISE-Frontend. Set ports 1700/2083 for RADIUS authentication.

Question 45

Which Cisco security solution determines if an endpoint has the latest OS updates and patches installed on the system?

Options:

A.

Cisco Endpoint Security Analytics

B.

Cisco AMP for Endpoints

C.

Endpoint Compliance Scanner

D.

Security Posture Assessment Service

Question 46

A switch with Dynamic ARP Inspection enabled has received a spoofed ARP response on a trusted interface.

How does the switch behave in this situation?

Options:

A.

It forwards the packet after validation by using the MAC Binding Table.

B.

It drops the packet after validation by using the IP & MAC Binding Table.

C.

It forwards the packet without validation.

D.

It drops the packet without validation.

Question 47

An engineer is configuring Dropbox integration with Cisco Cloudlock. Which action must be taken before granting API access in the Dropbox admin console?

Options:

A.

Authorize Dropbox within the Platform settings in the Cisco Cloudlock portal.

B.

Add Dropbox to the Cisco Cloudlock Authentication and API section in the Cisco Cloudlock portal.

C.

Send an API request to Cisco Cloudlock from Dropbox admin portal.

D.

Add Cisco Cloudlock to the Dropbox admin portal.

Question 48

Which kind of API that is used with Cisco DNA Center provisions SSIDs, QoS policies, and update software versions on switches?

Options:

A.

Integration

B.

Intent

C.

Event

D.

Multivendor

Question 49

Which Cisco security solution provides patch management in the cloud?

Options:

A.

Cisco Umbrella

B.

Cisco ISE

C.

Cisco CloudLock

D.

Cisco Tetration

Question 50

Which open standard creates a framework for sharing threat intelligence in a machine-digestible format?

Options:

A.

OpenC2

B.

OpenlOC

C.

CybOX

D.

STIX

Question 51

An organization is implementing URL blocking using Cisco Umbrella. The users are able to go to some sites but other sites are not accessible due to an error. Why is the error occurring?

Options:

A.

Client computers do not have the Cisco Umbrella Root CA certificate installed.

B.

IP-Layer Enforcement is not configured.

C.

Intelligent proxy and SSL decryption is disabled in the policy.

D.

Client computers do not have an SSL certificate deployed from an internal CA server.

Question 52

What are two differences between a Cisco WSA that is running in transparent mode and one running in explicit mode? (Choose two)

Options:

A.

The Cisco WSA responds with its own IP address only if it is running in explicit mode.

B.

The Cisco WSA is configured in a web browser only if it is running in transparent mode.

C.

The Cisco WSA responds with its own IP address only if it is running in transparent mode.

D.

The Cisco WSA uses a Layer 3 device to redirect traffic only if it is running in transparent mode.

E.

When the Cisco WSA is running in transparent mode, it uses the WSA ' s own IP address as the HTTP request destination.

Question 53

Where are individual sites specified to be block listed in Cisco Umbrella?

Options:

A.

Application settings

B.

Security settings

C.

Destination lists

D.

Content categories

Question 54

Which Cisco security solution stops exfiltration using HTTPS?

Options:

A.

Cisco FTD

B.

Cisco AnyConnect

C.

Cisco CTA

D.

Cisco ASA

Question 55

What are the two types of managed Intercloud Fabric deployment models? (Choose two.)

Options:

A.

Public managed

B.

Service Provider managed

C.

Enterprise managed

D.

User managed

E.

Hybrid managed

Question 56

What is an advantage of the Cisco Umbrella roaming client?

Options:

A.

the ability to see all traffic without requiring TLS decryption

B.

visibility into IP-based threats by tunneling suspicious IP connections

C.

the ability to dynamically categorize traffic to previously uncategorized sites

D.

visibility into traffic that is destined to sites within the office environment

Question 57

An administrator configures new authorization policies within Cisco ISE and has difficulty profiling the devices. Attributes for the new Cisco IP phones that are profiled based on the RADIUS authentication are seen however the attributes for CDP or DHCP are not. What should the administrator do to address this issue?

Options:

A.

Configure the ip dhcp snooping trust command on the DHCP interfaces to get the information to Cisco ISE

B.

Configure the authentication port-control auto feature within Cisco ISE to identify the devices that are trying to connect

C.

Configure a service template within the switch to standardize the port configurations so that the correct information is sent to Cisco ISE

D.

Configure the device sensor feature within the switch to send the appropriate protocol information

Question 58

An organization has a Cisco ESA set up with policies and would like to customize the action assigned for

violations. The organization wants a copy of the message to be delivered with a message added to flag it as a

DLP violation. Which actions must be performed in order to provide this capability?

Options:

A.

deliver and send copies to other recipients

B.

quarantine and send a DLP violation notification

C.

quarantine and alter the subject header with a DLP violation

D.

deliver and add disclaimer text

Question 59

Which two configurations must be made on Cisco ISE and on Cisco TrustSec devices to force a session to be adjusted after a policy change is made? (Choose two)

Options:

A.

posture assessment

B.

aaa authorization exec default local

C.

tacacs-server host 10.1.1.250 key password

D.

aaa server radius dynamic-author

E.

CoA

Question 60

Which DevSecOps implementation process gives a weekly or daily update instead of monthly or quarterly in the applications?

Options:

A.

Orchestration

B.

CI/CD pipeline

C.

Container

D.

Security

Question 61

Drag and drop the capabilities from the left onto the correct technologies on the right.
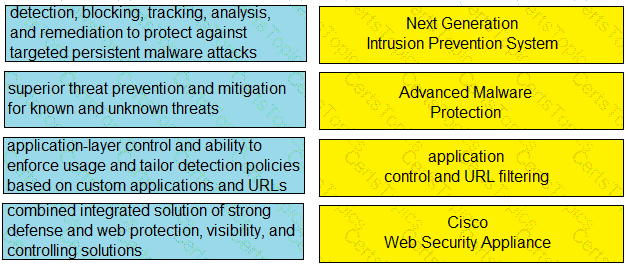
Options:

Question 62

A network security engineer must export packet captures from the Cisco FMC web browser while troubleshooting an issue. When navigating to the address < FMC IP > /capure/CAPI/pcap/test.pcap, an error 403: Forbidden is given instead of the PCAP file. Which action must the engineer take to resolve this issue?

Options:

A.

Disable the proxy setting on the browser

B.

Disable the HTTPS server and use HTTP instead

C.

Use the Cisco FTD IP address as the proxy server setting on the browser

D.

Enable the HTTPS server for the device platform policy

Question 63

Which function is performed by certificate authorities but is a limitation of registration authorities?

Options:

A.

accepts enrollment requests

B.

certificate re-enrollment

C.

verifying user identity

D.

CRL publishing

Question 64

In which two ways does a system administrator send web traffic transparently to the Web Security Appliance?

(Choose two)

Options:

A.

configure Active Directory Group Policies to push proxy settings

B.

configure policy-based routing on the network infrastructure

C.

reference a Proxy Auto Config file

D.

configure the proxy IP address in the web-browser settings

E.

use Web Cache Communication Protocol

Question 65

A malicious user gained network access by spoofing printer connections that were authorized using MAB on

four different switch ports at the same time. What two catalyst switch security features will prevent further

violations? (Choose two)

Options:

A.

DHCP Snooping

B.

802.1AE MacSec

C.

Port security

D.

IP Device track

E.

Dynamic ARP inspection

F.

Private VLANs

Question 66

An organization received a large amount of SPAM messages over a short time period. In order to take action on the messages, it must be determined how harmful the messages are and this needs to happen dynamically.

What must be configured to accomplish this?

Options:

A.

Configure the Cisco WSA to modify policies based on the traffic seen

B.

Configure the Cisco ESA to receive real-time updates from Talos

C.

Configure the Cisco WSA to receive real-time updates from Talos

D.

Configure the Cisco ESA to modify policies based on the traffic seen

Question 67

How many interfaces per bridge group does an ASA bridge group deployment support?

Options:

A.

up to 2

B.

up to 4

C.

up to 8

D.

up to 16

Question 68

Which security control is required for identifying and neutralizing malicious code that attempts to execute on an endpoint?

Options:

A.

EPP

B.

XDR

C.

SWG

D.

CASB

Question 69

Based on the NIST 800-145 guide, which cloud architecture is provisioned for exclusive use by a specific group of consumers from different organizations and may be owned, managed, and operated by one or more of those organizations?

Options:

A.

hybrid cloud

B.

private cloud

C.

community cloud

D.

public cloud

Question 70

What are two functions of TAXII in threat intelligence sharing? (Choose two.)

Options:

A.

determines the " what " of threat intelligence

B.

Supports STIX information

C.

allows users to describe threat motivations and abilities

D.

exchanges trusted anomaly intelligence information

E.

determines how threat intelligence information is relayed

Question 71

Which VPN technology supports a multivendor environment and secure traffic between sites?

Options:

A.

FlexVPN

B.

DMVPN

C.

SSL VPN

D.

GET VPN

Question 72

What is the benefit of integrating Cisco ISE with a MDM solution?

Options:

A.

It provides compliance checks for access to the network

B.

It provides the ability to update other applications on the mobile device

C.

It provides the ability to add applications to the mobile device through Cisco ISE

D.

It provides network device administration access

Question 73

How is DNS tunneling used to exfiltrate data out of a corporate network?

Options:

A.

It corrupts DNS servers by replacing the actual IP address with a rogue address to collect information or start other attacks.

B.

It encodes the payload with random characters that are broken into short strings and the DNS serverrebuilds the exfiltrated data.

C.

It redirects DNS requests to a malicious server used to steal user credentials, which allows further damageand theft on the network.

D.

It leverages the DNS server by permitting recursive lookups to spread the attack to other DNS servers.

Question 74

When a Cisco Secure Web Appliance checks a web request, what occurs if it is unable to match a user-defined policy?

Options:

A.

It applies the next identification profile policy.

B.

It applies the advanced policy.

C.

It applies the global policy.

D.

It blocks the request.

Question 75

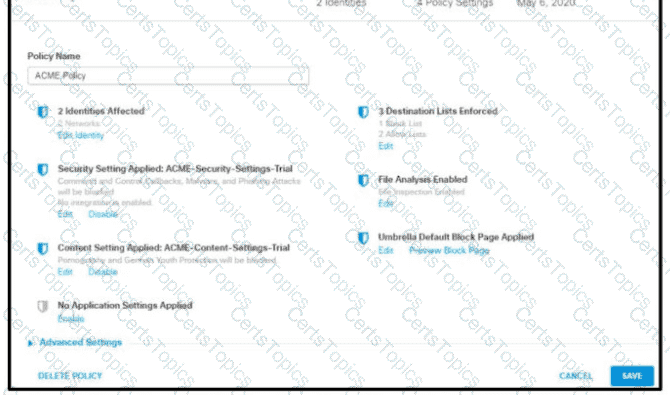
Refer to the exhibit.

How does Cisco Umbrella manage traffic that is directed toward risky domains?

Options:

A.

Traffic is proximed through the intelligent proxy.

B.

Traffic is managed by the security settings and blocked.

C.

Traffic is managed by the application settings, unhandled and allowed.

D.

Traffic is allowed but logged.

Question 76

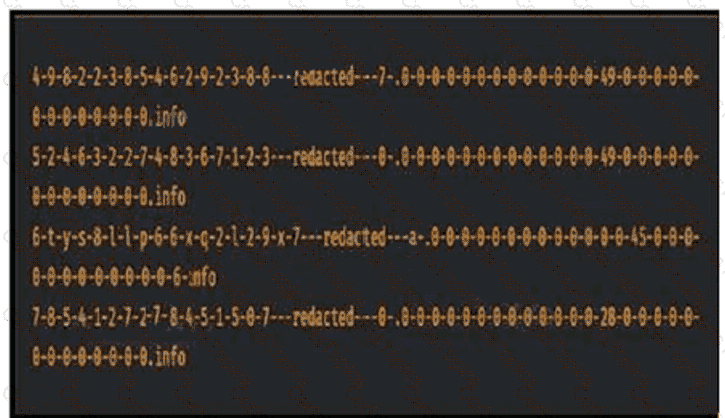
Refer to the exhibit.

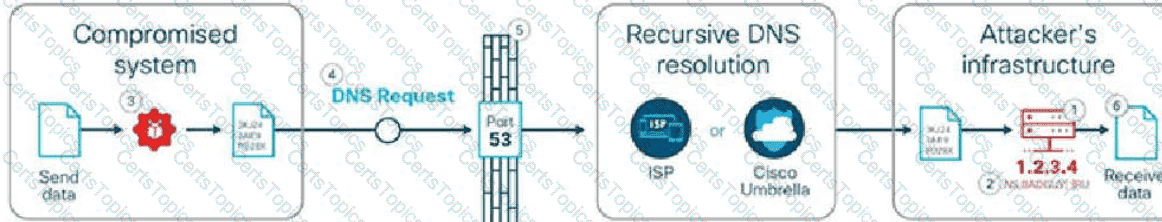
Consider that any feature of DNS requests, such as the length off the domain name

and the number of subdomains, can be used to construct models of expected behavior to which

observed values can be compared. Which type of malicious attack are these values associated with?

Options:

A.

Spectre Worm

B.

Eternal Blue Windows

C.

Heartbleed SSL Bug

D.

W32/AutoRun worm

Question 77

Which policy is used to capture host information on the Cisco Firepower Next Generation Intrusion Prevention

System?

Options:

A.

Correlation

B.

Intrusion

C.

Access Control

D.

Network Discovery

Question 78

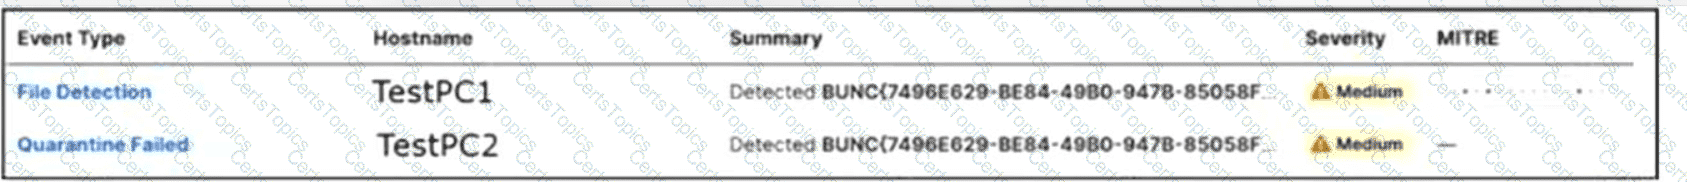
Refer to the exhibit.

A Cisco Secure Endpoint malware event shows that a file was convicted as malicious and that its remediation status is Quarantine Failed. Before escalating the incident, the analyst must determine what can be concluded from the available event data. What is occurring based on the logs?
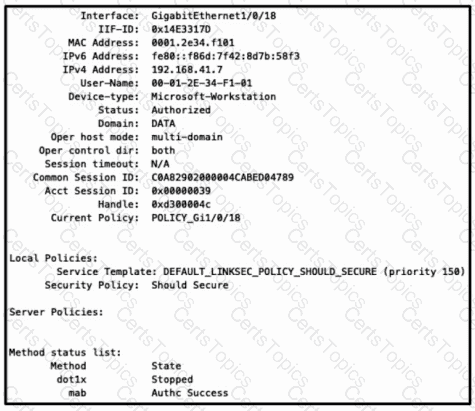
Options:

A.

The event data does not establish whether the threat remains present or was remediated through another mechanism.

B.

The failed-quarantine status proves that the endpoint was unable to apply the configured remediation policy.

C.

The failed-quarantine status proves that the file remained accessible to the operating system after the remediation attempt.

D.

The failed-quarantine status proves that the threat continued executing after the remediation attempt.

Question 79

Refer to the exhibit. Which configuration item makes it possible to have the AAA session on the network?

Options:

A.

aaa authorization exec default ise

B.

aaa authentication enable default enable

C.

aaa authorization network default group ise

D.

aaa authorization login console ise

Question 80

What is a benefit of using Cisco FMC over Cisco ASDM?

Options:

A.

Cisco FMC uses Java while Cisco ASDM uses HTML5.

B.

Cisco FMC provides centralized management while Cisco ASDM does not.

C.

Cisco FMC supports pushing configurations to devices while Cisco ASDM does not.

D.

Cisco FMC supports all firewall products whereas Cisco ASDM only supports Cisco ASA devices

Question 81

On Cisco Firepower Management Center, which policy is used to collect health modules alerts from managed

devices?

Options:

A.

health policy

B.

system policy

C.

correlation policy

D.

access control policy

E.

health awareness policy

Question 82

The security architect has concluded that the optimal mail flow positions the existing Cisco Secure Email Gateways as the first termination point for inbound messages, while Cisco Secure Email Threat Defense is positioned between the Secure Email Gateways and the cloud mail platform. The security engineer has been asked to configure the incoming-traffic domain setting in Cisco Secure Email Threat Defense so that it reflects the Secure Email Gateway handling inbound messages ahead of the service. Which domain configuration for incoming traffic must be selected to meet the requirement?

Options:

A.

Secondary Gateway

B.

Secondary with Additional Gateway

C.

Primary Gateway

D.

Primary with Additional Gateway

Question 83

When a transparent authentication fails on the Web Security Appliance, which type of access does the end user get?

Options:

A.

guest

B.

limited Internet

C.

blocked

D.

full Internet

Question 84

An organization wants to secure data in a cloud environment. Its security model requires that all users be

authenticated and authorized. Security configuration and posture must be continuously validated before access is granted or maintained to applications and data. There is also a need to allow certain application traffic and deny all other traffic by default. Which technology must be used to implement these requirements?

Options:

A.

Virtual routing and forwarding

B.

Microsegmentation

C.

Access control policy

D.

Virtual LAN

Question 85

A security engineer must protect endpoints when a file appears harmless during initial inspection but later shows malicious behavior. The solution must continuously observe process and file activity after execution and respond when a threat emerges. The infrastructure includes Cisco Secure Endpoint. Which feature must the engineer configure to meet the requirements?

Options:

A.

File Reputation

B.

Continuous Behavioral Monitoring

C.

Forensic Analysis

D.

System Process Protection

Question 86

Which API is used for Content Security?

Options:

A.

NX-OS API

B.

IOS XR API

C.

OpenVuln API

D.

AsyncOS API

Question 87

Which Secure Email Gateway implementation method segregates inbound and outbound email?

Options:

A.

Pair of logical listeners on a single physical interface with two unique logical IPv4 addresses and one IPv6 address

B.

One listener on one logical IPv4 address on a single logical interface

C.

Pair of logical IPv4 listeners and a pair of IPv6 listeners on two physically separate interfaces

D.

One listener on a single physical interface

Question 88

Which two Cisco ISE components must be configured for BYOD? (Choose two.)

Options:

A.

local WebAuth

B.

central WebAuth

C.

null WebAuth

D.

guest

E.

dual

Question 89

Which Linux system call loads an eBPF program and manages eBPF maps within the kernel?

Options:

A.

perf_event_open()

B.

ioctl()

C.

prctl()

D.

bpf()

Question 90

Which Cisco ISE feature helps to detect missing patches and helps with remediation?

Options:

A.

posture assessment

B.

profiling policy

C.

authentication policy

D.

enabling probes

Question 91

Which action controls the amount of URI text that is stored in Cisco WSA logs files?

Options:

A.

Configure the datasecurityconfig command

B.

Configure the advancedproxyconfig command with the HTTPS subcommand

C.

Configure a small log-entry size.

D.

Configure a maximum packet size.

Question 92

Refer to the exhibit.

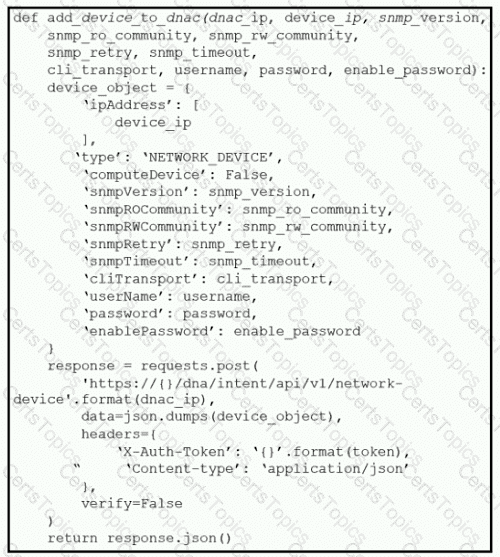
What is the result of this Python script of the Cisco DNA Center API?

Options:

A.

adds authentication to a switch

B.

adds a switch to Cisco DNA Center

C.

receives information about a switch

D.

deletes a switch from Cisco DNA Center

Question 93

An attacker needs to perform reconnaissance on a target system to help gain access to it. The system has weak passwords, no encryption on the VPN links, and software bugs on the system’s applications. Which

vulnerability allows the attacker to see the passwords being transmitted in clear text?

Options:

A.

weak passwords for authentication

B.

unencrypted links for traffic

C.

software bugs on applications

D.

improper file security

Question 94

Which feature within Cisco ISE verifies the compliance of an endpoint before providing access to the

network?

Options:

A.

Posture

B.

Profiling

C.

pxGrid

D.

MAB

Question 95

Which two key and block sizes are valid for AES? (Choose two)

Options:

A.

64-bit block size, 112-bit key length

B.

64-bit block size, 168-bit key length

C.

128-bit block size, 192-bit key length

D.

128-bit block size, 256-bit key length

E.

192-bit block size, 256-bit key length

Question 96

What are two recommended approaches to stop DNS tunneling for data exfiltration and command and control call backs? (Choose two.)

Options:

A.

Use intrusion prevention system.

B.

Block all TXT DNS records.

C.

Enforce security over port 53.

D.

Use next generation firewalls.

E.

Use Cisco Umbrella.

Question 97

When a Cisco WSA checks a web request, what occurs if it is unable to match a user-defined policy?

Options:

A.

It blocks the request.

B.

It applies the global policy.

C.

It applies the next identification profile policy.

D.

It applies the advanced policy.

Question 98

Which VMware platform does Cisco ACI integrate with to provide enhanced visibility, provide policy integration and deployment, and implement security policies with access lists?

Options:

A.

VMware APIC

B.

VMwarevRealize

C.

VMware fusion

D.

VMware horizons

Question 99

A large retail enterprise is deploying Cisco Secure Private Access to enable remote employees to reach internal applications without manual intervention. The IT department requires a seamless, zero-touch enrollment process in which users are registered and authenticated transparently without requiring end-user action. The architecture must support robust high availability for back-end connectivity to ensure continuous access to private resources. Which configuration approach must the administrator implement to meet the requirement?

Options:

A.

Implement ZTA with Certificate Enrollment and multiple Connector Groups associated with the private resource.

B.

Configure ZTA with SAML Enrollment and multiple Connector Groups associated with the private resource.

C.

Define a VPN Machine Tunnel with Certificate Enrollment and Connector Groups associated with the private resource.

D.

Apply ZTA with SAML Enrollment, including passwordless enrollment, and a single Connector associated with the private resource.

Question 100

An organization is implementing URL blocking using Cisco Umbrella. The users are able to go to some sites

but other sites are not accessible due to an error. Why is the error occurring?

Options:

A.

Client computers do not have the Cisco Umbrella Root CA certificate installed.

B.

IP-Layer Enforcement is not configured.

C.

Client computers do not have an SSL certificate deployed from an internal CA server.

D.

Intelligent proxy and SSL decryption is disabled in the policy

Question 101

Which two products are used to forecast capacity needs accurately in real time? (Choose two.)

Options:

A.

Cisco Secure Workload

B.

Cisco Umbrella

C.

Cisco Workload Optimization Manager

D.

Cisco AppDynamics

E.

Cisco Cloudlock

Question 102

Which endpoint solution protects a user from a phishing attack?

Options:

A.

Cisco Identity Services Engine

B.

Cisco AnyConnect with ISE Posture module

C.

Cisco AnyConnect with Network Access Manager module

D.

Cisco AnyConnect with Umbrella Roaming Security module

Question 103

An engineer is adding a Cisco DUO solution to the current TACACS+ deployment using Cisco ISE. The engineer wants to authenticate users using their account when they log into network devices. Which action accomplishes this task?

Options:

A.

Configure Cisco DUO with the external Active Directory connector and tie it to the policy set within Cisco ISE.

B.

Install and configure the Cisco DUO Authentication Proxy and configure the identity source sequence within Cisco ISE

C.

Create an identity policy within Cisco ISE to send all authentication requests to Cisco DUO.

D.

Modify the current policy with the condition MFASourceSequence DUO=true in the authorization conditions within Cisco ISE

Question 104

Which algorithm provides encryption and authentication for data plane communication?

Options:

A.

AES-GCM

B.

SHA-96

C.

AES-256

D.

SHA-384

Question 105

Which Cisco ASA deployment model is used to filter traffic between hosts in the same IP subnet using higher-level protocols without readdressing the network?

Options:

A.

routed mode

B.

transparent mode

C.

single context mode

D.

multiple context mode

Question 106

What is a feature of an endpoint detection and response solution?

Options:

A.

Preventing attacks by identifying harmful events with machine learning and conduct-based defense

B.

Rapidly and consistently observing and examining data to mitigate threats

C.

Capturing and clarifying data on email, endpoints, and servers to mitigate threats

D.

Ensuring the security of network devices by choosing which devices are allowed to reach the network

Question 107

A network engineer is configuring a Cisco Catalyst switch. The network engineer must prevent traffic on the network from being interrupted by broadcast packets flooding the network using a predefined threshold. What must be configured on the switch?

Options:

A.

DHCP Snooping

B.

Embedded Event Monitoring

C.

Storm Control

D.

Loop Guard

Question 108

What is a feature of NetFlow Secure Event Logging?

Options:

A.

It exports only records that indicate significant events in a flow.

B.

It filters NSEL events based on the traffic and event type through RSVP.

C.

It delivers data records to NSEL collectors through NetFlow over TCP only.

D.

It supports v5 and v8 templates.

Question 109

Which technology provides a combination of endpoint protection endpoint detection, and response?

Options:

A.

Cisco AMP

B.

Cisco Talos

C.

Cisco Threat Grid

D.

Cisco Umbrella

Question 110

Refer to the exhibit.

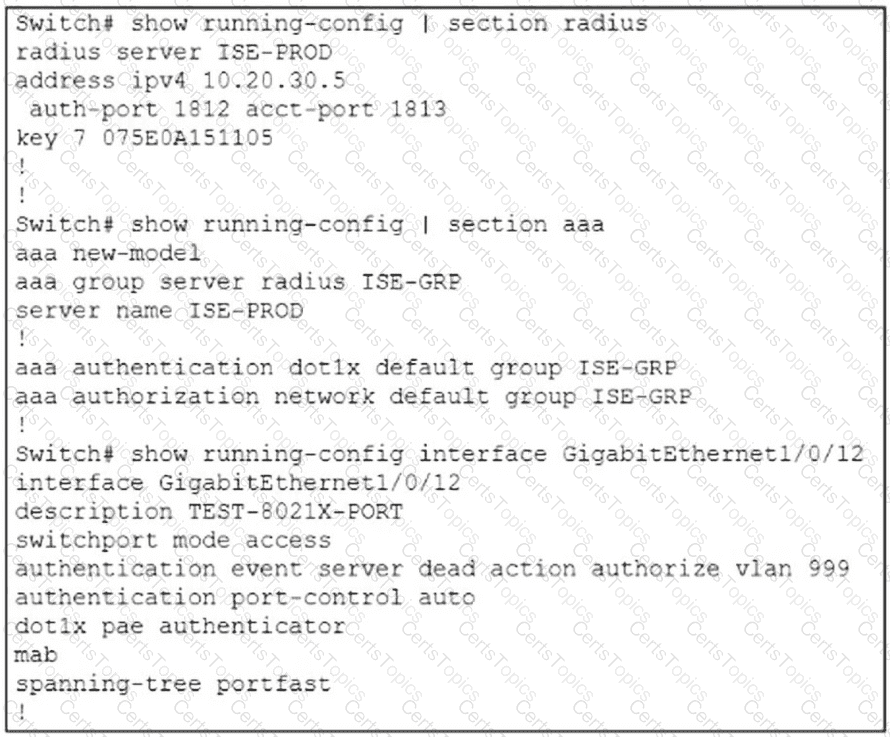
A newly installed stack of Cisco Catalyst switches has been integrated with Cisco ISE for 802.1X port control and downloadable access control list (dACL) enforcement. Test workstations authenticate successfully, but the expected dACL never appears in the port configuration, leaving all traffic unrestricted. Packet captures confirm that Cisco ISE transmits the correct attributes, yet the switches classify them as “unknown” and ignore the instructions. A review of the running configuration shows complete AAA and 802.1X configuration. Which configuration command must be added to resolve the issue?

Options:

A.

radius-server vsa send accounting

B.

aaa authorization network default group radius

C.

radius-server vsa send authentication

D.

aaa authorization exec default group radius

Question 111

An engineer is configuring their router to send NetfFow data to Stealthwatch which has an IP address of 1 1 11 using the flow record Stea!thwatch406397954 command Which additional command is required to complete the flow record?

Options:

A.

transport udp 2055

B.

match ipv4 ttl

C.

cache timeout active 60

D.

destination 1.1.1.1

Question 112

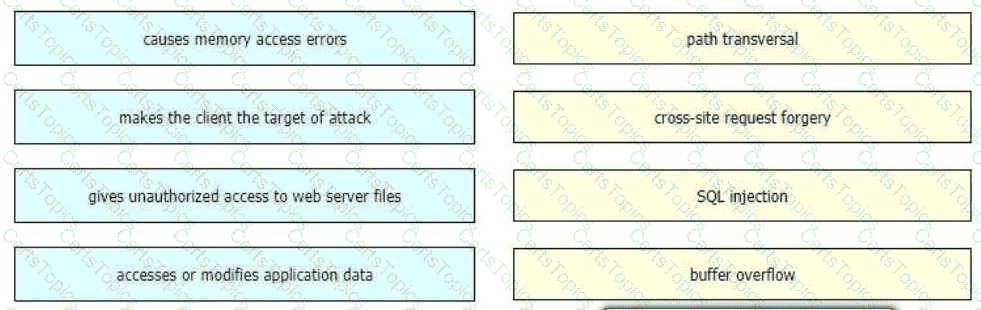
Drag and drop the exploits from the left onto the type of security vulnerability on the right.
Options:

Question 113

What is a difference between GRE over IPsec and IPsec with crypto map?

Options:

A.

Multicast traffic is supported by IPsec with crypto map.

B.

GRE over IPsec supports non-IP protocols.

C.

GRE provides its own encryption mechanism.

D.

IPsec with crypto map oilers better scalability.

Question 114

Which two fields are defined in the NetFlow flow? (Choose two)

Options:

A.

type of service byte

B.

class of service bits

C.

Layer 4 protocol type

D.

destination port

E.

output logical interface

Question 115

What is a prerequisite when integrating a Cisco ISE server and an AD domain?

Options:

A.

Place the Cisco ISE server and the AD server in the same subnet

B.

Configure a common administrator account

C.

Configure a common DNS server

D.

Synchronize the clocks of the Cisco ISE server and the AD server

Question 116

Refer to the exhibit.

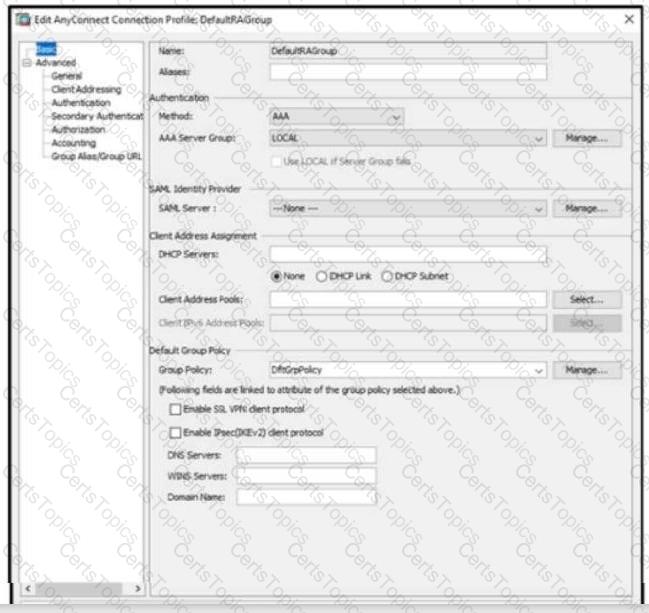
When configuring a remote access VPN solution terminating on the Cisco ASA, an administrator would like to utilize an external token authentication mechanism in conjunction with AAA authentication using machine

certificates. Which configuration item must be modified to allow this?

Options:

A.

Group Policy

B.

Method

C.

SAML Server

D.

DHCP Servers

Question 117

Which action must be taken in the AMP for Endpoints console to detect specific MD5 signatures on endpoints and then quarantine the files?

Options:

A.

Configure an advanced custom detection list.

B.

Configure an IP Block & Allow custom detection list

C.

Configure an application custom detection list

D.

Configure a simple custom detection list

Question 118

For which two conditions can an endpoint be checked using ISE posture assessment? (Choose two)

Options:

A.

Windows service

B.

computer identity

C.

user identity

D.

Windows firewall

E.

default browser

Question 119

Which option is the main function of Cisco Firepower impact flags?

Options:

A.

They alert administrators when critical events occur.

B.

They highlight known and suspected malicious IP addresses in reports.

C.

They correlate data about intrusions and vulnerability.

D.

They identify data that the ASA sends to the Firepower module.

Question 120

Using Cisco Cognitive Threat Analytics, which platform automatically blocks risky sites, and test unknown sites for hidden advanced threats before allowing users to click them?

Options:

A.

Cisco Identity Services Engine (ISE)

B.

Cisco Enterprise Security Appliance (ESA)

C.

Cisco Web Security Appliance (WSA)

D.

Cisco Advanced Stealthwatch Appliance (ASA)

Question 121

What is the recommendation in a zero-trust model before granting access to corporate applications and

resources?

Options:

A.

to use multifactor authentication

B.

to use strong passwords

C.

to use a wired network, not wireless

D.

to disconnect from the network when inactive

Question 122

What is the most commonly used protocol for network telemetry?

Options:

A.

SMTP

B.

SNMP

C.

TFTP

D.

NctFlow

Question 123

Which standard is used to automate exchanging cyber threat information?

Options:

A.

TAXII

B.

MITRE

C.

IoC

D.

STIX

Question 124

Which solution combines Cisco IOS and IOS XE components to enable administrators to recognize applications, collect and send network metrics to Cisco Prime and other third-party management tools, and prioritize application traffic?

Options:

A.

Cisco Catalyst Center

B.

Cisco Security Intelligence

C.

Cisco Model Driven Telemetry

D.

Cisco Application Visibility and Control

Question 125

Which CLI command is used to enable URL filtering support for shortened URLs on the Cisco Secure Email Gateway?

Options:

A.

outbreakconfig

B.

websecurityconfig

C.

webadvancedconfig

D.

websecurityadvancedconfig

Question 126

A large enterprise is currently managing a hybrid environment consisting of a private data center and multiple public cloud providers. The security engineering team is concerned about “Shadow IT” and the lack of visibility into unauthorized cloud services being used by various departments. The architect must select a solution that provides comprehensive discovery of cloud application usage and assesses the risk of each service based on industry certifications. Which technical solution must be used to provide cross-environment visibility?

Options:

A.

EDR

B.

CASB

C.

Secure Firewall

D.

CWPP

Question 127

What is the purpose of the My Devices Portal in a Cisco ISE environment?

Options:

A.

to register new laptops and mobile devices

B.

to request a newly provisioned mobile device

C.

to provision userless and agentless systems

D.

to manage and deploy antivirus definitions and patches on systems owned by the end user

Question 128

Which statement describes a serverless application?

Options:

A.

The application delivery controller in front of the server farm designates on which server the application runs each time.

B.

The application runs from an ephemeral, event-triggered, and stateless container that is fully managed by a cloud provider.

C.

The application is installed on network equipment and not on physical servers.

D.

The application runs from a containerized environment that is managed by Kubernetes or Docker Swarm.

Question 129

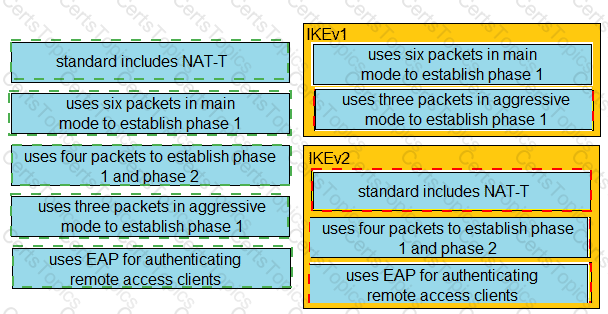
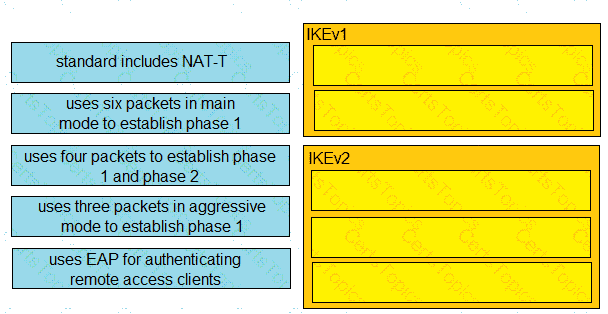
Drag and drop the descriptions from the left onto the correct protocol versions on the right.
Options:

Question 130

What is the primary benefit of deploying an ESA in hybrid mode?

Options:

A.

You can fine-tune its settings to provide the optimum balance between security and performance for your environment

B.

It provides the lowest total cost of ownership by reducing the need for physical appliances

C.

It provides maximum protection and control of outbound messages

D.

It provides email security while supporting the transition to the cloud

Question 131

Which policy represents a shared set of features or parameters that define the aspects of a managed device that are likely to be similar to other managed devices in a deployment?

Options:

A.

Group Policy

B.

Access Control Policy

C.

Device Management Policy

D.

Platform Service Policy

Question 132

Which command enables 802.1X globally on a Cisco switch?

Options:

A.

dot1x system-auth-control

B.

dot1x pae authenticator

C.

authentication port-control aut

D.

aaa new-model

Question 133

Which Cisco ISE service checks the compliance of endpoints before allowing the endpoints to connect to

the network?

Options:

A.

posture

B.

profiler

C.

Cisco TrustSec

D.

Threat Centric NAC

Question 134

What are two rootkit types? (Choose two)

Options:

A.

registry

B.

virtual

C.

bootloader

D.

user mode

E.

buffer mode

Question 135

Which Cisco WSA feature supports access control using URL categories?

Options:

A.

transparent user identification

B.

SOCKS proxy services

C.

web usage controls

D.

user session restrictions

Question 136

Refer to the exhibit.

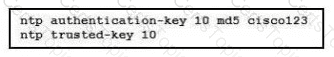
A network engineer is testing NTP authentication and realizes that any device synchronizes time with this router and that NTP authentication is not enforced What is the cause of this issue?

Options:

A.

The key was configured in plain text.

B.

NTP authentication is not enabled.

C.

The hashing algorithm that was used was MD5. which is unsupported.

D.

The router was not rebooted after the NTP configuration updated.

Question 137

An organization is receiving SPAM emails from a known malicious domain. What must be configured in order to

prevent the session during the initial TCP communication?

Options:

A.

Configure the Cisco ESA to drop the malicious emails

B.

Configure policies to quarantine malicious emails

C.

Configure policies to stop and reject communication

D.

Configure the Cisco ESA to reset the TCP connection

Question 138

Which solution for remote workers enables protection, detection, and response on the endpoint against known and unknown threats?

Options:

A.

Cisco AMP for Endpoints

B.

Cisco AnyConnect

C.

Cisco Umbrella

D.

Cisco Duo

Question 139

What is the Cisco API-based broker that helps reduce compromises, application risks, and data breaches in an environment that is not on-premise?

Options:

A.

Cisco Cloudlock

B.

Cisco Umbrella

C.

Cisco AMP

D.

Cisco App Dynamics

Question 140

An organization plans to upgrade its current email security solutions, and an engineer must deploy Cisco Secure Email. The requirements for the upgrade are:

Implement Data Loss Prevention

Implement mail encryption

Integrate with an existing Cisco IronPort Secure Email Gateway solution

Which Cisco Secure Email license is needed to accomplish this task?

Options:

A.

Cisco Secure Email Outbound Essentials

B.

Cisco Secure Email Phishing Defense

C.

Cisco Secure Email Domain Protection

D.

Cisco Secure Email Inbound Essentials

Question 141

What are two Detection and Analytics Engines of Cognitive Threat Analytics? (Choose two)

Options:

A.

data exfiltration

B.

command and control communication

C.

intelligent proxy

D.

snort

E.

URL categorization

Question 142

What do tools like Jenkins, Octopus Deploy, and Azure DevOps provide in terms of application and

infrastructure automation?

Options:

A.

continuous integration and continuous deployment

B.

cloud application security broker

C.

compile-time instrumentation

D.

container orchestration

Question 143

A network administrator is using the Cisco ESA with AMP to upload files to the cloud for analysis. The network

is congested and is affecting communication. How will the Cisco ESA handle any files which need analysis?

Options:

A.

AMP calculates the SHA-256 fingerprint, caches it, and periodically attempts the upload.

B.

The file is queued for upload when connectivity is restored.

C.

The file upload is abandoned.

D.

The ESA immediately makes another attempt to upload the file.

Question 144

What does Cisco AMP for Endpoints use to help an organization detect different families of malware?

Options:

A.

Ethos Engine to perform fuzzy fingerprinting

B.

Tetra Engine to detect malware when me endpoint is connected to the cloud

C.

Clam AV Engine to perform email scanning

D.

Spero Engine with machine learning to perform dynamic analysis

Question 145

An engineer recently completed the system setup on a Cisco WSA Which URL information does the system send to SensorBase Network servers?

Options:

A.

Summarized server-name information and MD5-hashed path information

B.

complete URL,without obfuscating the path segments

C.

URL information collected from clients that connect to the Cisco WSA using Cisco AnyConnect

D.

none because SensorBase Network Participation is disabled by default

Question 146

Which problem Is solved by deploying a multicontext firewall?

Options:

A.

overlapping IP addressing plan

B.

more secure policy

C.

resilient high availability design

D.

faster inspection

Question 147

Refer to the exhibit.

What does the API key do while working with

Options:

A.

displays client ID

B.

HTTP authorization

C.

Imports requests

D.

HTTP authentication

Question 148

An engineer is implementing NAC for LAN users on a segmented network. The engineer confirms that the device of each user is supported and the Cisco switch configuration is correct.

Which configuration should be made next to ensure there are no authentication issues?

Options:

A.

Disable the host firewall.

B.

Enable TACACS+ on the switch.

C.

Open TCP port 49.

D.

Permit UDP port 1812.

Question 149

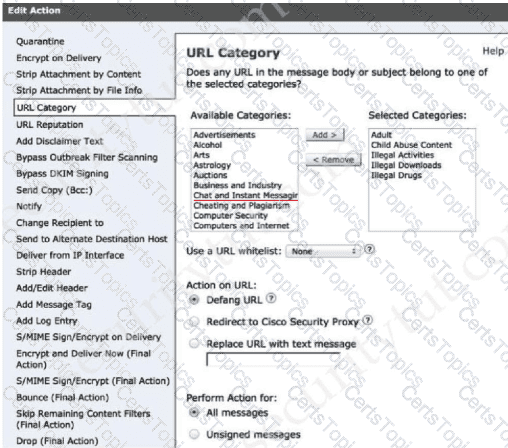
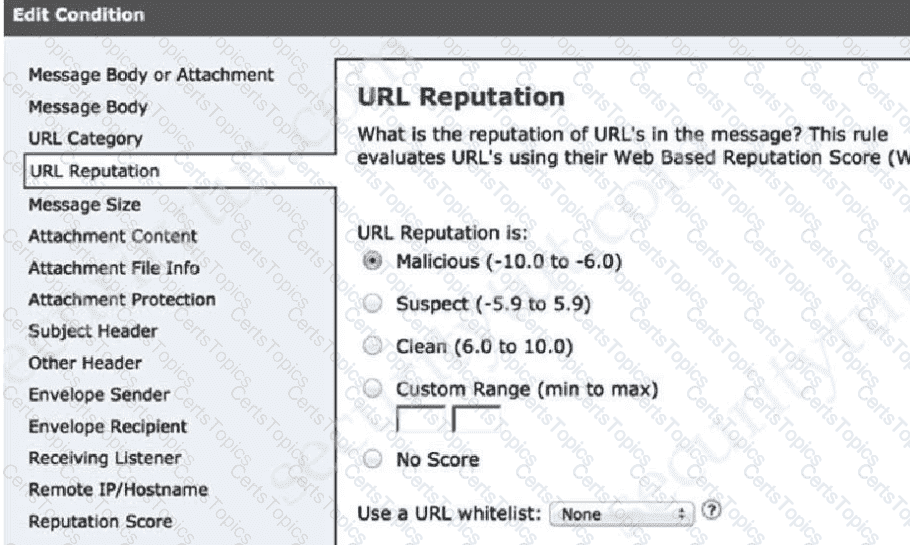
A network administrator is configuring a rule in an access control policy to block certain URLs and selects the “Chat and Instant Messaging” category. Which reputation score should be selected to accomplish this goal?

Options:

A.

1

B.

3

C.

5

D.

10

Question 150

Which two features are used to configure Cisco ESA with a multilayer approach to fight viruses and malware?

(Choose two)

Options:

A.

Sophos engine

B.

white list

C.

RAT

D.

outbreak filters

E.

DLP

Question 151

Which solution is more secure than the traditional use of a username and password and encompasses at least two of the methods of authentication?

Options:

A.

single-sign on

B.

RADIUS/LDAP authentication

C.

Kerberos security solution

D.

multifactor authentication

Question 152

An engineer needs to detect and quarantine a file named abc424400664 zip based on the MD5 signature of the file using the Outbreak Control list feature within Cisco Advanced Malware Protection (AMP) for Endpoints The configured detection method must work on files of unknown disposition Which Outbreak Control list must be configured to provide this?

Options:

A.

Blocked Application

B.

Simple Custom Detection

C.

Advanced Custom Detection

D.

Android Custom Detection

Question 153

Which solution combines Cisco IOS and IOS XE components to enable administrators to recognize

applications, collect and send network metrics to Cisco Prime and other third-party management tools, and prioritize application traffic?

Options:

A.

Cisco Security Intelligence

B.

Cisco Application Visibility and Control

C.

Cisco Model Driven Telemetry

D.

Cisco DNA Center

Question 154

What is a key difference between Cisco Firepower and Cisco ASA?

Options:

A.

Cisco ASA provides access control while Cisco Firepower does not.

B.

Cisco Firepower provides identity-based access control while Cisco ASA does not.

C.

Cisco Firepower natively provides intrusion prevention capabilities while Cisco ASA does not.

D.

Cisco ASA provides SSL inspection while Cisco Firepower does not.

Question 155

Why would a user choose an on-premises ESA versus the CES solution?

Options:

A.

Sensitive data must remain onsite.

B.

Demand is unpredictable.

C.

The server team wants to outsource this service.

D.

ESA is deployed inline.

Question 156

Which type of protection encrypts RSA keys when they are exported and imported?

Options:

A.

file

B.

passphrase

C.

NGE

D.

nonexportable

Question 157

Refer to the exhibit.

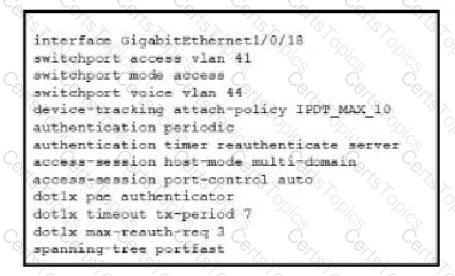
Refer to the exhibit. A Cisco ISE administrator adds a new switch to an 802.1X deployment and has difficulty with some endpoints gaining access.

Most PCs and IP phones can connect and authenticate using their machine certificate credentials. However printer and video cameras cannot base d on the interface configuration provided, what must be to get these devices on to the network using Cisco ISE for authentication and authorization while maintaining security controls?

Options:

A.

Change the default policy in Cisco ISE to allow all devices not using machine authentication .

B.

Enable insecure protocols within Cisco ISE in the allowed protocols configuration.

C.

Configure authentication event fail retry 2 action authorize vlan 41 on the interface

D.

Add mab to the interface configuration.

Question 158

What are two benefits of workload security? (Choose two.)

Options:

A.

Tracked application security

B.

Automated patching

C.

Reduced attack surface

D.

Scalable security policies

E.

Workload modeling

Question 159

Which two methods must be used to add switches into the fabric so that administrators can control how switches are added into DCNM for private cloud management? (Choose two.)

Options:

A.

Cisco Cloud Director

B.

Cisco Prime Infrastructure

C.

PowerOn Auto Provisioning

D.

Seed IP

E.

CDP AutoDiscovery

Question 160

Why is it important to patch endpoints consistently?

Options:

A.

Patching reduces the attack surface of the infrastructure.

B.

Patching helps to mitigate vulnerabilities.

C.

Patching is required per the vendor contract.

D.

Patching allows for creating a honeypot.

Question 161

Which two protocols must be configured to authenticate end users to the Web Security Appliance? (Choose two.)
Options:

A.

NTLMSSP

B.

Kerberos

C.

CHAP

D.

TACACS+

E.

RADIUS

Question 162

Refer to the exhibit. Traffic is not passing through IPsec site-to-site VPN on the Secure Firewall Threat Defense appliance. What is causing this issue?

Options:

A.

No split-tunnel policy is defined on the Secure Firewall Threat Defense appliance.

B.

Site-to-site VPN preshared keys are mismatched.

C.

The access control policy is not allowing VPN traffic in.

D.

Site-to-site VPN peers are using different encryption algorithms.

Question 163

Which characteristic is unique to a Cisco WSAv as compared to a physical appliance?

Options:

A.

supports VMware vMotion on VMware ESXi

B.

requires an additional license

C.

performs transparent redirection

D.

supports SSL decryption

Question 164

An organization is using DNS services for their network and want to help improve the security of the DNS infrastructure. Which action accomplishes this task?

Options:

A.

Use DNSSEC between the endpoints and Cisco Umbrella DNS servers.

B.

Modify the Cisco Umbrella configuration to pass queries only to non-DNSSEC capable zones.

C.

Integrate Cisco Umbrella with Cisco CloudLock to ensure that DNSSEC is functional.

D.

Configure Cisco Umbrella and use DNSSEC for domain authentication to authoritative servers.

Question 165

Which Cisco security solution secures public, private, hybrid, and community clouds?

Options:

A.

Cisco ISE

B.

Cisco ASAv

C.

Cisco Cloudlock

D.

Cisco pxGrid

Question 166

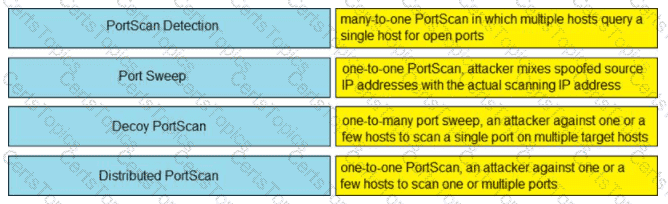
Drag and drop the Firepower Next Generation Intrusion Prevention System detectors from the left onto the correct definitions on the right.
Options:

Question 167

An organization has a requirement to collect full metadata information about the traffic going through their AWS cloud services They want to use this information for behavior analytics and statistics Which two actions must be taken to implement this requirement? (Choose two.)

Options:

A.

Configure Cisco ACI to ingest AWS information.

B.

Configure Cisco Thousand Eyes to ingest AWS information.

C.

Send syslog from AWS to Cisco Stealthwatch Cloud.

D.

Send VPC Flow Logs to Cisco Stealthwatch Cloud.

E.

Configure Cisco Stealthwatch Cloud to ingest AWS information

Question 168

What is a description of microsegmentation?

Options:

A.

Environments apply a zero-trust model and specify how applications on different servers or containers can communicate

B.

Environments deploy a container orchestration platform, such as Kubernetes, to manage the application delivery

C.

Environments implement private VLAN segmentation to group servers with similar applications.

D.

Environments deploy centrally managed host-based firewall rules on each server or container

Question 169

Which CoA response code is sent if an authorization state is changed successfully on a Cisco IOS device?

Options:

A.

CoA-NCL

B.

CoA-NAK

C.

СоА-МАВ

D.

CoA-ACK

Question 170

A security policy administrator configures a Cisco Secure Access SIA DNS policy to block all social media categories for the Marketing Active Directory group. While testing from one of the user machines, access to the domain is allowed. When searching for this domain in User Activity Search, no queries for that specific domain are returned. Consider these facts:

    The test user is part of the Marketing Active Directory group.

    The domain socialmediaexample.org belongs to the social media category.

    The user is configured with the Umbrella Roaming Client for DNS redirection.

    All other social media websites are properly blocked for the same user and match the correct policy.

Which configuration must the administrator implement in Cisco Secure Access to meet the requirement?

Options:

A.

Enable HTTPS inspection in the web policy because this is an HTTPS site.

B.

Add socialmediaexample.org to the External Domains list.

C.

Enable the intelligent proxy to identify this domain properly.

D.

Add socialmediaexample.org to the Internal Domains list.

Question 171

An MDM provides which two advantages to an organization with regards to device management? (Choose two)

Options:

A.

asset inventory management

B.

allowed application management

C.

Active Directory group policy management

D.

network device management

E.

critical device management

Question 172

A recent change left network engineers unable to SSH into a branch Cisco Catalyst switch. The engineer confirms that the TACACS server group TACACS-GROUP is defined but unreachable. There is no fallback to the local database when TACACS+ is unavailable. Security policy requires TACACS+ as the primary authentication method with automatic fallback to local accounts. Which configuration command must be added to resolve the issue?

Options:

A.

aaa authentication login ssh LOCAL TACACS-GROUP

B.

aaa authentication login group TACACS-GROUP local

C.

aaa authentication login default group TACACS-GROUP local

D.

aaa authentication serial console TACACS-GROUP LOCAL

Question 173

What are two functions of secret key cryptography? (Choose two)

Options:

A.

key selection without integer factorization

B.

utilization of different keys for encryption and decryption

C.

utilization of large prime number iterations

D.

provides the capability to only know the key on one side

E.

utilization of less memory

Question 174

For Cisco IOS PKI, which two types of Servers are used as a distribution point for CRLs? (Choose two)

Options:

A.

SDP

B.

LDAP

C.

subordinate CA

D.

SCP

E.

HTTP

Question 175

What must be enabled to secure SaaS-based applications?

Options:

A.

modular policy framework

B.

two-factor authentication

C.

application security gateway

D.

end-to-end encryption

Question 176

Which solution supports high availability in routed or transparent mode as well as in northbound and

southbound deployments?

Options:

A.

Cisco FTD with Cisco ASDM

B.

Cisco FTD with Cisco FMC

C.

Cisco Firepower NGFW physical appliance with Cisco. FMC

D.

Cisco Firepower NGFW Virtual appliance with Cisco FMC

Question 177

A mall provides security services to customers with a shared appliance. The mall wants separation of

management on the shared appliance. Which ASA deployment mode meets these needs?

Options:

A.

routed mode

B.

transparent mode

C.

multiple context mode

D.

multiple zone mode

Question 178

An engineer is configuring device-hardening on a router in order to prevent credentials from being seen

if the router configuration was compromised. Which command should be used?

Options:

A.

service password-encryption

B.

username < username > privilege 15 password < password >

C.

service password-recovery

D.

username < username > password < password >

Question 179

When NetFlow is applied to an interface, which component creates the flow monitor cache that is used

to collect traffic based on the key and nonkey fields in the configured record?

Options:

A.

records

B.

flow exporter

C.

flow sampler

D.

flow monitor

Question 180

What is managed by Cisco Security Manager?

Options:

A.

access point

B.

WSA

C.

ASA

D.

ESA

Question 181

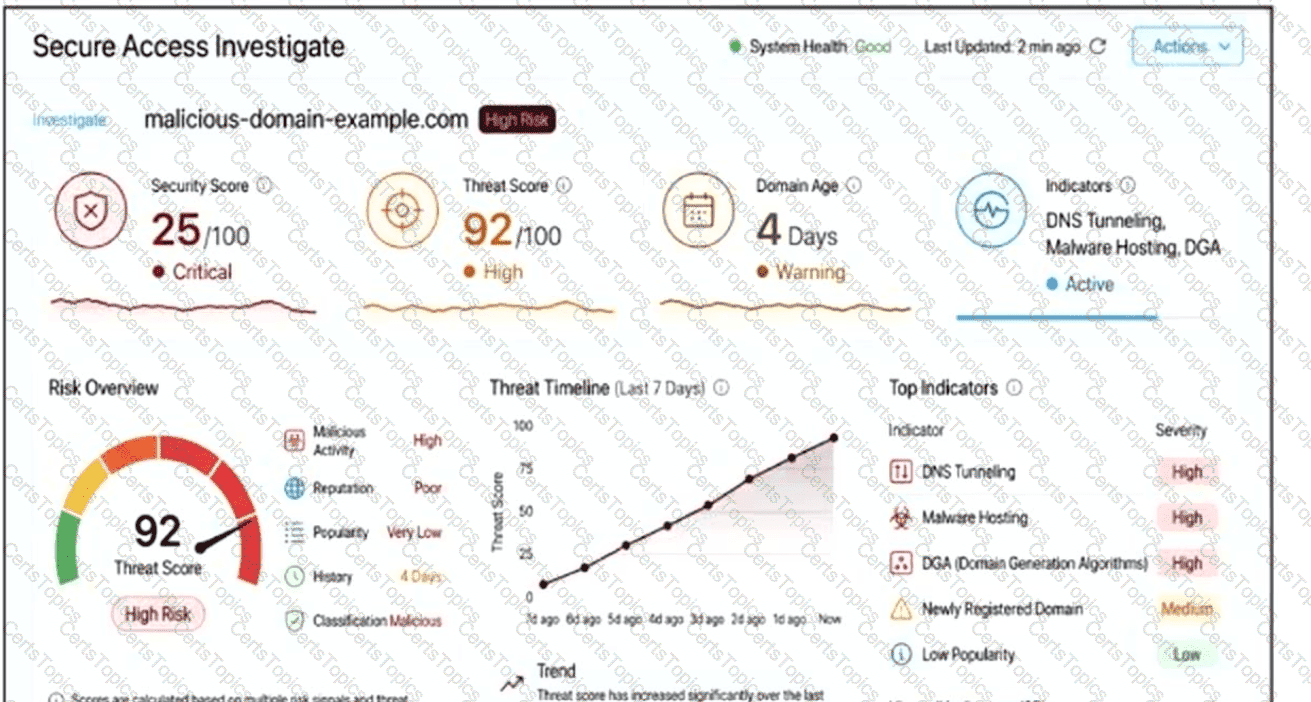
Refer to the exhibit.

What conclusion should an administrator draw about the URL malicious-domain-example.com?

Options:

A.

The domain is blocked solely because it is newly registered, regardless of the Threat Score.

B.

The domain is a legacy site that has been compromised, as indicated by its domain age.

C.

The domain is safe because its Security Score is 25/100.

D.

The high Threat Score together with DNS tunneling, malware hosting, and DGA indicators shows active malicious behavior.

Question 182

Which Cisco product provides proactive endpoint protection and allows administrators to centrally manage the

deployment?

Options:

A.

NGFW

B.

AMP

C.

WSA

D.

ESA

Question 183

What is a feature of the open platform capabilities of Cisco DNA Center?

Options:

A.

intent-based APIs

B.

automation adapters

C.

domain integration

D.

application adapters

Question 184

What is the primary role of the Cisco Email Security Appliance?

Options:

A.

Mail Submission Agent

B.

Mail Transfer Agent

C.

Mail Delivery Agent

D.

Mail User Agent

Question 185

Which capability is provided by application visibility and control?

Options:

A.

reputation filtering

B.

data obfuscation

C.

data encryption

D.

deep packet inspection

Question 186

What is the function of the crypto is a kmp key cisc406397954 address 0.0.0.0 0.0.0.0 command when establishing an IPsec VPN tunnel?

Options:

A.

It defines what data is going to be encrypted via the VPN

B.

lt configures the pre-shared authentication key

C.

It prevents all IP addresses from connecting to the VPN server.

D.

It configures the local address for the VPN server.

Question 187

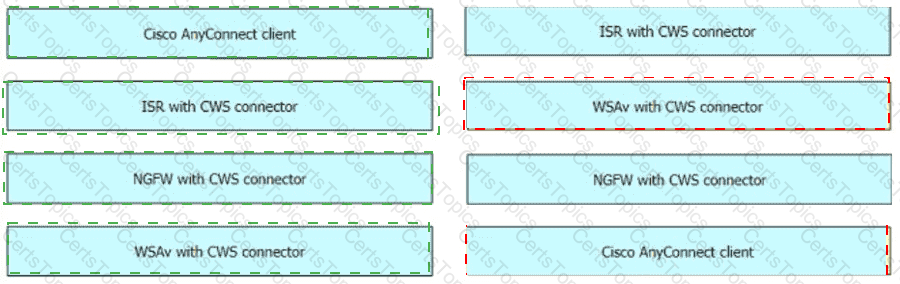
Drag and drop the Cisco CWS redirection options from the left onto the capabilities on the right.
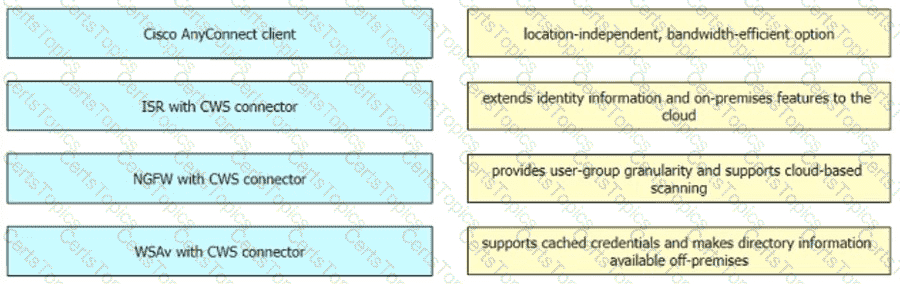
Options:

Question 188

What is a characteristic of Firepower NGIPS inline deployment mode?

Options:

A.

ASA with Firepower module cannot be deployed.

B.

It cannot take actions such as blocking traffic.

C.

It is out-of-band from traffic.

D.

It must have inline interface pairs configured.

Question 189

Which RADIUS attribute can you use to filter MAB requests in an 802.1 x deployment?

Options:

A.

1

B.

2

C.

6

D.

31

Question 190

A network engineer must create an access control list on a Cisco Adaptive Security Appliance firewall. The access control list must permit HTTP traffic to the internet from the organization ' s inside network 192.168.1.0/24. Which IOS command must oe used to create the access control list?

Options:

A.
B.
C.
D.
Question 191

An organization wants to provide visibility and to identify active threats in its network using a VM. The

organization wants to extract metadata from network packet flow while ensuring that payloads are not retained

or transferred outside the network. Which solution meets these requirements?

Options:

A.

Cisco Umbrella Cloud

B.

Cisco Stealthwatch Cloud PNM

C.

Cisco Stealthwatch Cloud PCM

D.

Cisco Umbrella On-Premises

Question 192

Drag and drop the VPN functions from the left onto the descriptions on the right.
Options:

Question 193

Which two global commands must the network administrator implement to limit the attack surface of an internet-facing Cisco router? (Choose two.)

Options:

A.

no service password-recovery

B.

no cdp run

C.

service tcp-keepalives-in

D.

no ip http server

E.

ip ssh version 2

Question 194

Which two characteristics of messenger protocols make data exfiltration difficult to detect and prevent?

(Choose two)

Options:

A.

Outgoing traffic is allowed so users can communicate with outside organizations.

B.

Malware infects the messenger application on the user endpoint to send company data.

C.

Traffic is encrypted, which prevents visibility on firewalls and IPS systems.

D.

An exposed API for the messaging platform is used to send large amounts of data.

E.

Messenger applications cannot be segmented with standard network controls

Question 195

Which two parameters are used to prevent a data breach in the cloud? (Choose two.)

Options:

A.

DLP solutions

B.

strong user authentication

C.

encryption

D.

complex cloud-based web proxies

E.

antispoofing programs

Question 196

Which two criteria must a certificate meet before the WSA uses it to decrypt application traffic? (Choose two.)

Options:

A.

It must include the current date.

B.

It must reside in the trusted store of the WSA.

C.

It must reside in the trusted store of the endpoint.

D.

It must have been signed by an internal CA.

E.

it must contain a SAN.

Question 197

A healthcare organization is deploying Cisco Secure Access to prevent protected health information from being shared with generative AI services. The security team requires real-time DLP inspection only for traffic destined for AI applications, with minimal false positives during general web browsing. The policy must permit tuning based on the proximity and match counts of PHI identifiers. Which configuration action must the engineer perform?

Options:

A.

Configure a real-time DLP rule referencing a built-in PHI data classification with default thresholds, scoped to a web profile that includes all Internet traffic.

B.

Implement an API-based DLP rule referencing a custom PHI data classification with tuned proximity and match-count thresholds, scoped to the generative AI application category.

C.

Deploy a real-time DLP rule referencing a built-in PHI data classification with tuned match-count thresholds, scoped to a web profile filtered by destination lists for known AI vendors.

D.

Apply a real-time DLP rule referencing a custom PHI data classification with tuned proximity and match-count thresholds, scoped to a web profile filtered by the generative AI application category.

Question 198

Which technology must De used to Implement secure VPN connectivity among company branches over a private IP cloud with any-to-any scalable connectivity?

Options:

A.

GET VPN

B.

IPsec DVTI

C.

DMVPN

D.

FlexVPN

Question 199

How does DNS Tunneling exfiltrate data?

Options:

A.

An attacker registers a domain that a client connects to based on DNS records and sends malware throughthat connection.

B.

An attacker opens a reverse DNS shell to get into the client’s system and install malware on it.

C.

An attacker uses a non-standard DNS port to gain access to the organization’s DNS servers in order topoison the resolutions.

D.

An attacker sends an email to the target with hidden DNS resolvers in it to redirect them to a maliciousdomain.

Question 200

Which open standard underpins OpenID Connect, enabling Cisco Duo to authorize application access?

Options:

A.

OAuth 2.0

B.

SCEP

C.

RSTP

D.

Kerberos

Question 201

What must be configured in Cisco ISE to enforce reauthentication of an endpoint session when an endpoint is

deleted from an identity group?

Options:

A.

posture assessment

B.

CoA

C.

external identity source

D.

SNMP probe

Question 202

Drag and drop the VPN functions from the left onto the description on the right.
Options:

Question 203

Which Cisco firewall solution supports configuration via Cisco Policy Language?

Options:

A.

CBAC

B.

ZFW

C.

IPS

D.

NGFW

Question 204

Which portion of the network do EPP solutions solely focus on and EDR solutions do not?

Options:

A.

server farm

B.

perimeter

C.

core

D.

East-West gateways

Question 205

Which open source tool does Cisco use to create graphical visualizations of network telemetry on Cisco IOS XE devices?

Options:

A.

InfluxDB

B.

Splunk

C.

SNMP

D.

Grafana

Question 206

What is an advantage of using a next-generation firewall compared to a traditional firewall?

Options:

A.

Next-generation firewalls have stateless inspection capabilities, and traditional firewalls use stateful inspection.

B.

Next-generation firewalls use dynamic packet filtering, and traditional firewalls use static packet filtering.

C.

Next-generation firewalls have threat intelligence feeds, and traditional firewalls use signature detection.

D.

Next-generation firewalls use intrusion prevention policies, and traditional firewalls use intrusion detection policies.

Question 207

Refer to the exhibit.

The DHCP snooping database resides on router R1, and dynamic ARP inspection is configured only on switch SW2. Which ports must be configured as untrusted so that dynamic ARP inspection operates normally?

Options:

A.

P2 and P3 only

B.

P5, P6, and P7 only

C.

P1, P2, P3, and P4 only

D.

P2, P3, and P6 only

Question 208

Which system performs compliance checks and remote wiping?

Options:

A.

MDM

B.

ISE

C.

AMP

D.

OTP

Question 209

An engineer is configuring guest WLAN access using Cisco ISE and the Cisco WLC. Which action temporarily gives guest endpoints access dynamically while maintaining visibility into who or what is connecting?

Options:

A.

Modify the WLC configuration to require local WLC logins for the authentication prompts.

B.

Configure ISE and the WLC for guest redirection and services using a self-registered portal.

C.

Configure ISE and the WLC for guest redirection and services using a hotspot portal.

D.

Modify the WLC configuration to allow any endpoint to access an internet-only VLAN.

Question 210

Refer to the exhibit.

A site-to-site IKEv2 VPN between a Cisco Secure Firewall Threat Defense device with public IP address 203.0.113.10 and a third-party firewall with public IP address 198.51.100.20 is failing to establish at a logistics company. The engineer enables IKEv2 debugging on the FTD and captures the output. Which action must be performed to resolve the issue?

Options:

A.

Change the DH group in the IKEv2 policy from Group 20 to Group 14 to match the group negotiated during IKE_SA_INIT.

B.

Verify that the pre-shared key configured on the VPN peer object exactly matches the key on the remote peer, including case, special characters, and any leading or trailing spaces.

C.

Update the IKEv2 policy to remove SHA-384 and use only SHA-256, aligning Phase 1 integrity with the algorithm agreed upon during IKE_SA_INIT.

D.

Switch both peers to certificate-based authentication by enrolling an identity certificate from the corporate CA and sharing the CA certificate with the remote peer.

Question 211

Which Cisco Advanced Malware protection for Endpoints deployment architecture is designed to keep data

within a network perimeter?

Options:

A.

cloud web services

B.

network AMP

C.

private cloud

D.

public cloud

Question 212

What provides visibility and awareness into what is currently occurring on the network?

Options:

A.

CMX

B.

WMI

C.

Prime Infrastructure

D.

Telemetry

Question 213

Refer to the exhibit.

A network administrator configured a site-to-site VPN tunnel between two Cisco IOS routers, and hosts are unable to communicate between two sites of VPN. The network administrator runs the debug crypto isakmp sa command to track VPN status. What is the problem according to this command output?

Options:

A.

hashing algorithm mismatch

B.

encryption algorithm mismatch

C.

authentication key mismatch

D.

interesting traffic was not applied

Question 214

An engineer must configure Cisco AMP for Endpoints so that it contains a list of files that should not be executed by users. These files must not be quarantined. Which action meets this configuration requirement?

Options:

A.

Identity the network IPs and place them in a blocked list.

B.

Modify the advanced custom detection list to include these files.

C.

Create an application control blocked applications list.

D.

Add a list for simple custom detection.

Question 215

Which factor must be considered when choosing the on-premise solution over the cloud-based one?

Options:

A.

With an on-premise solution, the provider is responsible for the installation and maintenance of the product, whereas with a cloud-based solution, the customer is responsible for it

B.

With a cloud-based solution, the provider is responsible for the installation, but the customer is responsible for the maintenance of the product.

C.

With an on-premise solution, the provider is responsible for the installation, but the customer is responsible for the maintenance of the product.

D.

With an on-premise solution, the customer is responsible for the installation and maintenance of theproduct, whereas with a cloud-based solution, the provider is responsible for it.

Question 216

Which benefit is provided by ensuring that an endpoint is compliant with a posture policy configured in Cisco ISE?

Options:

A.

It allows the endpoint to authenticate with 802.1x or MAB.

B.

It verifies that the endpoint has the latest Microsoft security patches installed.

C.

It adds endpoints to identity groups dynamically.

D.

It allows CoA to be applied if the endpoint status is compliant.

Question 217

Which attribute has the ability to change during the RADIUS CoA?

Options:

A.

NTP

B.

Authorization

C.

Accessibility

D.

Membership

Question 218

An engineer is configuring 802.1X authentication on Cisco switches in the network and is using CoA as a mechanism. Which port on the firewall must be opened to allow the CoA traffic to traverse the network?

Options:

A.

TCP 6514

B.

UDP 1700

C.

TCP 49

D.

UDP 1812

Question 219

What does Cisco ISE use to collect endpoint attributes that are used in profiling?

Options:

A.

probes

B.

posture assessment

C.

Cisco AnyConnect Secure Mobility Client

D.

Cisco pxGrid

Question 220

Which Splunk SOAR component automates multi-step security actions into a repeatable workflow?

Options:

A.

Alert

B.

Action

C.

Data model

D.

Playbook

Question 221

Which two endpoint measures are used to minimize the chances of falling victim to phishing and social

engineering attacks? (Choose two)

Options:

A.

Patch for cross-site scripting.

B.

Perform backups to the private cloud.

C.

Protect against input validation and character escapes in the endpoint.

D.

Install a spam and virus email filter.

E.

Protect systems with an up-to-date antimalware program

Question 222

Which key feature of Cisco ZFW is unique among other Cisco IOS firewall solutions?

Options:

A.

Security levels

B.

Stateless inspection

C.

Security zones

D.

SSL inspection

Question 223

Which two capabilities of Integration APIs are utilized with Cisco DNA center? (Choose two)

Options:

A.

Upgrade software on switches and routers

B.

Third party reporting

C.

Connect to ITSM platforms

D.

Create new SSIDs on a wireless LAN controller

E.

Automatically deploy new virtual routers

Question 224

For which type of attack is multifactor authentication an effective deterrent?

Options:

A.

Ping of death

B.

Teardrop

C.

SYN flood

D.

Phishing

Question 225

Which Cisco Secure Client module is integrated with Splunk Enterprise to provide monitoring capabilities to administrators to allow them to view endpoint application usage?

Options:

A.

Umbrella Roaming Security

B.

Network Visibility

C.

AMP Enabler

D.

ISE Posture

Question 226

Which category includes DoS Attacks?

Options:

A.

Virus attacks

B.

Trojan attacks

C.

Flood attacks

D.

Phishing attacks

Question 227

An engineer configured a new network identity in Cisco Umbrella but must verify that traffic is being routed

through the Cisco Umbrella network. Which action tests the routing?

Options:

A.

Ensure that the client computers are pointing to the on-premises DNS servers.

B.

Enable the Intelligent Proxy to validate that traffic is being routed correctly.

C.

Add the public IP address that the client computers are behind to a Core Identity.

D.

Browse to http://welcome.umbrella.com/ to validate that the new identity is working.

Question 228

Drag and drop the capabilities of Cisco Firepower versus Cisco AMP from the left into the appropriate category on the right.
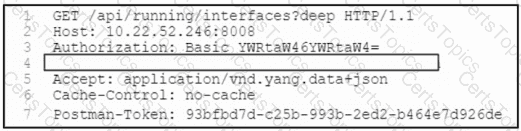
Options:

Question 229

Refer to the exhibit. A network engineer must retrieve the interface configuration on a Cisco router by using the NETCONF API. The engineer uses a python script to automate the activity.

Which code snippet completes the script?

Options:

A.

Content-Type: application/vnd.yang.data+json

B.

Content-Type: application/vnd.yang.data

C.

Content-Type: application/vnd.yang.data+api

D.

Content-Type: applications/json/vnd.yang.data

Question 230

An engineer is configuring AMP for endpoints and wants to block certain files from executing. Which outbreak

control method is used to accomplish this task?

Options:

A.

device flow correlation

B.

simple detections

C.

application blocking list

D.

advanced custom detections

Question 231

Which type of attack is MFA an effective deterrent for?

Options:

A.

ping of death

B.

phishing

C.

teardrop

D.

syn flood

Question 232

An engineer must configure AsyncOS for Cisco Secure Web Appliance to push log files to a syslog server using the SCP retrieval method. Drag and drop the steps from the left into the sequence on the right to complete the configuration.
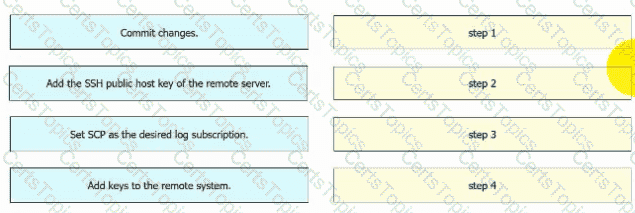
Options:

Question 233

Which two tasks allow NetFlow on a Cisco ASA 5500 Series firewall? (Choose two)

Options:

A.

Enable NetFlow Version 9.

B.

Create an ACL to allow UDP traffic on port 9996.

C.

Apply NetFlow Exporter to the outside interface in the inbound direction.

D.

Create a class map to match interesting traffic.

E.

Define a NetFlow collector by using the flow-export command

Question 234

Which two aspects of the cloud PaaS model are managed by the customer but not the provider? (Choose two)

Options:

A.

virtualization

B.

middleware

C.

operating systems

D.

applications

E.

data

Question 235

A company wants to enforce security policy using Cisco Secure Access Secure Internet Access. The design requirements are:

    Block adult-content and gambling categories for all users.

    Inspect file downloads for malware.

    Bypass TLS decryption for financial and healthcare domains because of compliance requirements.

    Allow the Marketing department to use social media while keeping file scanning active for downloads from those sites.

Which two configuration actions must the engineer perform in Cisco Secure Access to meet the requirements? (Choose two.)

Options:

A.

Configure a Marketing policy with higher precedence to allow social-networking sites, and apply a decryption-bypass list for financial and healthcare domains.

B.

Disable TLS decryption globally and rely on DNS-layer reputation to block adult-content and gambling sites.

C.

Use destination allow lists for financial and healthcare sites to prevent SSL inspection, with malware scanning enabled in full-inspection mode for all traffic.

D.

Create a global policy that blocks adult-content and gambling categories with TLS inspection enabled, and create a higher-precedence Marketing policy that allows social-networking sites.

E.

Implement one global policy that blocks adult-content and gambling categories, and add a web-application allow rule for social networking.

Question 236

Which action configures the IEEE 802.1X Flexible Authentication feature lo support Layer 3 authentication mechanisms?

Options:

A.

Identity the devices using this feature and create a policy that allows them to pass Layer 2 authentication.

B.

Configure WebAuth so the hosts are redirected to a web page for authentication.

C.

Modify the Dot1x configuration on the VPN server lo send Layer 3 authentications to an external authentication database

D.

Add MAB into the switch to allow redirection to a Layer 3 device for authentication.

Question 237

What are two reasons for implementing a multifactor authentication solution such as Duo Security provide to an

organization? (Choose two)

Options:

A.

flexibility of different methods of 2FA such as phone callbacks, SMS passcodes, and push notifications

B.

single sign-on access to on-premises and cloud applications

C.

integration with 802.1x security using native Microsoft Windows supplicant

D.

secure access to on-premises and cloud applications

E.

identification and correction of application vulnerabilities before allowing access to resources

Question 238

Drag and drop the suspicious patterns for the Cisco Tetration platform from the left onto the correct definitions on the right.
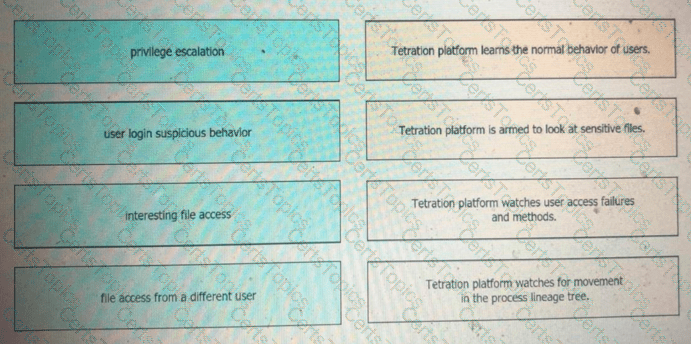
Options:

Question 239

Which action configures the IEEE 802.1X Flexible Authentication feature to support Layer 3 authentication mechanisms?

Options:

A.

Add MAB into the switch to allow redirection to a Layer 3 device for authentication.

B.

Identify the devices using this feature and create a policy that allows them to pass Layer 2 authentication.

C.

Modify the Dot1x configuration on the VPN server to send Layer 3 authentications to an external authentication database.

D.

Configure WebAuth so the hosts are redirected to a web page for authentication.

Question 240

What is a feature of container orchestration?

Options:

A.

ability to deploy Amazon ECS clusters by using the Cisco Container Platform data plane

B.

ability to deploy Amazon EKS clusters by using the Cisco Container Platform data plane

C.

ability to deploy Kubernetes clusters in air-gapped sites

D.

automated daily updates

Exam Detail
Vendor: Cisco
Certification: CCNP Security
Exam Code: 350-701
Last Update: Oct 5, 2026
350-701 Question Answers
Page: 1 / 60
Total 801 questions