Cisco Umbrella is a cloud-delivered and SaaS-based solution that provides DNS-layer security and web filtering for internet traffic. It blocks requests to malicious domains or IPs before a connection is even established, and logs and inspects all web traffic for greater transparency, control, and protection1.
However, not all domains or IPs are clearly malicious or benign. Some of them may be risky, meaning that they host both legitimate and malicious content, or that they have a low reputation score based on various factors. For these domains or IPs, Cisco Umbrella offers the option to proxy the traffic through the intelligent proxy, which is a selective web proxy that performs deeper inspection and analysis of the web content2.
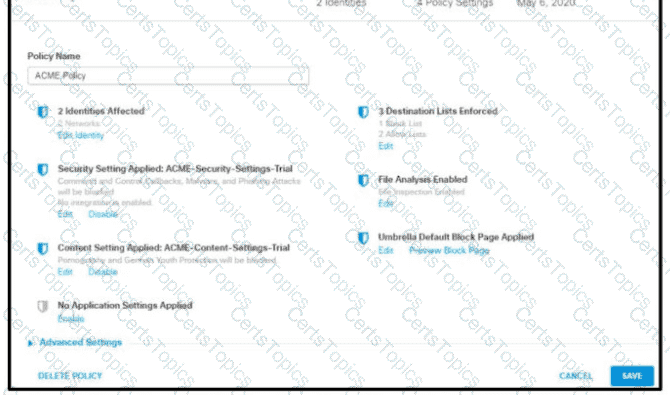
The intelligent proxy can apply URL filtering, file inspection, and file type control to the proxied traffic, and block or allow it based on the policy settings. The intelligent proxy can also leverage Cisco Advanced Malware Protection (AMP) and antivirus engines to scan files for malware and threats3.
Therefore, by using the intelligent proxy, Cisco Umbrella can manage traffic that is directed toward risky domains more effectively, and provide an additional layer of security and visibility for the organization.
References :=
Manage the Intelligent Proxy
Manage File Inspection
Cisco Umbrella At a Glance