
Power Up Your Study Prep: Black Friday 75% Discount! Use coupon code below to save! - Ends in 0d 00h 00m 00s - Coupon code: big75certs

ECCouncil EC0-350 Exam With Confidence Using Practice Dumps

Exam Code:
EC0-350
Exam Name:
Ethical Hacking and Countermeasures V8
Certification:
Vendor:
Questions:
878
Last Updated:
Nov 13, 2026
Exam Status:
Stable
ECCouncil EC0-350

EC0-350: Certified Ethical Hacker Exam 2025 Study Guide Pdf and Test Engine

Are you worried about passing the ECCouncil EC0-350 (Ethical Hacking and Countermeasures V8) exam? Download the most recent ECCouncil EC0-350 braindumps with answers that are 100% real. After downloading the ECCouncil EC0-350 exam dumps training , you can receive 99 days of free updates, making this website one of the best options to save additional money. In order to help you prepare for the ECCouncil EC0-350 exam questions and verified answers by IT certified experts, CertsTopics has put together a complete collection of dumps questions and answers. To help you prepare and pass the ECCouncil EC0-350 exam on your first attempt, we have compiled actual exam questions and their answers. 

Our (Ethical Hacking and Countermeasures V8) Study Materials are designed to meet the needs of thousands of candidates globally. A free sample of the CompTIA EC0-350 test is available at CertsTopics. Before purchasing it, you can also see the ECCouncil EC0-350 practice exam demo.

Ethical Hacking and Countermeasures V8 Questions and Answers

Question 1

Firewalk has just completed the second phase (the scanning phase) and a technician receives the output shown below. What conclusions can be drawn based on these scan results? TCP port 21 – no response  TCP port 22 – no response TCP port 23 – Time-to-live exceeded

Options:

A.

The firewall itself is blocking ports 21 through 23 and a service is listening on port 23 of the target host.

B.

The lack of response from ports 21 and 22 indicate that those services are not running on the destination server.

C.

The scan on port 23 passed through the filtering device. This indicates that port 23 was not blocked at the firewall.

D.

The scan on port 23 was able to make a connection to the destination host prompting the firewall to respond with a TTL error.

Buy Now
Question 2

On a Linux device, which of the following commands will start the Nessus client in the background so that the Nessus server can be configured?

Options:

A.

nessus +

B.

nessus *s

C.

nessus &

D.

nessus -d

Question 3

Switches maintain a CAM Table that maps individual MAC addresses on the network to physical ports on the switch.

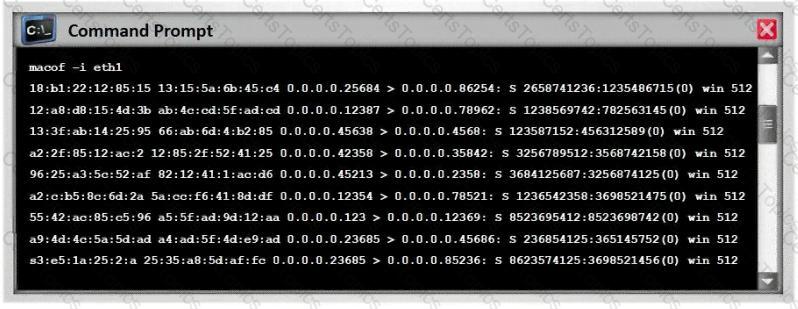
In MAC flooding attack, a switch is fed with many Ethernet frames, each containing different source MAC addresses, by the attacker. Switches have a limited memory for mapping various MAC addresses to physical ports. What happens when the CAM table becomes full?

Options:

A.

Switch then acts as hub by broadcasting packets to all machines on the network

B.

The CAM overflow table will cause the switch to crash causing Denial of Service

C.

The switch replaces outgoing frame switch factory default MAC address of FF:FF:FF:FF:FF:FF

D.

Every packet is dropped and the switch sends out SNMP alerts to the IDS port