Weekend Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: big75certs

Fortinet NSE8_812 Exam With Confidence Using Practice Dumps

Exam Code:
NSE8_812
Exam Name:
Network Security Expert 8 Written Exam
Vendor:
Questions:
105
Last Updated:
Sep 19, 2026
Exam Status:
Stable
Fortinet NSE8_812

NSE8_812: Fortinet Network Security Expert Exam 2025 Study Guide Pdf and Test Engine

Are you worried about passing the Fortinet NSE8_812 (Network Security Expert 8 Written Exam) exam? Download the most recent Fortinet NSE8_812 braindumps with answers that are 100% real. After downloading the Fortinet NSE8_812 exam dumps training , you can receive 99 days of free updates, making this website one of the best options to save additional money. In order to help you prepare for the Fortinet NSE8_812 exam questions and verified answers by IT certified experts, CertsTopics has put together a complete collection of dumps questions and answers. To help you prepare and pass the Fortinet NSE8_812 exam on your first attempt, we have compiled actual exam questions and their answers. 

Our (Network Security Expert 8 Written Exam) Study Materials are designed to meet the needs of thousands of candidates globally. A free sample of the CompTIA NSE8_812 test is available at CertsTopics. Before purchasing it, you can also see the Fortinet NSE8_812 practice exam demo.
Network Security Expert 8 Written Exam Questions and Answers

Question 1

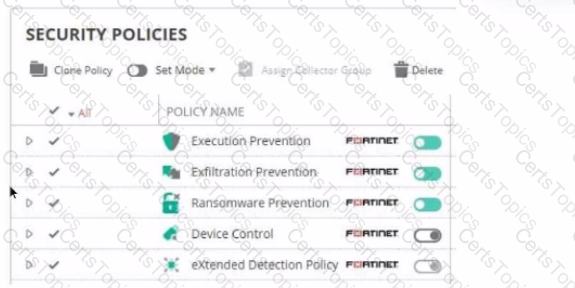
Refer to The exhibit showing a FortiEDR configuration.

Based on the exhibit, which statement is correct?

Options:

A.

The presence of a cryptolocker malware at rest on the filesystem will be detected by the Ransomware Prevention security policy.

B.

FortiEDR Collector will not collect OS Metadata.

C.

If a malicious file is executed and attempts to establish a connection it will generate duplicate events.

D.

If an unresolved file rule is triggered, by default the file is logged but not blocked.

Buy Now
Question 2

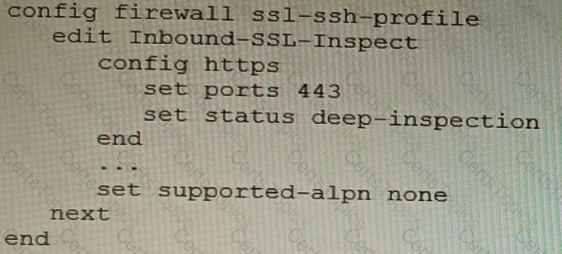
Refer to the CLI configuration of an SSL inspection profile from a FortiGate device configured to protect a web server:

Based on the information shown, what is the expected behavior when an HTTP/2 request comes in?

Options:

A.

FortiGate will reject all HTTP/2 ALPN headers.

B.

FortiGate will strip the ALPN header and forward the traffic.

C.

FortiGate will rewrite the ALPN header to request HTTP/1.

D.

FortiGate will forward the traffic without modifying the ALPN header.

Question 3

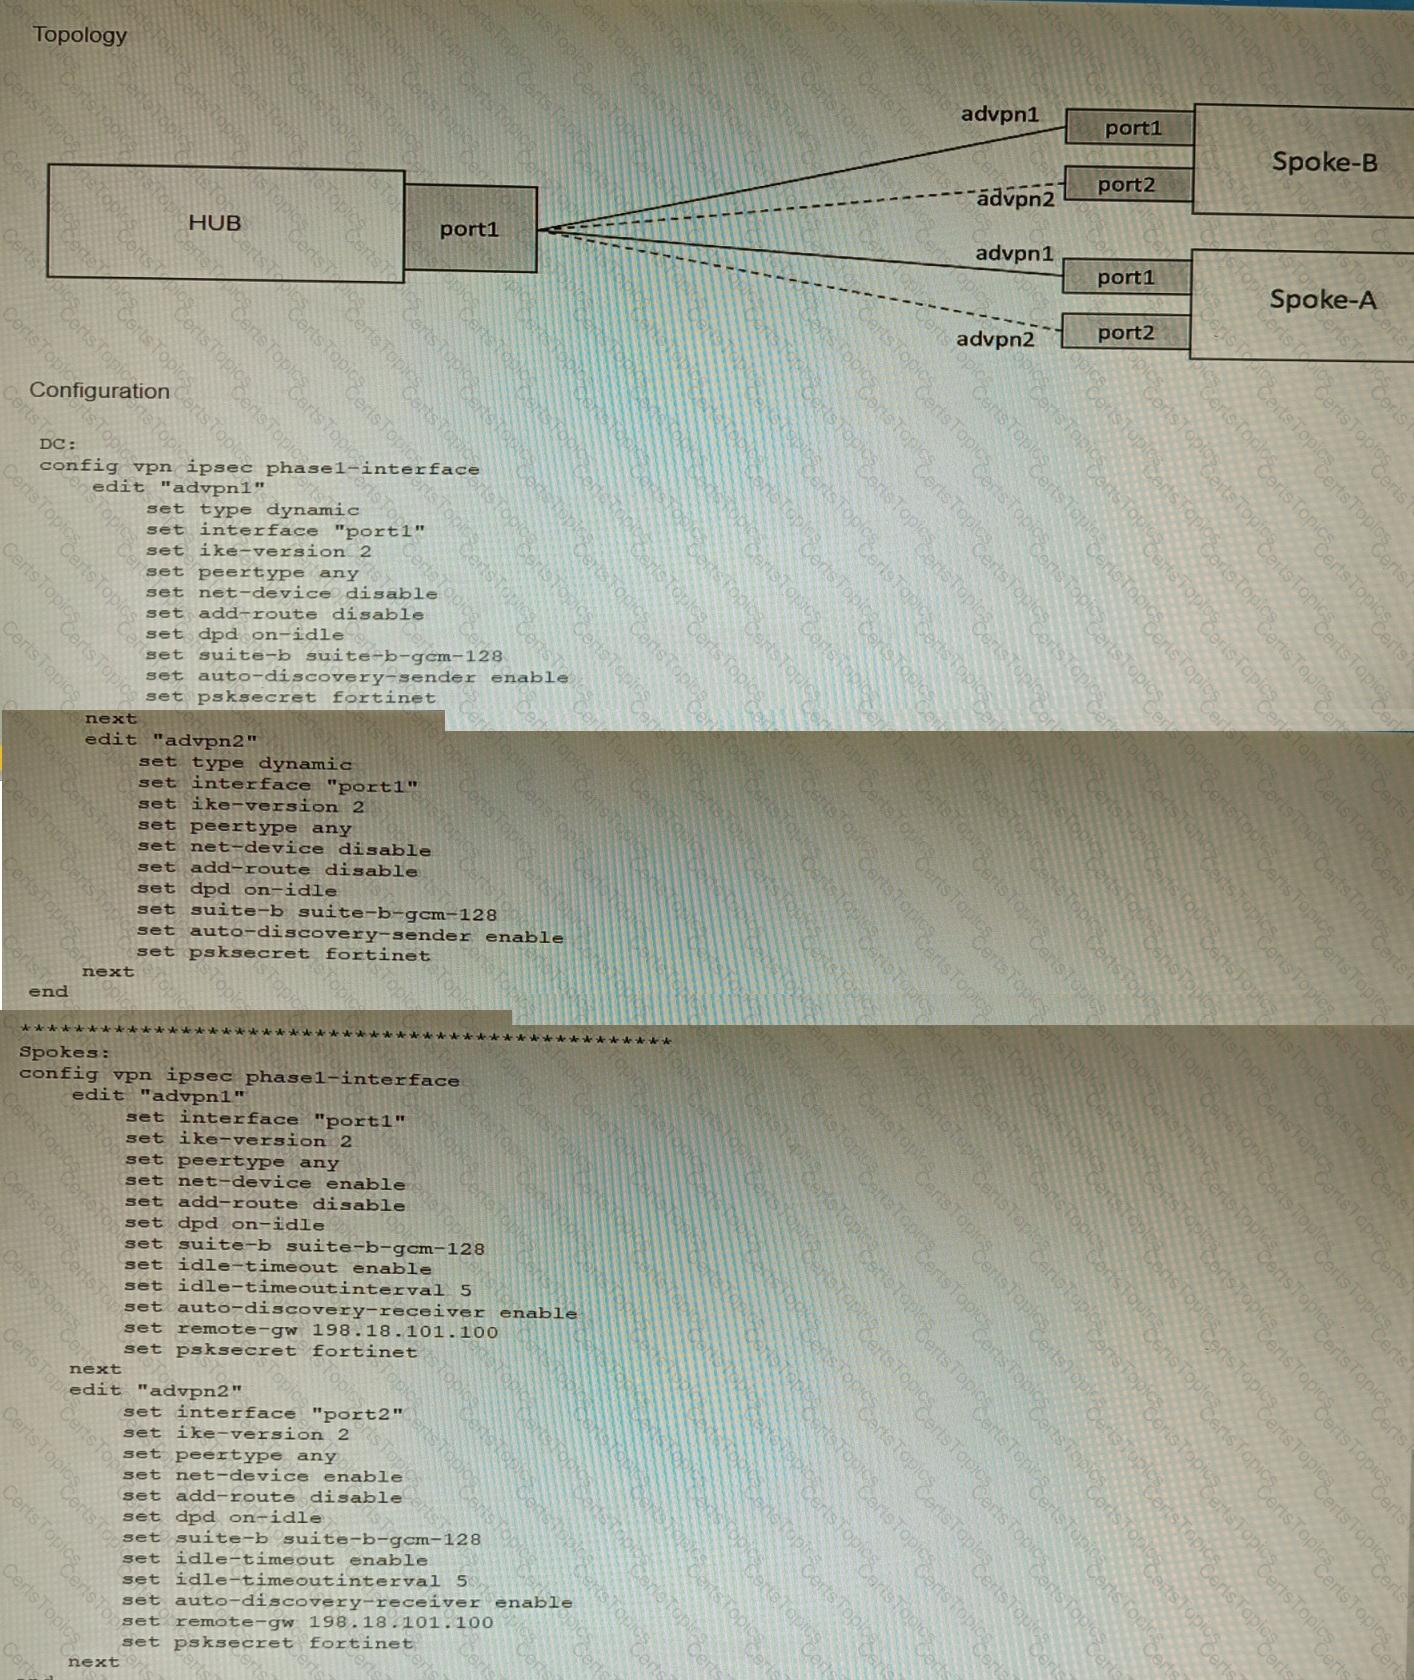
Refer to the exhibits.

The exhibits show a diagram of a requested topology and the base IPsec configuration.

A customer asks you to configure ADVPN via two internet underlays. The requirement is that you use one interface with a single IP address on DC FortiGate.

In this scenario, which feature should be implemented to achieve this requirement?

Options:

A.

Use network-overlay id

B.

Change advpn2 to IKEv1

C.

Use local-id

D.

Use peer-id