
Refer to the exhibit.
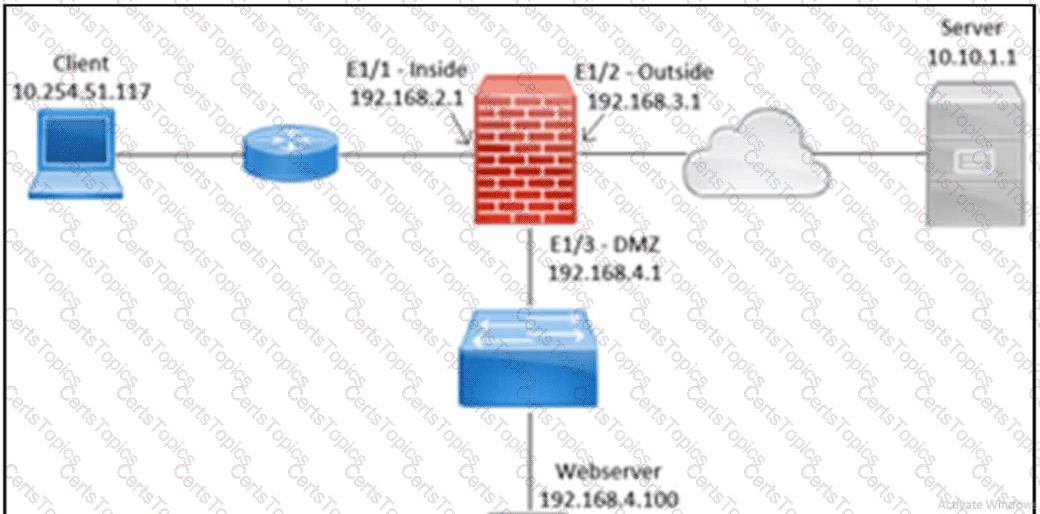
A client with IP address 10.254.51.117 connects through a Cisco Secure Firewall Threat Defense device toward a website at 10.10.1.1. The packet capture shows repeated TCP SYN packets from the client without completion of the three-way handshake. Which action must the engineer take to resolve the issue?
Which two actions can be used in an access control policy rule? (Choose two.)
A security engineer must configure a Cisco Secure Firewall Threat Defense device to inspect only executable files. A lightweight method of detecting whether a file is an executable must be used. Which configuration for Malware Cloud Lookup must be selected in Cisco Secure Firewall Management Center?
Which command is run at the CLI when logged in to an FTD unit, to determine whether the unit is managed locally or by a remote FMC server?
Copyright © 2021-2026 CertsTopics. All Rights Reserved
