
Pre-Winter Sale 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: save70

CCNP Security 300-710 Exam Dumps

Page: 16 / 33
Total 444 questions

Securing Networks with Cisco Firepower (300-710 SNCF) v1.2 Questions and Answers

Question 61

An organization has a Cisco FTD that uses bridge groups to pass traffic from the inside interfaces to the outside interfaces. They are unable to gather information about neighbouring Cisco devices or use multicast in their environment. What must be done to resolve this issue?

Options:

A.

Create a firewall rule to allow CDP traffic.

B.

Create a bridge group with the firewall interfaces.

C.

Change the firewall mode to transparent.

D.

Change the firewall mode to routed.

Question 62

An engineer wants to perform a packet capture on the Cisco FTD to confirm that the host using IP address 192 168.100.100 has the MAC address of 0042 7734.103 to help troubleshoot aconnectivity issue What is the correct tcpdump command syntax to ensure that the MAC address appears in the packet capture output?
Options:

A.

-nm src 192.168.100.100

B.

-ne src 192.168.100.100

C.

-w capture.pcap -s 1518 host 192.168.100.100 mac

D.

-w capture.pcap -s 1518 host 192.168.100.100 ether

Question 63

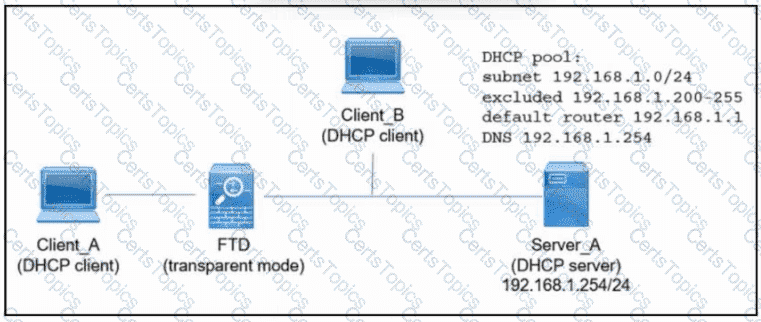
Refer to the exhibit. An engineer is deploying a new instance of Cisco Secure Firewall Threat Defense. Which action must the engineer take next so that Client_A and Client_B receive an IP address via DHCP from Server_A?

Options:

A.

Disable Option 82 in the DHCP relay configuration properties using Secure Firewall Management Center.

B.

Add access rules that allow DHCP traffic by using Cisco Secure Firewall Management Center.

C.

Add another DHCP pool on Server_A with DHCP relay on Secure Firewall Threat Defense.

D.

Disable all the DHCP Snort rules by using Secure Firewall Device Manager.

Question 64

A connectivity issue is occurring between a client and a server which are communicating through a Cisco Firepower device While troubleshooting, a network administrator sees that traffic is reaching the server, but the client is not getting a response Which step must be taken to resolve this issue without initiating traffic from the client?

Options:

A.

Use packet-tracer to ensure that traffic is not being blocked by an access list.

B.

Use packet capture to ensure that traffic is not being blocked by an access list.

C.

Use packet capture to validate that the packet passes through the firewall and is NATed to the corrected IP address.

D.

Use packet-tracer to validate that the packet passes through the firewall and is NATed to the corrected IP address.

Page: 16 / 33
Total 444 questions
