
With Cisco FTD software, which interface mode must be configured to passively receive traffic that passes through the appliance?
Refer to the exhibit.
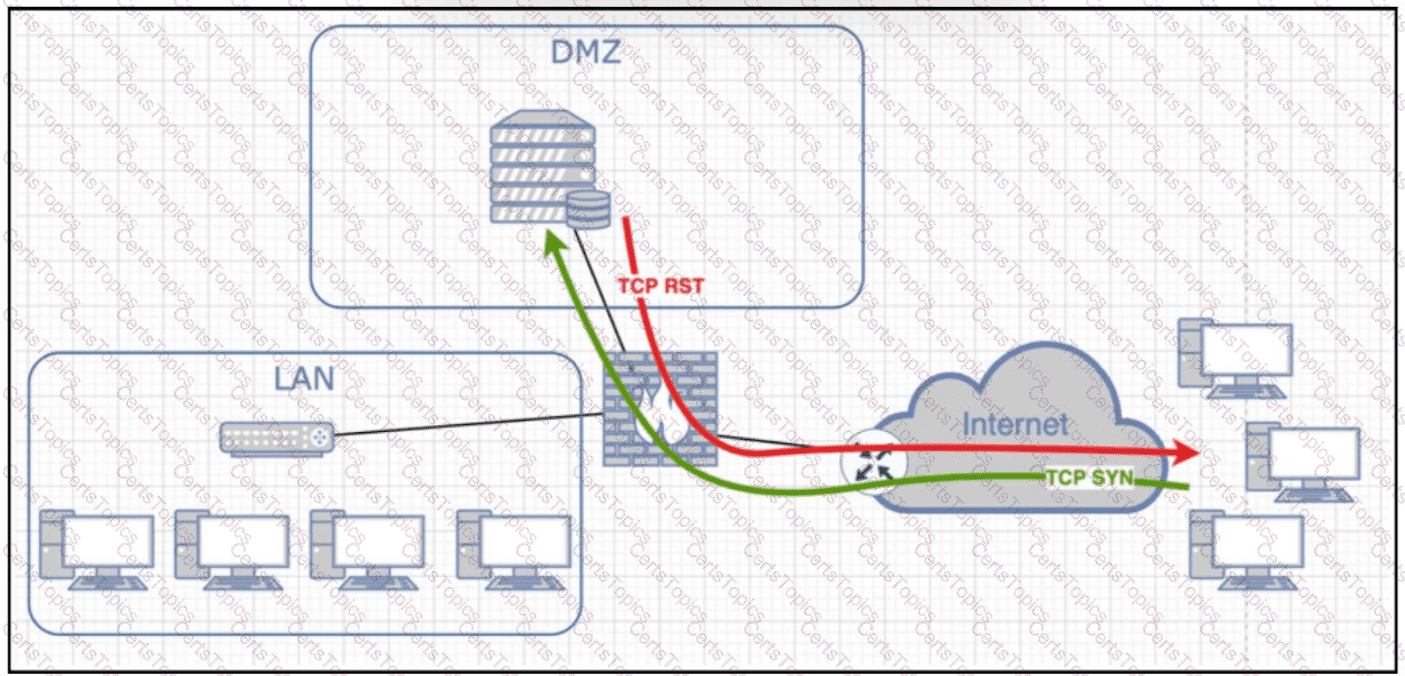
Following a critical incident, an engineer must determine why a server in the DMZ is sending TCP RST responses. Internet users can access the application but cannot view its main webpage. Where must the engineer capture the traffic to identify and resolve the issue?
Which two deployment types support high availability? (Choose two.)
A security engineer is configuring an Access Control Policy for multiple branch locations These locations share a common rule set and utilize a network object called INSIDE_NET which contains the locally significant internal network subnets at each location What technique will retain the policy consistency at each location but allow only the locally significant network subnet within the applicable rules?
Copyright © 2021-2026 CertsTopics. All Rights Reserved
