
An engineer must change the mode of a Cisco Secure Firewall Threat Defense (FTD) firewall in the Cisco Secure Firewall Management Center (FMC) inventory. The engineer must take these actions:
• Register Secure FTD with Secure FMC.
• Change the firewall mode.
• Deregister the Secure FTD device from Secure FMC.
How must the engineer take FTD take the actions?
An engineer is deploying a Cisco ASA Secure Firewall module. The engineer must be able to examine traffic without impacting the network, and the ASA has been deployed with a single context. Which ASA Secure Firewall module deployment mode must be implemented to meet the requirements?
An engineer must deploy a high-availability pair that includes two Cisco Secure Firewall Threat Defense devices. The deployment must provide a mechanism that protects synchronization traffic between the members. Which action must the engineer take?
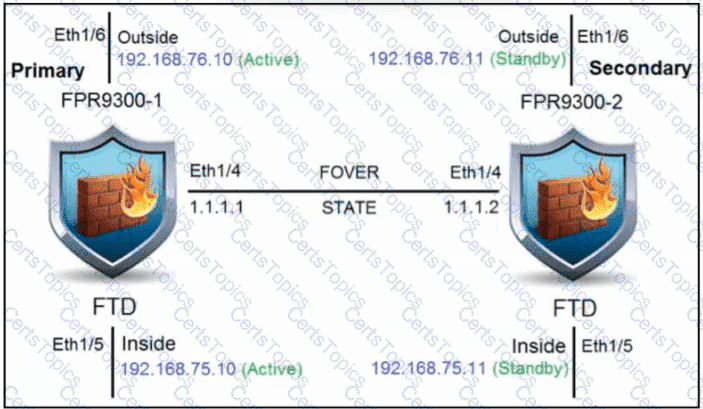
Refer to the exhibit. An engineer is configuring a high-availability solution that has the hardware devices and software versions:
two Cisco Secure Firewall 9300 Security Appliances with FXOS SW 2.0(1.23)
software Cisco Secure Firewall Threat Defense 6.0.1.1 (build 1023) on both appliances
one Cisco Secure Firewall Management Center with SW 6.0.1.1 (build 1023)
Which condition must be met to complete the high-availability configuration?
Copyright © 2021-2026 CertsTopics. All Rights Reserved
