
Halloween Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: big75certs

Fortinet NSE7_FSN_AR-7.6 Exam With Confidence Using Practice Dumps

Exam Code:
NSE7_FSN_AR-7.6
Exam Name:
Fortinet NSE 7 - Secure Networking 7.6 Architect
Vendor:
Questions:
177
Last Updated:
Oct 17, 2026
Exam Status:
Stable
Fortinet NSE7_FSN_AR-7.6

NSE7_FSN_AR-7.6: NSE 7 Network Security Architect Exam 2025 Study Guide Pdf and Test Engine

Are you worried about passing the Fortinet NSE7_FSN_AR-7.6 (Fortinet NSE 7 - Secure Networking 7.6 Architect) exam? Download the most recent Fortinet NSE7_FSN_AR-7.6 braindumps with answers that are 100% real. After downloading the Fortinet NSE7_FSN_AR-7.6 exam dumps training , you can receive 99 days of free updates, making this website one of the best options to save additional money. In order to help you prepare for the Fortinet NSE7_FSN_AR-7.6 exam questions and verified answers by IT certified experts, CertsTopics has put together a complete collection of dumps questions and answers. To help you prepare and pass the Fortinet NSE7_FSN_AR-7.6 exam on your first attempt, we have compiled actual exam questions and their answers. 

Our (Fortinet NSE 7 - Secure Networking 7.6 Architect) Study Materials are designed to meet the needs of thousands of candidates globally. A free sample of the CompTIA NSE7_FSN_AR-7.6 test is available at CertsTopics. Before purchasing it, you can also see the Fortinet NSE7_FSN_AR-7.6 practice exam demo.

Fortinet NSE 7 - Secure Networking 7.6 Architect Questions and Answers

Question 1

During the SAML negotiation process, in which section does the Identity Provider (IdP) provide the SAML attributes used in the authentication process to the Service Provider (SP)?

Options:

A.

Bindings HTTP post

B.

Assertion dump

C.

Authentication request

D.

Authentication response

Buy Now
Question 2

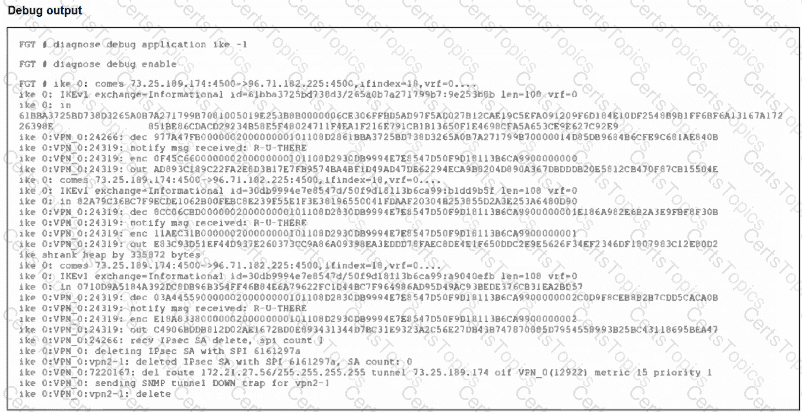
Refer to the exhibit.

An IPsec VPN tunnel is dropping, as shown by the debug output.

Analyzing the debug output, what could be causing the tunnel to go down?

Options:

A.

Phase 2 drops but Phase 1 is up.

B.

Dead Peer Detection is not receiving its acknowledge packet.

C.

The tunnel drops during rekey negotiation.

D.

The tunnel drops after the timer expires.

Question 3

Consider the scenario where the server name indication (SNI) does not match either the common name (CN) or any of the subject alternative names (SAN) in the server certificate. Which two actions will FortiGate take when using the default settings for SSL certificate inspection? (Choose two answers)

Options:

A.

FortiGate uses the SNI from the user ' s web browser.

B.

FortiGate does not decrypt the traffic if the traffic is blocked by the web filter profile.

C.

FortiGate uses the CN information from the Subject field in the server certificate.

D.

FortiGate does not decrypt the traffic if the traffic is allowed by the web filter profile.