
Halloween Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: big75certs

Fortinet NSE7_SOC_AR-7.6 Exam With Confidence Using Practice Dumps

Exam Code:
NSE7_SOC_AR-7.6
Exam Name:
Fortinet NSE 7 - Security Operations 7.6 Architect
Vendor:
Questions:
96
Last Updated:
Oct 27, 2026
Exam Status:
Stable
Fortinet NSE7_SOC_AR-7.6

NSE7_SOC_AR-7.6: Fortinet Certified Professional Security Operations Exam 2025 Study Guide Pdf and Test Engine

Are you worried about passing the Fortinet NSE7_SOC_AR-7.6 (Fortinet NSE 7 - Security Operations 7.6 Architect) exam? Download the most recent Fortinet NSE7_SOC_AR-7.6 braindumps with answers that are 100% real. After downloading the Fortinet NSE7_SOC_AR-7.6 exam dumps training , you can receive 99 days of free updates, making this website one of the best options to save additional money. In order to help you prepare for the Fortinet NSE7_SOC_AR-7.6 exam questions and verified answers by IT certified experts, CertsTopics has put together a complete collection of dumps questions and answers. To help you prepare and pass the Fortinet NSE7_SOC_AR-7.6 exam on your first attempt, we have compiled actual exam questions and their answers. 

Our (Fortinet NSE 7 - Security Operations 7.6 Architect) Study Materials are designed to meet the needs of thousands of candidates globally. A free sample of the CompTIA NSE7_SOC_AR-7.6 test is available at CertsTopics. Before purchasing it, you can also see the Fortinet NSE7_SOC_AR-7.6 practice exam demo.

Fortinet NSE 7 - Security Operations 7.6 Architect Questions and Answers

Question 1

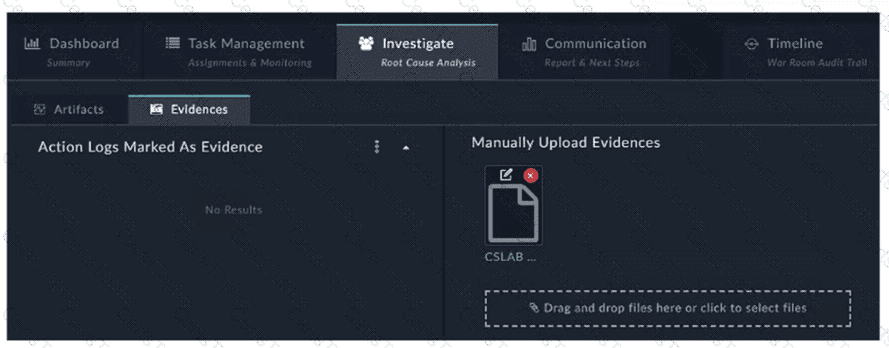
Refer to the exhibit.

How do you add a piece of evidence to the Action Logs Marked As Evidence area? (Choose one answer)

Options:

A.

By tagging output or a workspace comment with the keyword Evidence

B.

By linking an indicator to the war room

C.

By creating an evidence collection task and attaching a file

D.

By executing a playbook with the Save Execution Logs option enabled

Buy Now
Question 2

You suspect your organization has been a victim of numerous incidents carried out by the same threat actor. Which option allows you to group the incidents and track them? Choose one answer.

Options:

A.

Add a common tag to correlate them.

B.

Mark one incident as the parent and run a playbook to close the child incidents.

C.

Select those incidents and use the Merge function.

D.

Create a campaign and link related records to it.

Question 3

Refer to the exhibit.

Which two options describe how the Update Asset and Identity Database playbook is configured? (Choose two.)

Options:

A.

The playbook is using a local connector.

B.

The playbook is using a FortiMail connector.

C.

The playbook is using an on-demand trigger.

D.

The playbook is using a FortiClient EMS connector.