Halloween Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: big75certs

CompTIA PT0-003 Exam With Confidence Using Practice Dumps

Exam Code:
PT0-003
Exam Name:
CompTIA PenTest+ Exam
Certification:
Vendor:
Questions:
364
Last Updated:
Oct 26, 2026
Exam Status:
Stable
CompTIA PT0-003

PT0-003: PenTest+ Exam 2025 Study Guide Pdf and Test Engine

Are you worried about passing the CompTIA PT0-003 (CompTIA PenTest+ Exam) exam? Download the most recent CompTIA PT0-003 braindumps with answers that are 100% real. After downloading the CompTIA PT0-003 exam dumps training , you can receive 99 days of free updates, making this website one of the best options to save additional money. In order to help you prepare for the CompTIA PT0-003 exam questions and verified answers by IT certified experts, CertsTopics has put together a complete collection of dumps questions and answers. To help you prepare and pass the CompTIA PT0-003 exam on your first attempt, we have compiled actual exam questions and their answers. 

Our (CompTIA PenTest+ Exam) Study Materials are designed to meet the needs of thousands of candidates globally. A free sample of the CompTIA PT0-003 test is available at CertsTopics. Before purchasing it, you can also see the CompTIA PT0-003 practice exam demo.
CompTIA PenTest+ Exam Questions and Answers

Question 1

A penetration tester successfully gains access to a Linux system and then uses the following command:

find / -type f -ls > /tmp/recon.txt

Which of the following best describes the tester ' s goal?

Options:

A.

Permission enumeration

B.

Secrets enumeration

C.

User enumeration

D.

Service enumeration

Buy Now
Question 2

A penetration tester compromises a Windows OS endpoint that is joined to an Active Directory local environment. Which of the following tools should the tester use to manipulate authentication mechanisms to move laterally in the network?

Options:

A.

Rubeus

B.

WinPEAS

C.

NTLMRelayX

D.

Impacket

Question 3

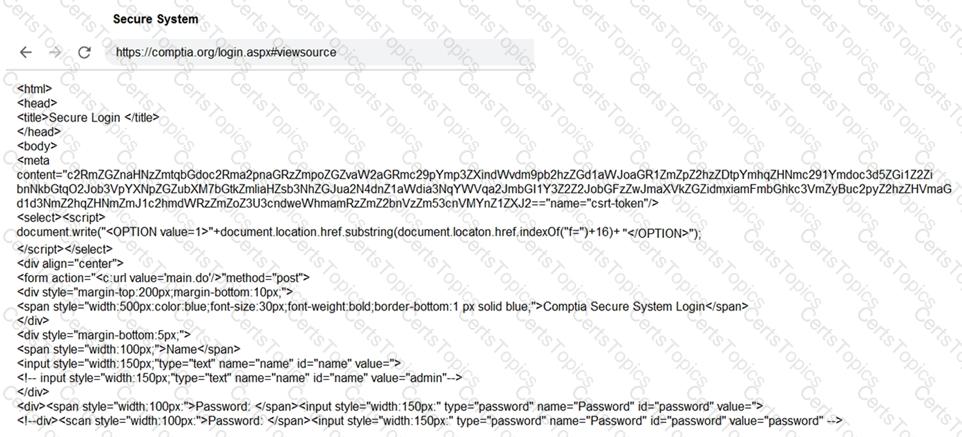
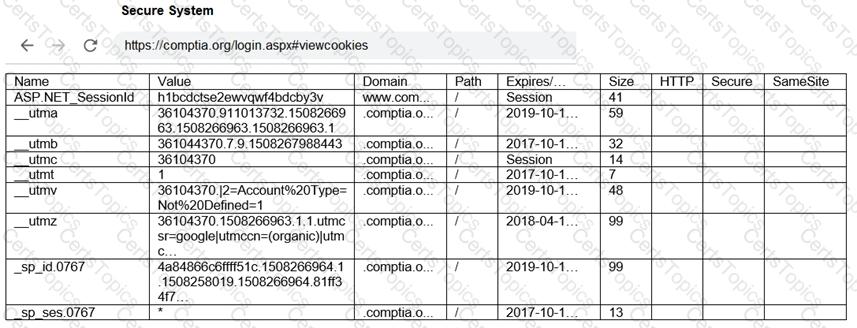
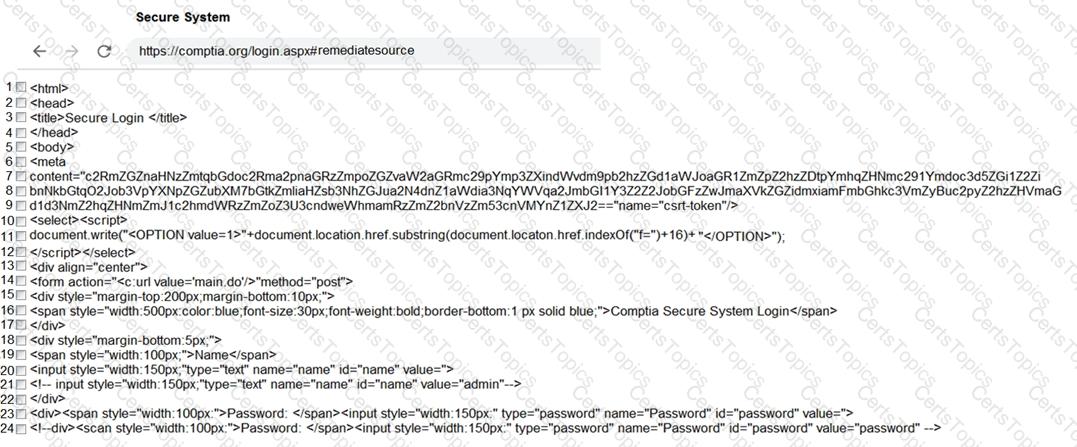
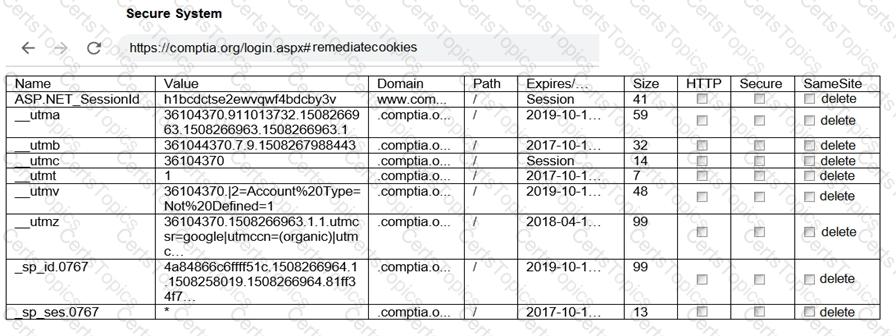
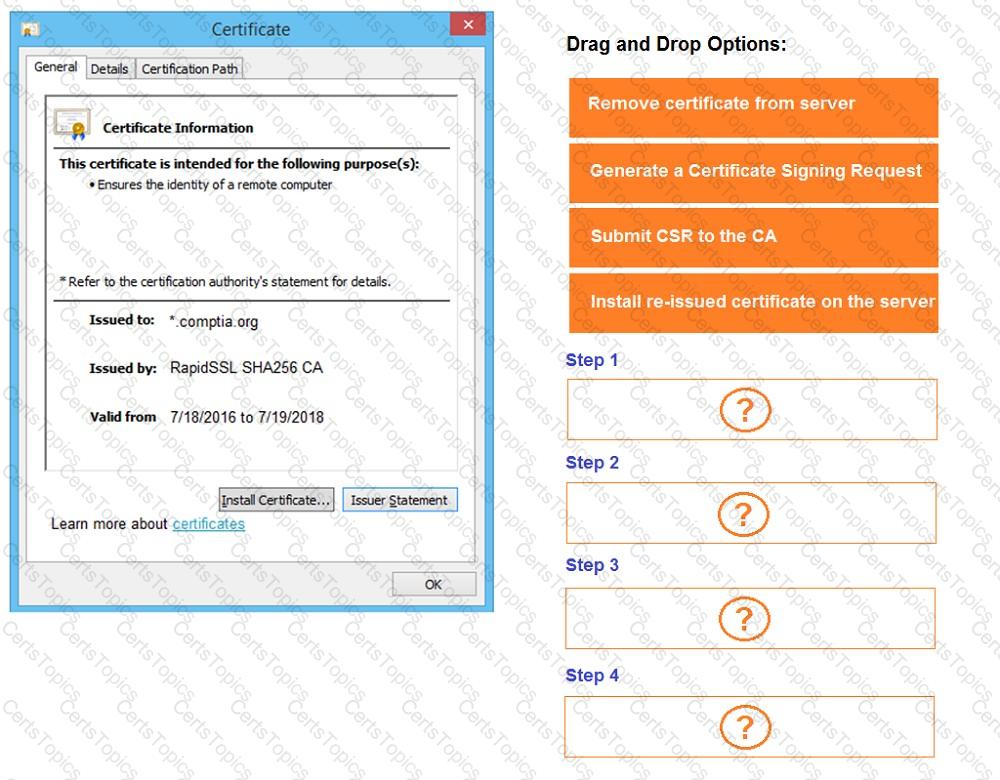
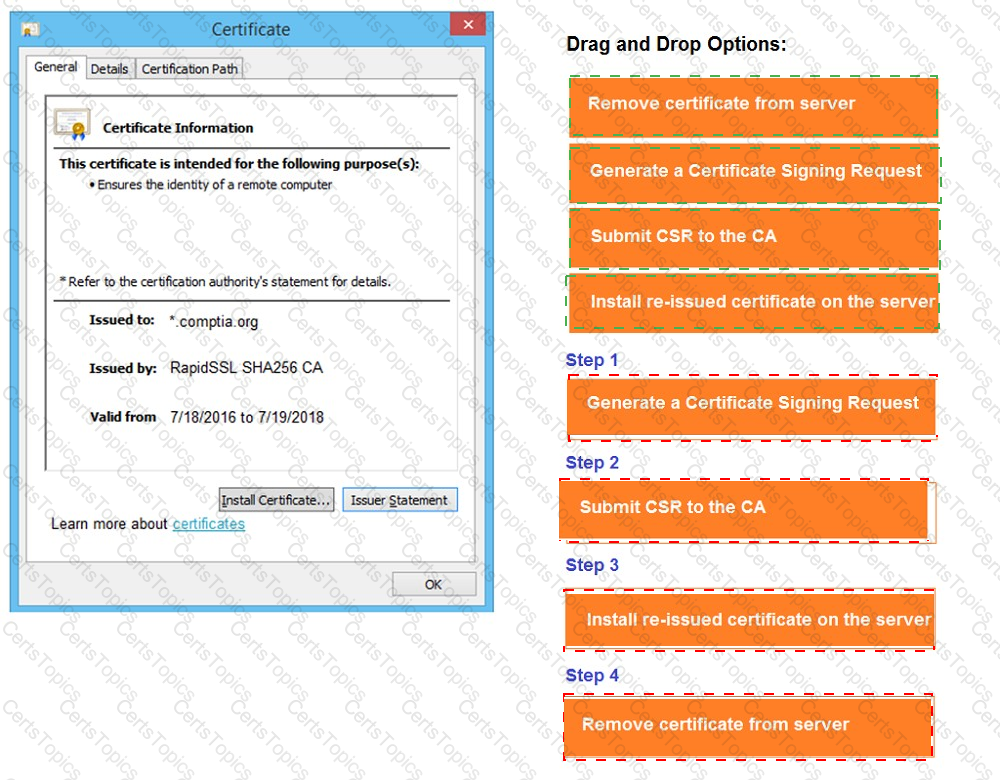
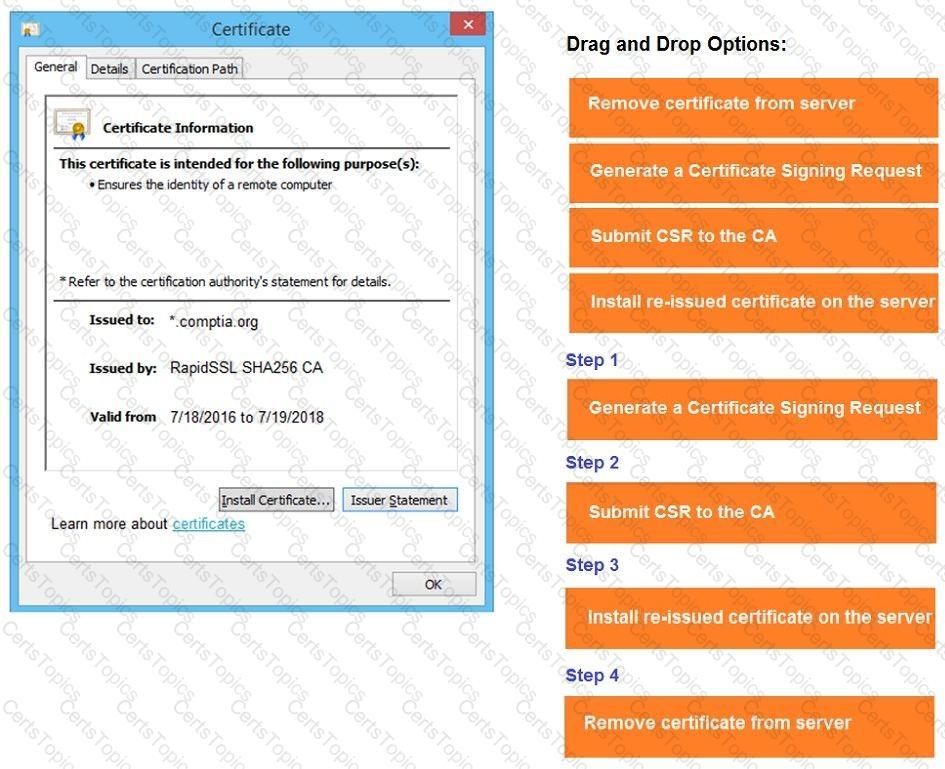
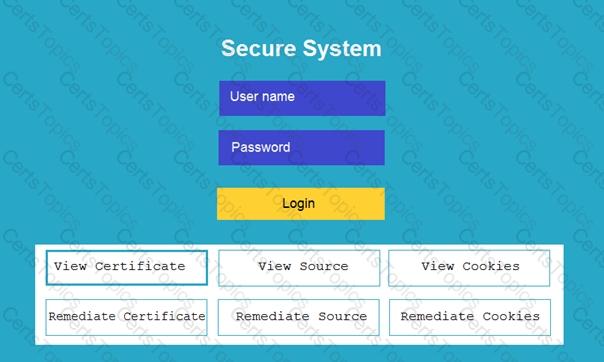
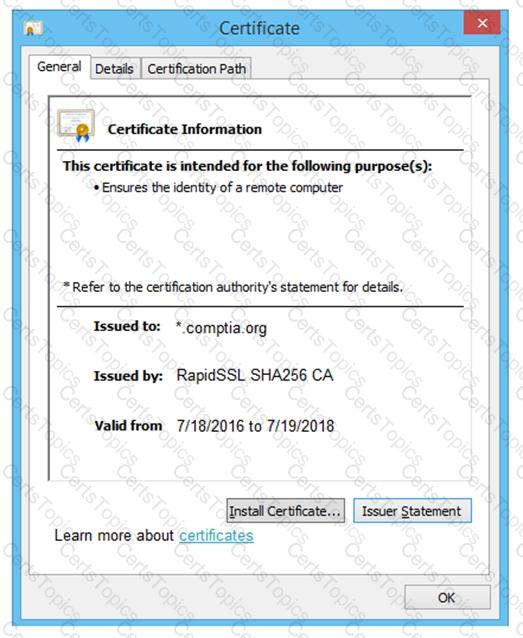
You are a penetration tester reviewing a client’s website through a web browser.

INSTRUCTIONS

Review all components of the website through the browser to determine if vulnerabilities are present.

Remediate ONLY the highest vulnerability from either the certificate, source, or cookies.

If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.

Options: