
Power Up Your Study Prep: Black Friday 75% Discount! Use coupon code below to save! - Ends in 0d 00h 00m 00s - Coupon code: big75certs

Note! The CS0-003 Exam is no longer valid. To find out more, please contact us through our Live Chat or email us.

CompTIA CS0-003 Exam With Confidence Using Practice Dumps

Exam Code:
CS0-003
Exam Name:
CompTIA CyberSecurity Analyst CySA+ Certification Exam
Certification:
Vendor:
Questions:
515
Last Updated:
Oct 23, 2026
Exam Status:
Stable
CompTIA CS0-003

CS0-003: CompTIA CySA+ Exam 2025 Study Guide Pdf and Test Engine

Are you worried about passing the CompTIA CS0-003 (CompTIA CyberSecurity Analyst CySA+ Certification Exam) exam? Download the most recent CompTIA CS0-003 braindumps with answers that are 100% real. After downloading the CompTIA CS0-003 exam dumps training , you can receive 99 days of free updates, making this website one of the best options to save additional money. In order to help you prepare for the CompTIA CS0-003 exam questions and verified answers by IT certified experts, CertsTopics has put together a complete collection of dumps questions and answers. To help you prepare and pass the CompTIA CS0-003 exam on your first attempt, we have compiled actual exam questions and their answers. 

Our (CompTIA CyberSecurity Analyst CySA+ Certification Exam) Study Materials are designed to meet the needs of thousands of candidates globally. A free sample of the CompTIA CS0-003 test is available at CertsTopics. Before purchasing it, you can also see the CompTIA CS0-003 practice exam demo.

CompTIA CyberSecurity Analyst CySA+ Certification Exam Questions and Answers

Question 1

After an upgrade to a new EDR, a security analyst received reports that several endpoints were not communicating with the SaaS provider to receive critical threat signatures. To comply with the incident response playbook, the security analyst was required to validate connectivity to ensure communications. The security analyst ran a command that provided the following output:

    ComputerName: comptia007

    RemotePort: 443

    InterfaceAlias: Ethernet 3

    TcpTestSucceeded: False

Which of the following did the analyst use to ensure connectivity?

Options:

A.

nmap

B.

tnc

C.

ping

D.

tracert

Buy Now
Question 2

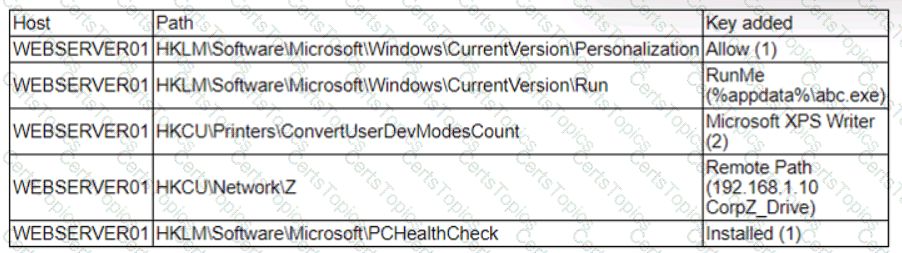
A security analyst is reviewing the following alert that was triggered by FIM on a critical system:

Which of the following best describes the suspicious activity that is occurring?

Options:

A.

A fake antivirus program was installed by the user.

B.

A network drive was added to allow exfiltration of data

C.

A new program has been set to execute on system start

D.

The host firewall on 192.168.1.10 was disabled.

Question 3

A company is in the process of implementing a vulnerability management program. no-lich of the following scanning methods should be implemented to minimize the risk of OT/ICS devices malfunctioning due to the vulnerability identification process?

Options:

A.

Non-credentialed scanning

B.

Passive scanning

C.

Agent-based scanning

D.

Credentialed scanning