
Winter Sale 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: save70

CompTIA CAS-005 Exam With Confidence Using Practice Dumps

Exam Code:
CAS-005
Exam Name:
CompTIA SecurityX Certification Exam
Certification:
Vendor:
Questions:
344
Last Updated:
Nov 5, 2026
Exam Status:
Stable
CompTIA CAS-005

CAS-005: CompTIA CASP Exam 2025 Study Guide Pdf and Test Engine

Are you worried about passing the CompTIA CAS-005 (CompTIA SecurityX Certification Exam) exam? Download the most recent CompTIA CAS-005 braindumps with answers that are 100% real. After downloading the CompTIA CAS-005 exam dumps training , you can receive 99 days of free updates, making this website one of the best options to save additional money. In order to help you prepare for the CompTIA CAS-005 exam questions and verified answers by IT certified experts, CertsTopics has put together a complete collection of dumps questions and answers. To help you prepare and pass the CompTIA CAS-005 exam on your first attempt, we have compiled actual exam questions and their answers. 

Our (CompTIA SecurityX Certification Exam) Study Materials are designed to meet the needs of thousands of candidates globally. A free sample of the CompTIA CAS-005 test is available at CertsTopics. Before purchasing it, you can also see the CompTIA CAS-005 practice exam demo.
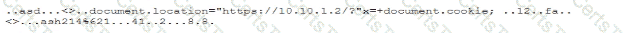

CompTIA SecurityX Certification Exam Questions and Answers

Question 1

A security architect is mitigating a vulnerability that previously led to a web application data breach. An analysis into the root cause of the issue finds the following:

An administrator’s account was hijacked and used on several Autonomous System Numbers within 30 minutes.

All administrators use named accounts that require multifactor authentication.

Single sign-on is used for all company applications.Which of the following should the security architect do to mitigate the issue?

Options:

A.

Configure token theft detection on the single sign-on system with automatic account lockouts.

B.

Enable context-based authentication when network locations change on administrator login attempts.

C.

Decentralize administrator accounts and force unique passwords for each application.

D.

Enforce biometric authentication requirements for the administrator’s named accounts.

Buy Now
Question 2

During a forensic review of a cybersecurity incident, a security engineer collected a portion of the payload used by an attacker on a comprised web server Given the following portion of the code:

Which of the following best describes this incident?

Options:

A.

XSRF attack

B.

Command injection

C.

Stored XSS

D.

SQL injection

Question 3

Developers have been creating and managing cryptographic material on their personal laptops fix use in production environment. A security engineer needs to initiate a more secure process. Which of thefollowing is the best strategy for the engineer to use?

Options:

A.

Disabling the BIOS and moving to UEFI

B.

Managing secrets on the vTPM hardware

C.

Employing shielding lo prevent LMI

D.

Managing key material on a HSM