
CompTIA Related Exams
CAS-005 Exam
An analyst needs to identify security event trends. The following is an excerpt from the SIEM:
Time
Alert
Source
Destination
20250407-UTC
Successful login from uncommon auth method in 24 hours
user1
AD-DC-01.corp
20250407-UTC
User accessed sensitive resources
user1
NFS-01/financial/share
20250407-UTC
Potential password spraying from host
10.10.15.100
iga-server.corp
20250407-UTC
Threshold exceeded user visiting high risk websites
user2
freehacks.com
20250407-UTC
Risk score exceeded for user
user1
bar.ru
20250407-UTC
NULL
NULL
NULL
Which of the following is the most practical way to identify trends?
A company designs policies and procedures for hardening containers deployed in the production environment. However, a security assessment reveals that deployed containers are not complying with the security baseline. Which of the following solutions best addresses this issue throughout early life-cycle stages?
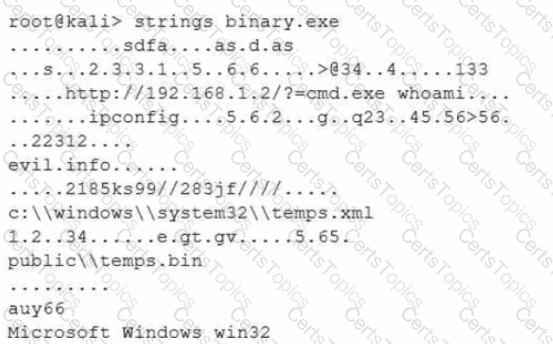
After a cybersecurity incident, a security analyst was able to collect a binary that the attacker used on the compromised server. Then the analyst ran the following command:
Which of the following options describes what the analyst is trying to do?