
Halloween Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: big75certs

NSEI_OTS_AR-7.6 Exam Dumps : Fortinet NSE I - OT Security 7.6 Architect

PDF
NSEI_OTS_AR-7.6 pdf
 Real Exam Questions and Answer
 Last Update: Oct 18, 2026
 Question and Answers: 56 With Explanation
 Compatible with all Devices
 Printable Format
 100% Pass Guaranteed
$21.25  $84.99
NSEI_OTS_AR-7.6 exam
PDF + Testing Engine
NSEI_OTS_AR-7.6 PDF + engine
 Both PDF & Practice Software
 Last Update: Oct 18, 2026
 Question and Answers: 56
 Discount Offer
 Download Free Demo
 24/7 Customer Support
$33.75  $134.99
Testing Engine
NSEI_OTS_AR-7.6 Engine
 Desktop Based Application
 Last Update: Oct 18, 2026
 Question and Answers: 56
 Create Multiple Test Sets
 Questions Regularly Updated
  90 Days Free Updates
  Windows and Mac Compatible
$25  $99.99

Verified By IT Certified Experts

CertsTopics.com Certified Safe Files

Up-To-Date Exam Study Material

99.5% High Success Pass Rate

100% Accurate Answers

Instant Downloads

Exam Questions And Answers PDF

Try Demo Before You Buy

Certification Exams with Helpful Questions And Answers

Fortinet NSE I - OT Security 7.6 Architect Questions and Answers

Question 1

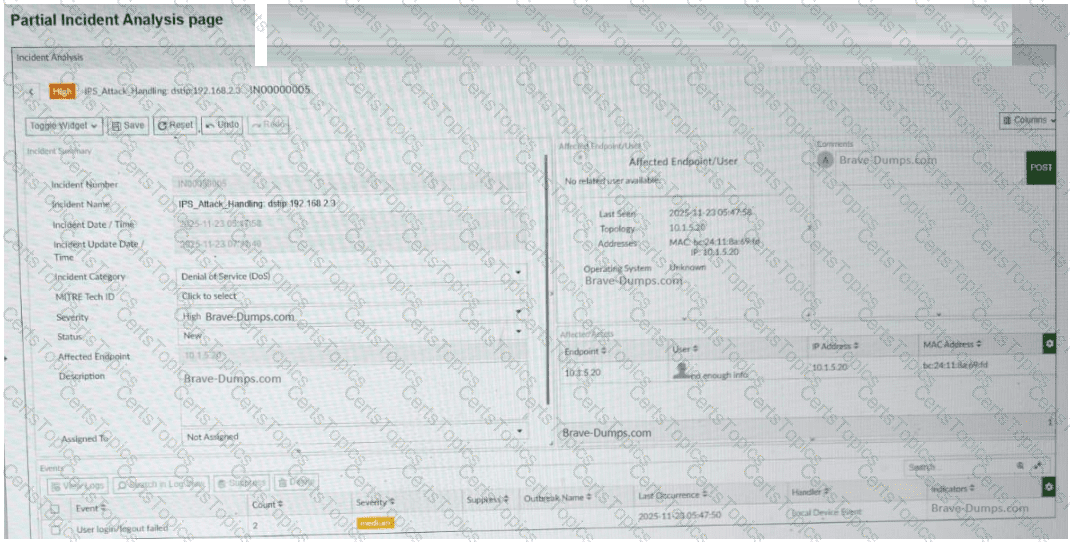
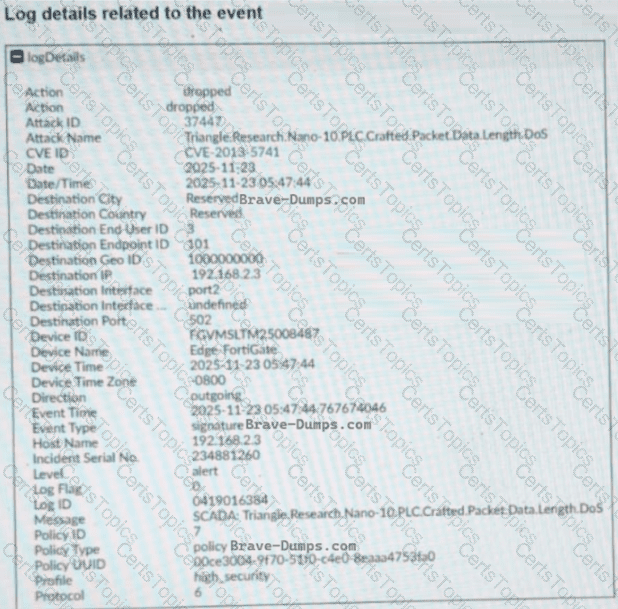
Refer to the exhibits.

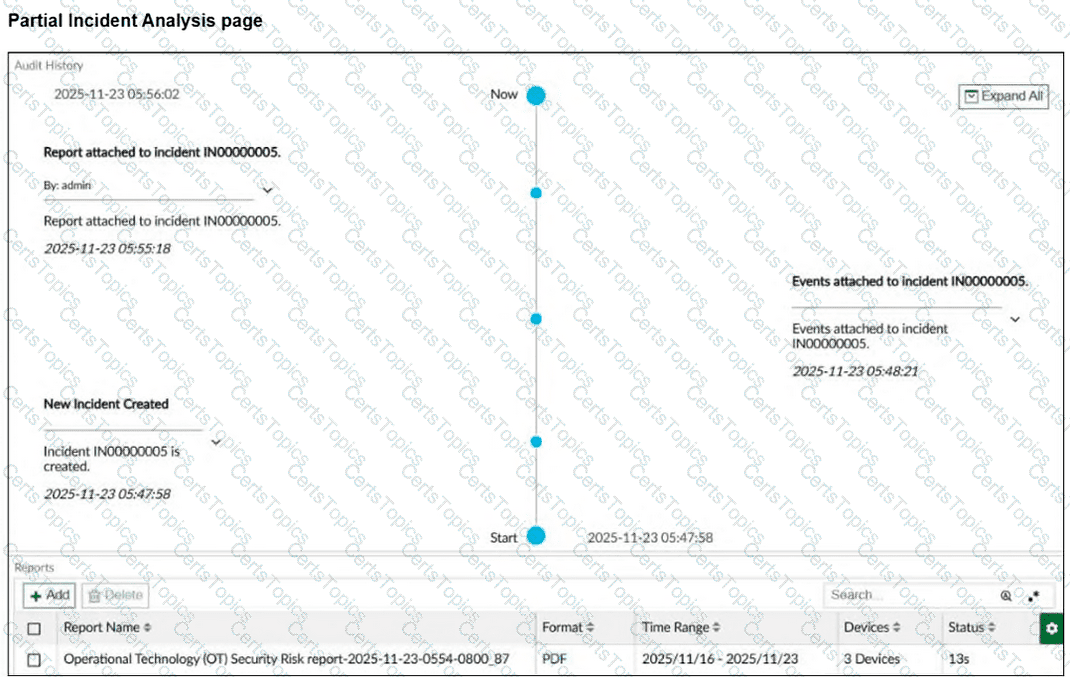
A partial Incident Analysis page and the log details related to the event are shown. An attack is reported on your OT network. You analyze the corresponding incident. Based on the information provided on the Incident Analysis page and the log details, which two statements are correct? (Choose two answers)

Options:

A.

The attack uses the Modbus protocol.

B.

The attack is mitigated.

C.

The attack uses the IEC 104 protocol.

D.

The event severity is high.

E.

The target device IP address is 10.1.5.20.

Buy Now
Question 2

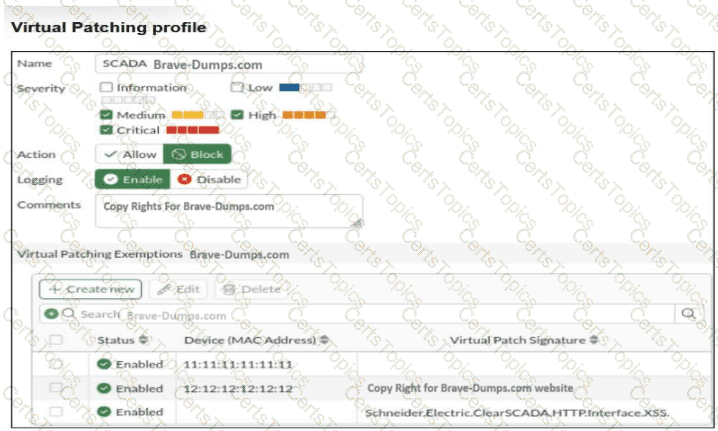
Refer to the exhibit.

A Virtual Patching profile is shown. You have recently updated your SCADA system and would like to apply the SCADA virtual patching profile. Which two statements about this profile are correct? (Choose two answers)

Options:

A.

Only the vulnerability Schneider.Electric.ClearSCADA.HTTP.Interface.XSS is still present.

B.

Low severity signatures are not blocked for the device with the MAC address 12:12:12:12:12.

C.

This profile blocks critical severity signatures for all the devices.

D.

The device with the MAC address 11:11:11:11:11 is considered to have no vulnerabilities.

Question 3

Refer to the exhibit.

A partial Incident Analysis page is shown. How was the 360-Degree Security Review OT report attached to the incident? (Choose one answer)

Options:

A.

Automatically by a stitch

B.

Automatically by an event handler

C.

Automatically by a playbook

D.

Manually by an administrator