Pre-Winter Sale 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: save70

Free and Premium Fortinet NSEI_OTS_AR-7.6 Dumps Questions Answers

Fortinet NSE I - OT Security 7.6 Architect Questions and Answers

Question 1

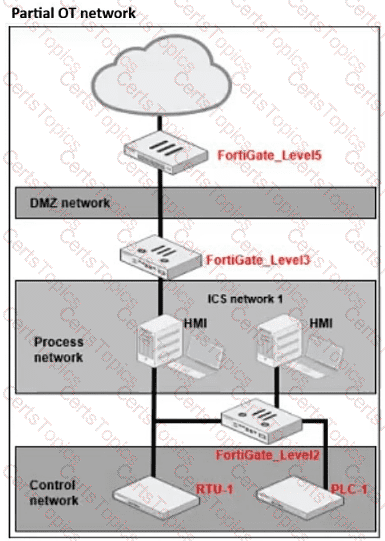
Refer to the exhibit.
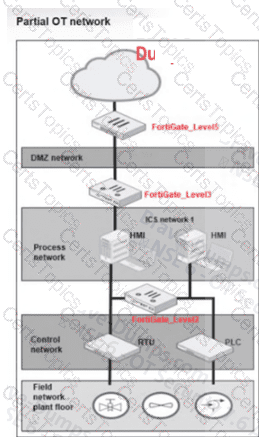
A partial OT network is shown. In this OT network, you must add additional security measures to detect OT protocols and, therefore, increase the traffic visibility. Which security sensor must you implement to detect the OT protocols in this network? (Choose one answer)

Options:

A.

Device detection on all the FortiGate interfaces.

B.

Inline IDS on FortiGate_Level3.

C.

Application sensor set to monitor on all the FortiGate devices.

D.

IPS sensor on FortiGate_Level5.

Buy Now
Question 2

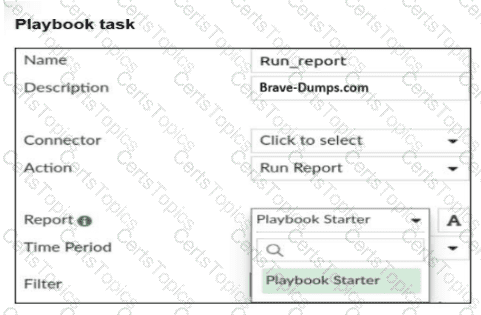
Refer to the exhibit.

A Run_report task is shown. You want to automate the generation of a newly created report on FortiAnalyzer . When you configure the Run_report task in Playbook, why is the report not shown in the Report field? (Choose two answers)

Options:

A.

You must first configure the connector.

B.

You must first enable Extended Log Filtering in the report.

C.

You must first enable Auto-cache in the report.

D.

You must first configure an event handler.

E.

You must first select Playbook Starter, and then select the newly created report.

Question 3

You want to protect OT devices that are not updated against known vulnerabilities so you apply virtual patching to the firewall policies. What must you check to confirm that the OT devices are virtually patched? (Choose one answer)

Options:

A.

The output of the CLI command get virtual-patch profile

B.

The OT View page

C.

The output of the CLI command get rule otvp status

D.

The Asset Identity List page

Question 4

In your OT environment, you want to detect the devices passively. Which two methods must you implement? (Choose two answers)

Options:

A.

SSH

B.

SNMP

C.

Vendor OUI

D.

Network traffic

Question 5

As the first step in your OT network protection plan, you must identify the OT protocols that the FortiGate device supports. Which two configurations must you implement on this FortiGate device? (Choose two answers)

Options:

A.

You must enable Device detection on all the interfaces.

B.

You must implement an Application Control security profile that monitors OT.

C.

You must enable the OT signatures.

D.

You must implement an Intrusion Prevention security profile that monitors OT.

Question 6

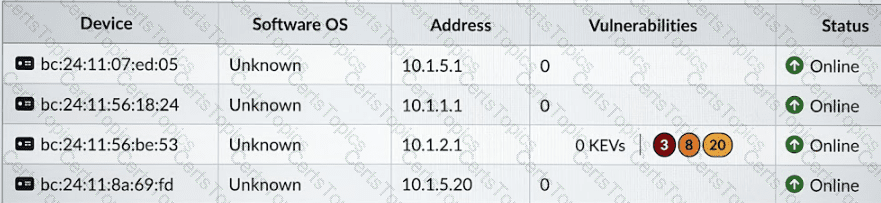
Refer to the exhibit.

Which statement about this partial Asset Identity List page is correct? (Choose one answer)

Options:

A.

A firewall policy has an Antivirus security profile applied to it.

B.

A firewall policy has a Virtual Patching security profile applied to it.

C.

A firewall policy has an Intrusion Prevention security profile applied to it.

D.

A firewall policy has an Application Control security profile applied to it.

Question 7

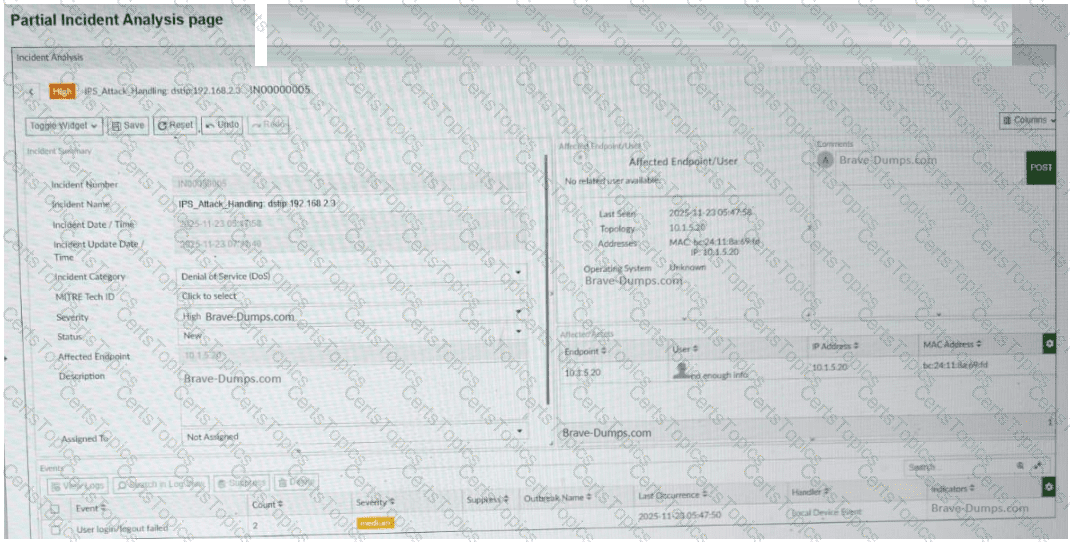
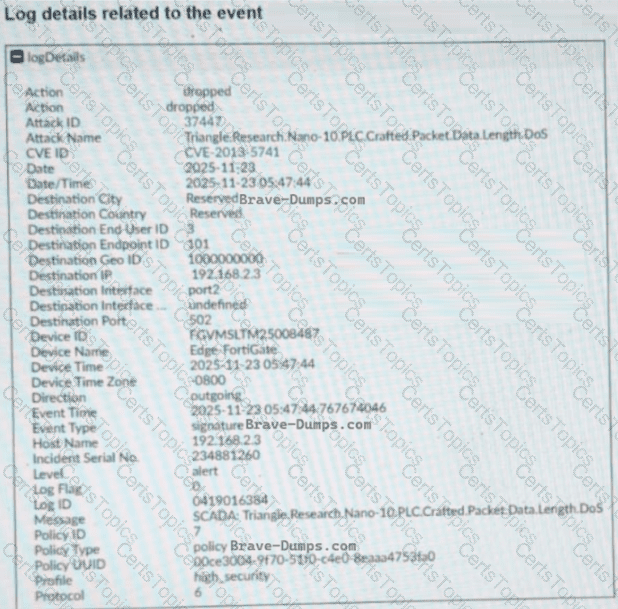
Refer to the exhibits.

A partial Incident Analysis page and the log details related to the event are shown. An attack is reported on your OT network. You analyze the corresponding incident. Based on the information provided on the Incident Analysis page and the log details, which two statements are correct? (Choose two answers)

Options:

A.

The attack uses the Modbus protocol.

B.

The attack is mitigated.

C.

The attack uses the IEC 104 protocol.

D.

The event severity is high.

E.

The target device IP address is 10.1.5.20.

Question 8

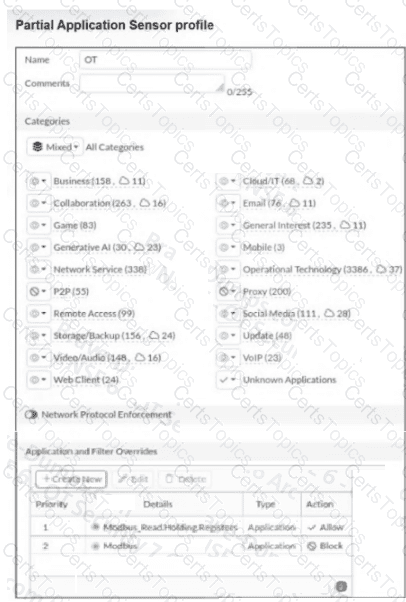
Refer to the exhibit.

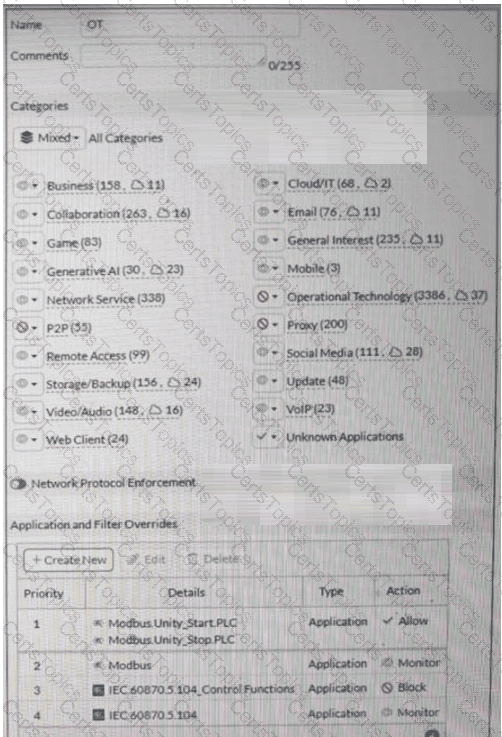
A partial Application Sensor profile is shown. When you apply this profile in a firewall policy, which two statements are correct? (Choose two answers)

Options:

A.

A log is provided for each IEC command.

B.

A log is provided for each Modbus command.

C.

OT signatures are enabled.

D.

All OT protocols are blocked.

Question 9

During layer 2 polling , which two pieces of information are gathered by FortiNAC to identify a device? (Choose two answers)

Options:

A.

Where it was learned

B.

The MAC-to-IP correlation learned

C.

The system name learned

D.

The time it was learned

Question 10

Refer to the exhibit.

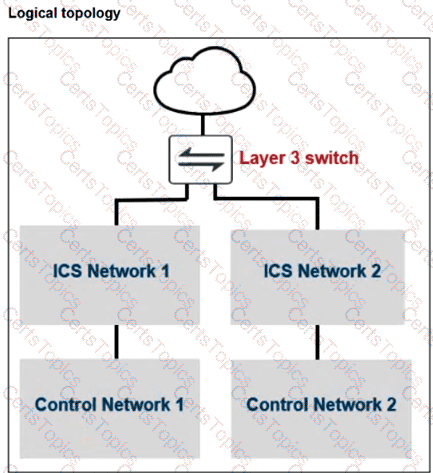
A partial OT network is shown. You must improve the security of this OT network and implement internal segmentation between network 1 and network 2. How can you achieve the segmentation? (Choose one answer)

Options:

A.

You can configure universal ZTNA.

B.

You can configure one traffic VDOM.

C.

You can configure an explicit software switch.

D.

You can configure forward domain IDs for each network.

Question 11

Refer to the exhibit.

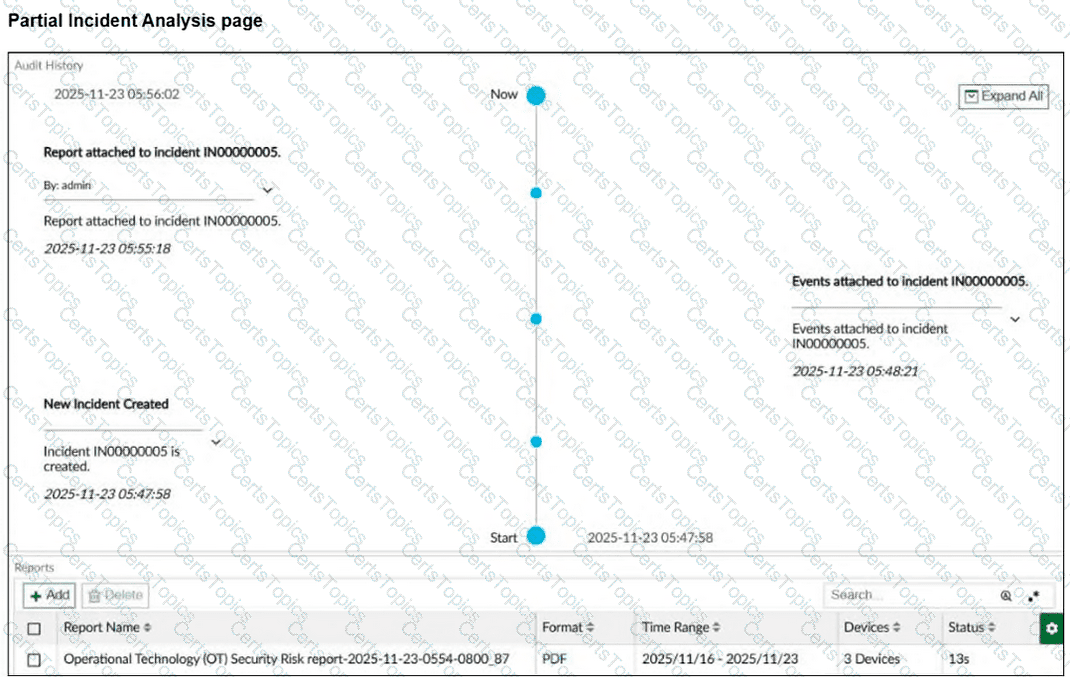
A partial Incident Analysis page is shown. How was the 360-Degree Security Review OT report attached to the incident? (Choose one answer)

Options:

A.

Automatically by a stitch

B.

Automatically by an event handler

C.

Automatically by a playbook

D.

Manually by an administrator

Question 12

Refer to the exhibit.

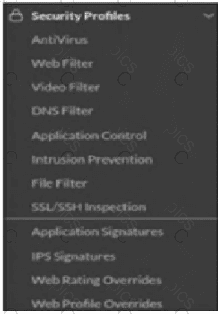
The OT devices behind the ruggedized FortiGate have vulnerabilities and you want to apply a virtual patching profile in the firewall policy. Why is Virtual Patching not available in the Security Profiles section? (Choose one answer)

Options:

A.

You must enable Virtual Patching in the Feature Visibility section.

B.

You must have a ruggedized FortiGate allowing the virtual patching feature.

C.

You must enable OT signatures.

D.

You must have a valid OT security service license.

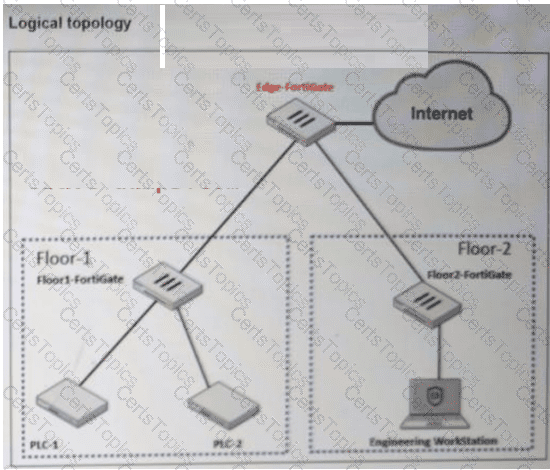
Question 13

Refer to the exhibit.

A partial OT network is shown. You have encountered many disconnections in the links and want to improve the availability of this network. Which action can you perform? (Choose one answer)

Options:

A.

You can implement HA clusters.

B.

You can implement SD-WAN at Floor-1-FortiGate and Floor-2-FortiGate.

C.

You can implement parallel redundancy protocol.

D.

You can implement VDOMs in Edge-FortiGate.

Question 14

Refer to the exhibit.

A partial OT network is shown.

PLC-1 has a known critical vulnerability, but you cannot update it.

What must you configure to protect PLC-1?

Options:

A.

OT signatures on FortiGate_Level3

B.

IPS on FortiGate_Level5

C.

Virtual patching on FortiGate_Level2

D.

OT application control on all FortiGate devices

Question 15

Refer to the exhibit.

A partial Application Sensor profile is shown. When you apply this profile in firewall policy, which two statements are correct? (Choose two answers)

Options:

A.

OT signatures are enabled.

B.

All OT protocols are monitored.

C.

Modbus write commands are blocked.

D.

A log is provided for each Modbus read holding registers command.

Question 16

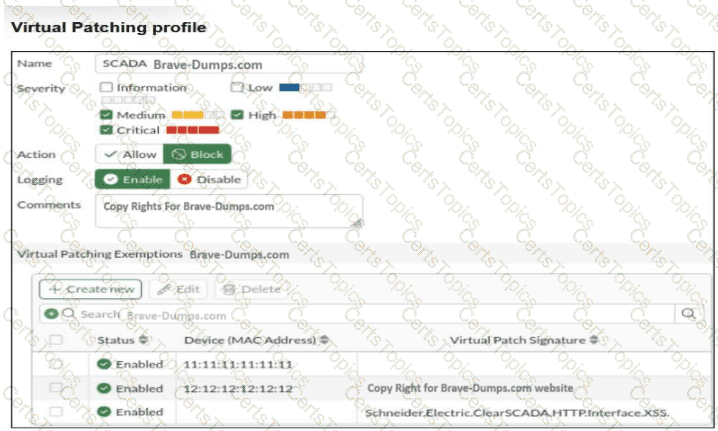
Refer to the exhibit.

A Virtual Patching profile is shown. You have recently updated your SCADA system and would like to apply the SCADA virtual patching profile. Which two statements about this profile are correct? (Choose two answers)

Options:

A.

Only the vulnerability Schneider.Electric.ClearSCADA.HTTP.Interface.XSS is still present.

B.

Low severity signatures are not blocked for the device with the MAC address 12:12:12:12:12.

C.

This profile blocks critical severity signatures for all the devices.

D.

The device with the MAC address 11:11:11:11:11 is considered to have no vulnerabilities.