
Halloween Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: big75certs

Fortinet NSE5_FWB_AD-8.0 Exam With Confidence Using Practice Dumps

Exam Code:
NSE5_FWB_AD-8.0
Exam Name:
Fortinet NSE 5 - FortiWeb 8.0 Administrator
Vendor:
Questions:
36
Last Updated:
Nov 2, 2026
Exam Status:
Stable
Fortinet NSE5_FWB_AD-8.0

NSE5_FWB_AD-8.0: NSE 5 Network Security Analyst Exam 2025 Study Guide Pdf and Test Engine

Are you worried about passing the Fortinet NSE5_FWB_AD-8.0 (Fortinet NSE 5 - FortiWeb 8.0 Administrator) exam? Download the most recent Fortinet NSE5_FWB_AD-8.0 braindumps with answers that are 100% real. After downloading the Fortinet NSE5_FWB_AD-8.0 exam dumps training , you can receive 99 days of free updates, making this website one of the best options to save additional money. In order to help you prepare for the Fortinet NSE5_FWB_AD-8.0 exam questions and verified answers by IT certified experts, CertsTopics has put together a complete collection of dumps questions and answers. To help you prepare and pass the Fortinet NSE5_FWB_AD-8.0 exam on your first attempt, we have compiled actual exam questions and their answers. 

Our (Fortinet NSE 5 - FortiWeb 8.0 Administrator) Study Materials are designed to meet the needs of thousands of candidates globally. A free sample of the CompTIA NSE5_FWB_AD-8.0 test is available at CertsTopics. Before purchasing it, you can also see the Fortinet NSE5_FWB_AD-8.0 practice exam demo.

Fortinet NSE 5 - FortiWeb 8.0 Administrator Questions and Answers

Question 1

Which URL should you rewrite to reduce security risk?

Buy Now
Question 2

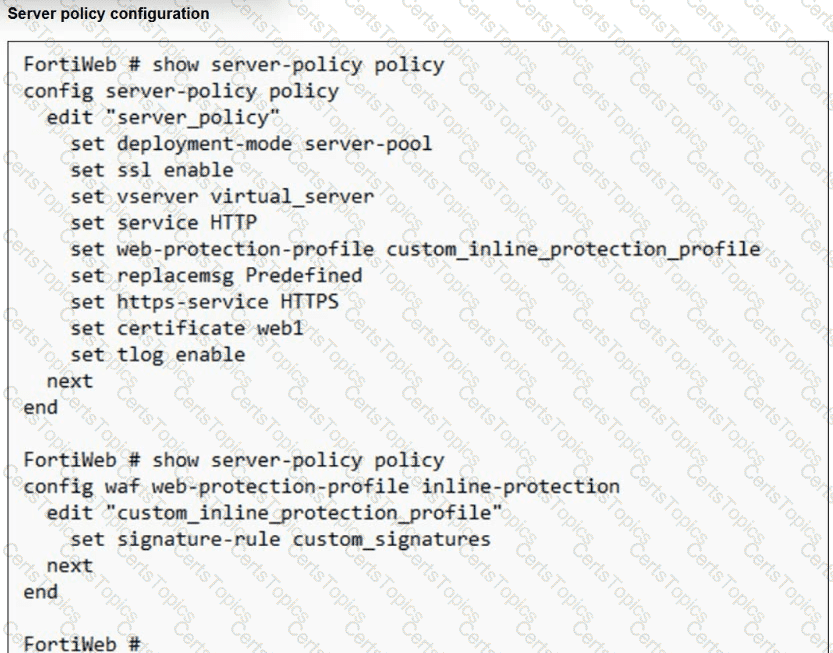
Refer to the exhibit.

You have deployed FortiWeb behind a FortiGate that is configured as a reverse proxy and inserts the X-Forwarded-For HTTP header when forwarding HTTP and HTTPS traffic.

FortiWeb is using a custom inline protection profile, and logging is enabled, as shown in the exhibit.

You notice that FortiWeb is blocking legitimate users, and all requests in the attack logs appear to come from the FortiGate IP address, not the original client IP address.

Which action should you take to fix this issue?

Options:

A.

Replace the current deployment mode with a one-arm proxy to expose source IP addresses.

B.

Disable IP-based detection features on FortiWeb to avoid IP-related blocking.

C.

Recreate the server policy using the predefined profile instead of a custom one.

D.

Modify the protection profile to use the X-Forwarded-For header for client IP address detection.

Question 3

You are a FortiWeb administrator investigating an SQL injection attack on your company’s customer portal. The network firewall and intrusion prevention system (IPS) did not stop the attack.

You decide to deploy a web application firewall (WAF) to help prevent this type of attack.

Which two actions can you take to block application-layer threats? (Choose two.)

Options:

A.

Focus on client-side risks, such as protecting user browsers.

B.

Inspect general network traffic equally between clients and servers.

C.

Detect and block threats like SQL injection, cross-site scripting (XSS), and other Layer 7 attacks.

D.

Filter and analyze HTTP/S requests to block attacks targeting the web server.