
Power Up Your Study Prep: Black Friday 75% Discount! Use coupon code below to save! - Ends in 0d 00h 00m 00s - Coupon code: big75certs

PECB ISO-IEC-27001-Lead-Auditor Exam With Confidence Using Practice Dumps

Exam Code:
ISO-IEC-27001-Lead-Auditor
Exam Name:
PECB Certified ISO/IEC 27001 2022 Lead Auditor exam
Certification:
Vendor:
Questions:
418
Last Updated:
Nov 16, 2026
Exam Status:
Stable
PECB ISO-IEC-27001-Lead-Auditor

ISO-IEC-27001-Lead-Auditor: ISO 27001 Exam 2025 Study Guide Pdf and Test Engine

Are you worried about passing the PECB ISO-IEC-27001-Lead-Auditor (PECB Certified ISO/IEC 27001 2022 Lead Auditor exam) exam? Download the most recent PECB ISO-IEC-27001-Lead-Auditor braindumps with answers that are 100% real. After downloading the PECB ISO-IEC-27001-Lead-Auditor exam dumps training , you can receive 99 days of free updates, making this website one of the best options to save additional money. In order to help you prepare for the PECB ISO-IEC-27001-Lead-Auditor exam questions and verified answers by IT certified experts, CertsTopics has put together a complete collection of dumps questions and answers. To help you prepare and pass the PECB ISO-IEC-27001-Lead-Auditor exam on your first attempt, we have compiled actual exam questions and their answers. 

Our (PECB Certified ISO/IEC 27001 2022 Lead Auditor exam) Study Materials are designed to meet the needs of thousands of candidates globally. A free sample of the CompTIA ISO-IEC-27001-Lead-Auditor test is available at CertsTopics. Before purchasing it, you can also see the PECB ISO-IEC-27001-Lead-Auditor practice exam demo.

PECB Certified ISO/IEC 27001 2022 Lead Auditor exam Questions and Answers

Question 1

You are performing an ISMS audit at a residential nursing home called ABC that provides healthcare services.

The next step in your audit plan is to verify the information security on ABC's healthcare mobile app

development, support, and lifecycle process. During the audit, you learned the organization outsourced the

mobile app development to a professional software development company with CMMI Level 5, ITSM (ISO/IEC

20000-1), BCMS (ISO 22301) and ISMS (ISO/IEC 27001) certified. The IT Manager presented the software

security management procedure and summarised the process as follows:

The mobile app development shall adopt "security-by-design" and "security-by-default" principles, as a

minimum. The following security functions for personal data protection shall be available:

Access control.

Personal data encryption, i.e., Advanced Encryption Standard (AES) algorithm, key lengths: 256 bits; and

Personal data pseudonymization.

Vulnerability checked and no security backdoor

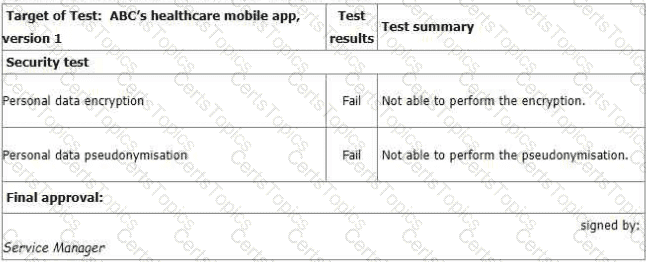
You sample the latest Mobile App Test report - details as follows:

You ask the IT Manager why the organisation still uses the mobile app while personal data

encryption and pseudonymization tests failed. Also, whether the Service Manager is authorized to

approve the test.

The IT Manager explains the test results should be approved by him according to the software

security management procedure. The reason why the encryption and pseudonymization functions

failed is that these functions heavily slowed down the system and service performance. An extra

150% of resources are needed to cover this. The Service Manager agreed that access control is

good enough and acceptable. That's why the Service Manager signed the approval.

You sample one of the medical staff's mobile and found that ABC's healthcare mobile app, version

1.01 is installed. You found that version 1.01 has no test record.

The IT Manager explains that because of frequent ransomware attacks, the outsourced mobile app

development company gave a free minor update on the tested software, performed an emergency

release of the updated software, and gave a verbal guarantee that there will be no impact on any

security functions. Based on his 20 years of information security experience, there is no need to re-

test.

You are preparing the audit findings Select two options that are correct.

Options:

A.

There is a nonconformity (NC). The IT. Manager does not comply with the software security management procedure. (Relevant to clause 8.1, control A.8.30)

B.

There is a nonconformity (NC). The organisation does not control planned changes and review the consequences of unintended changes. (Relevant to clause 8.1)

C.

There is an opportunity for improvement (OI). The IT Manager should make the decision to continue the service based on appropriate testing. (Relevant to clause 8.1, control A.8.30)

D.

There is an opportunity for improvement (OI). The organisation selects an external service provider based on the extent of free services it will provide. (Relevant to clause 8.1, control A.5.21)

E.

There is NO nonconformity (NC). The IT Manager demonstrates good leadership. (Relevant to clause 5.1, control 5.4)

F.

There is NO nonconformity (NC). The IT Manager demonstrates he is fully competent. (Relevant to clause 7.2)

Buy Now
Question 2

Which one of the following statements best describes the purpose of conducting a document review?

    To reveal whether the documented management system is nonconforming with audit criteria and to gather evidence to support the audit report

Options:

A.

To decide about the conformity of the documented management system with audit standards and to gather findings to support the audit process

B.

To determine the conformity of the management system, as far as documented, with audit criteria and to gather information to support the on-site audit activities

C.

To detect any nonconformity of the management system, if documented, with audit criteria and to identify information to support the audit plan

Question 3

Scenario 5: Data Grid Inc. is a well-known company that delivers security services across the entire information technology infrastructure. It provides cybersecurity software, including endpoint security, firewalls, and antivirus software. For two decades, Data Grid Inc. has helped various companies secure their networks through advanced products and services. Having achieved reputation in the information and network security field, Data Grid Inc. decided to obtain the ISO/IEC 27001 certification to better secure its internal and customer assets and gain competitive advantage.

Data Grid Inc. appointed the audit team, who agreed on the terms of the audit mandate. In addition, Data Grid Inc. defined the audit scope, specified the audit criteria, and proposed to close the audit within five days. The audit team rejected Data Grid Inc.'s proposal to conduct the audit within five days, since the company has a large number of employees and complex processes. Data Grid Inc. insisted that they have planned to complete the audit within five days, so both parties agreed upon conducting the audit within the defined duration. The audit team followed a risk-based auditing approach.

To gain an overview of the main business processes and controls, the audit team accessed process descriptions and organizational charts. They were unable to perform a deeper analysis of the IT risks and controls because their access to the IT infrastructure and applications was restricted. However, the audit team stated that the risk that a significant defect could occur to Data Grid Inc.'s ISMS was low since most of the company's processes were automated. They therefore evaluated that the ISMS, as a whole, conforms to the standard requirements by asking the representatives of Data Grid Inc. the following questions:

•How are responsibilities for IT and IT controls defined and assigned?

•How does Data Grid Inc. assess whether the controls have achieved the desired results?

•What controls does Data Grid Inc. have in place to protect the operating environment and data from malicious software?

•Are firewall-related controls implemented?

Data Grid Inc.'s representatives provided sufficient and appropriate evidence to address all these questions.

The audit team leader drafted the audit conclusions and reported them to Data Grid Inc.'s top management. Though Data Grid Inc. was recommended for certification by the auditors, misunderstandings were raised between Data Grid Inc. and the certification body in regards to audit objectives. Data Grid Inc. stated that even though the audit objectives included the identification of areas for potential improvement, the audit team did not provide such information.

Based on this scenario, answer the following question:

Data Grid Inc. is responsible for all the actions below, EXCEPT:

Options:

A.

Specifying the audit criteria

B.

Appointing the audit team

C.

Defining the audit scope