Halloween Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: big75certs

Fortinet NSE6_FSM_AN-7.4 Exam With Confidence Using Practice Dumps

Exam Code:
NSE6_FSM_AN-7.4
Exam Name:
Fortinet NSE 6 - FortiSIEM 7.4 Analyst
Vendor:
Questions:
48
Last Updated:
Nov 3, 2026
Exam Status:
Stable
Fortinet NSE6_FSM_AN-7.4

NSE6_FSM_AN-7.4: NSE 6 Network Security Specialist Exam 2025 Study Guide Pdf and Test Engine

Are you worried about passing the Fortinet NSE6_FSM_AN-7.4 (Fortinet NSE 6 - FortiSIEM 7.4 Analyst) exam? Download the most recent Fortinet NSE6_FSM_AN-7.4 braindumps with answers that are 100% real. After downloading the Fortinet NSE6_FSM_AN-7.4 exam dumps training , you can receive 99 days of free updates, making this website one of the best options to save additional money. In order to help you prepare for the Fortinet NSE6_FSM_AN-7.4 exam questions and verified answers by IT certified experts, CertsTopics has put together a complete collection of dumps questions and answers. To help you prepare and pass the Fortinet NSE6_FSM_AN-7.4 exam on your first attempt, we have compiled actual exam questions and their answers. 

Our (Fortinet NSE 6 - FortiSIEM 7.4 Analyst) Study Materials are designed to meet the needs of thousands of candidates globally. A free sample of the CompTIA NSE6_FSM_AN-7.4 test is available at CertsTopics. Before purchasing it, you can also see the Fortinet NSE6_FSM_AN-7.4 practice exam demo.
Fortinet NSE 6 - FortiSIEM 7.4 Analyst Questions and Answers

Question 1

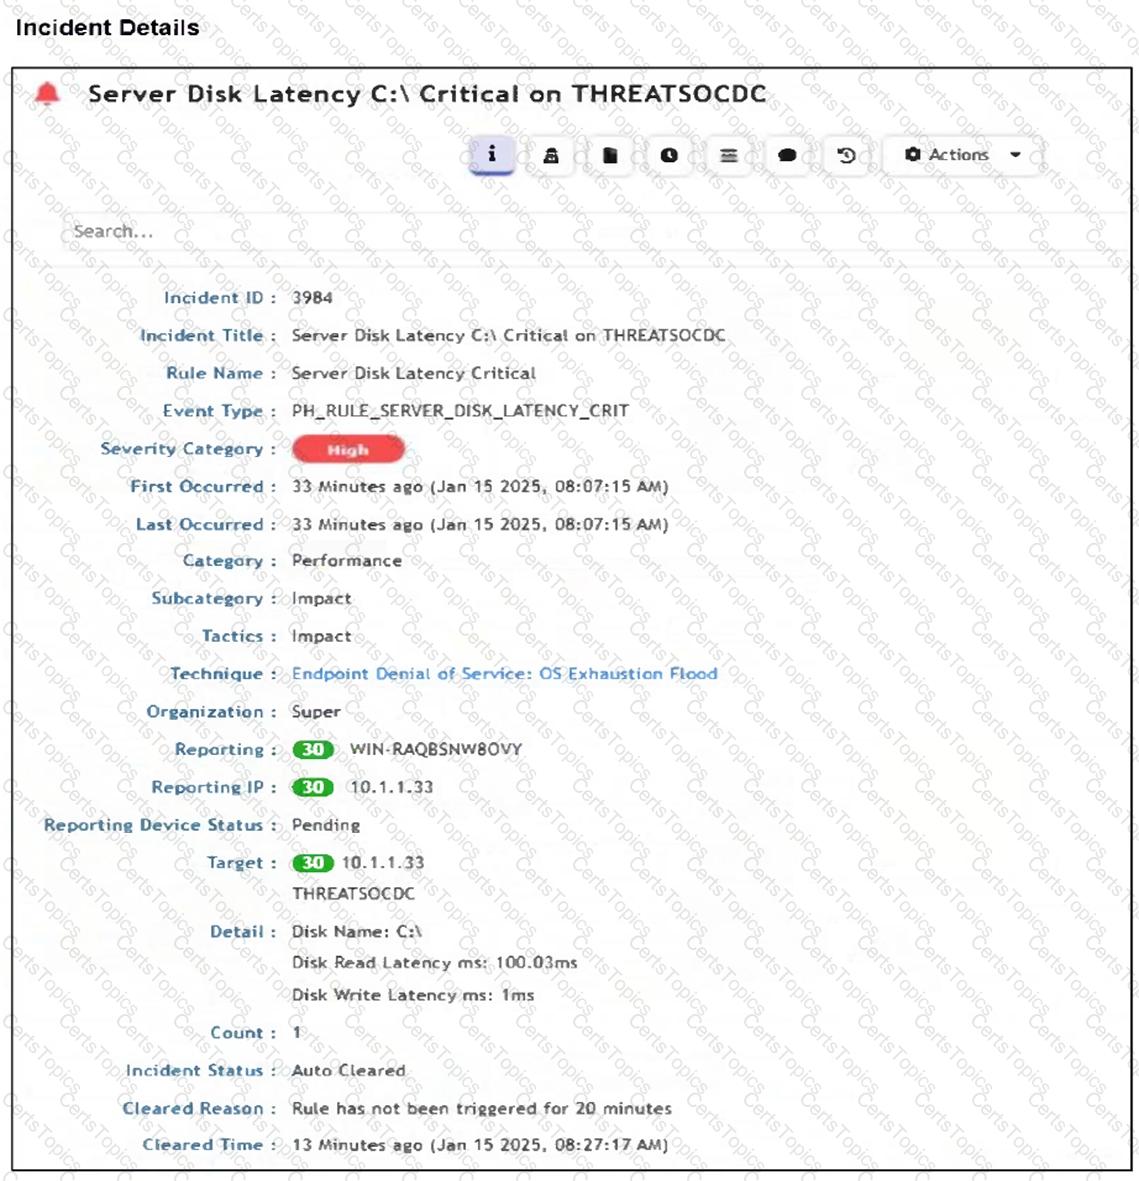
Refer to the exhibit.

How was this incident cleared?

Options:

A.

The analyst manually cleared the incident from the incident table.

B.

FortiSIEM cleared the incident automatically after 24 hours.

C.

The incident was cleared automatically by the rule.

D.

The endpoint was rebooted and sent an all-clear signal to FortiSIEM.

Buy Now
Question 2

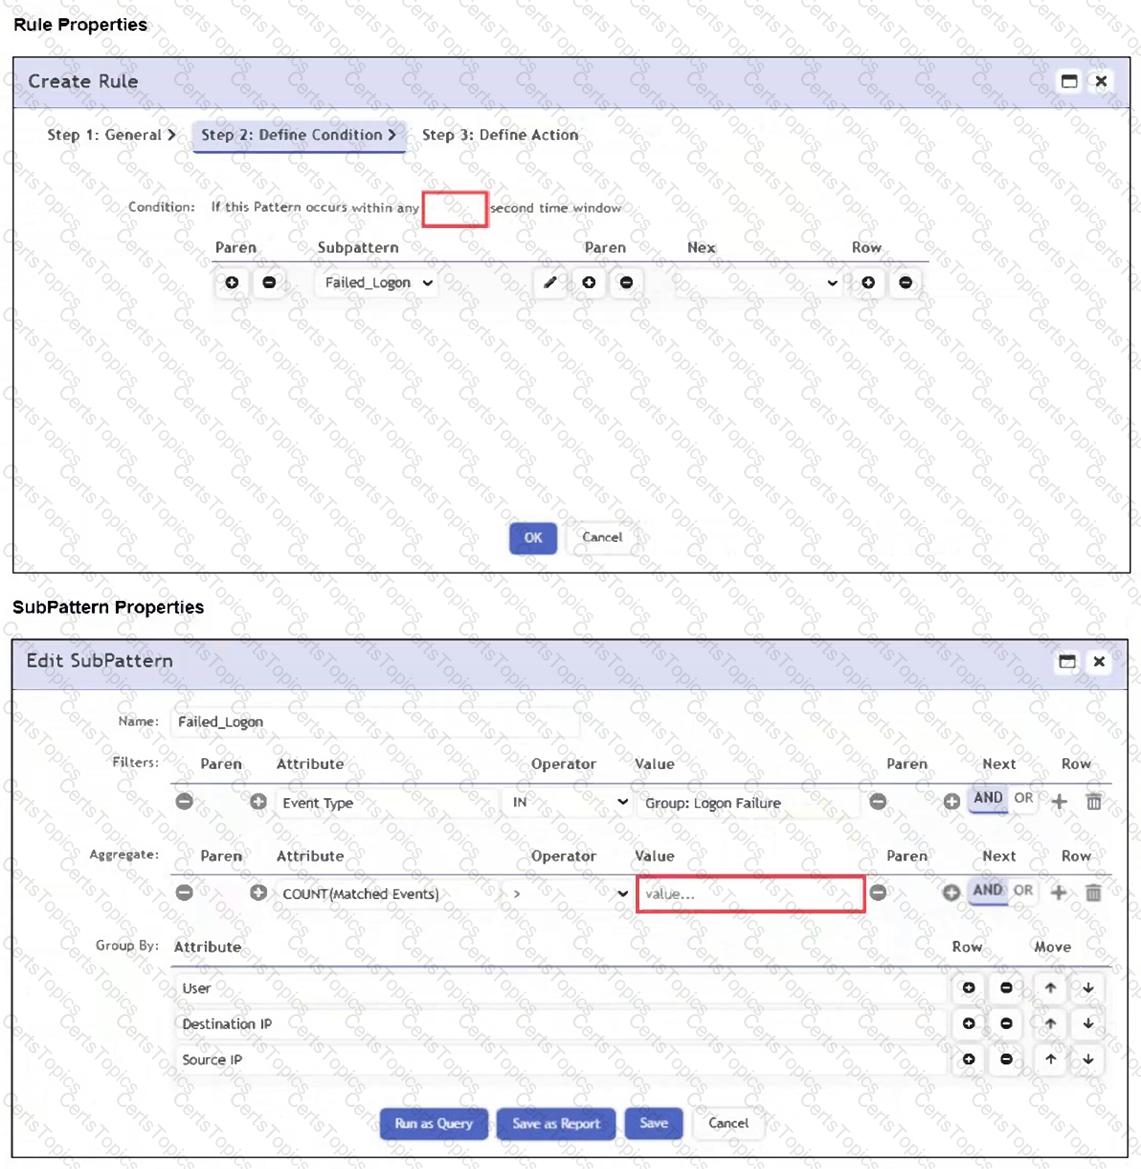
Refer to the exhibit.

An analyst wants the rule shown in the exhibit to trigger when three failed login attempts occur within three minutes.

What should the values be for the condition time window and aggregate count?

Options:

A.

Time window 180 seconds, aggregate count 3

B.

Time window 180 seconds, aggregate count 2

C.

Time window 90 seconds, aggregate count 3

D.

Time window 90 seconds, aggregate count 2

Question 3

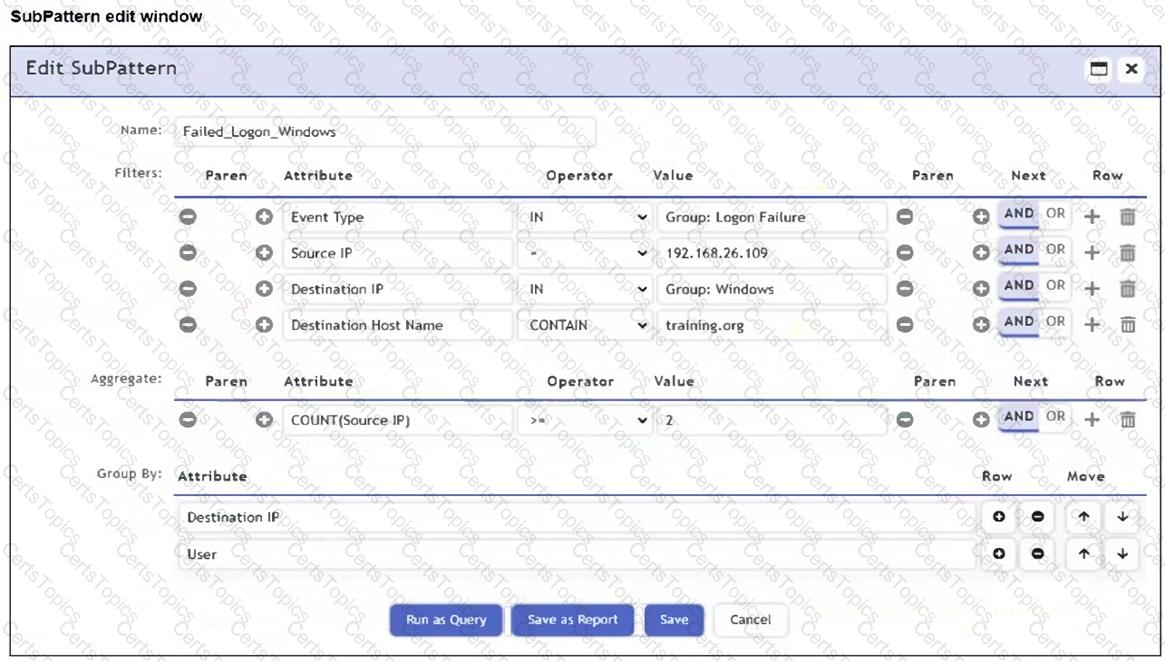
Refer to the exhibit.

An analyst is troubleshooting the rule shown in the exhibit. It is not generating any incidents, but the filter parameters are generating events on the Analytics tab.

What is wrong with the rule conditions?

Options:

A.

The Event Type refers to a CMDB lookup and should be an Event lookup.

B.

The Destination Host Name value is not fully qualified.

C.

The Group By attributes restricts which events are counted.

D.

The Aggregate attribute is too restrictive.