
Halloween Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: big75certs

NSE5_FWB_AD-8.0 Exam Dumps : Fortinet NSE 5 - FortiWeb 8.0 Administrator

PDF
NSE5_FWB_AD-8.0 pdf
 Real Exam Questions and Answer
 Last Update: Nov 2, 2026
 Question and Answers: 36 With Explanation
 Compatible with all Devices
 Printable Format
 100% Pass Guaranteed
$21.25  $84.99
NSE5_FWB_AD-8.0 exam
PDF + Testing Engine
NSE5_FWB_AD-8.0 PDF + engine
 Both PDF & Practice Software
 Last Update: Nov 2, 2026
 Question and Answers: 36
 Discount Offer
 Download Free Demo
 24/7 Customer Support
$33.75  $134.99
Testing Engine
NSE5_FWB_AD-8.0 Engine
 Desktop Based Application
 Last Update: Nov 2, 2026
 Question and Answers: 36
 Create Multiple Test Sets
 Questions Regularly Updated
  90 Days Free Updates
  Windows and Mac Compatible
$25  $99.99

Verified By IT Certified Experts

CertsTopics.com Certified Safe Files

Up-To-Date Exam Study Material

99.5% High Success Pass Rate

100% Accurate Answers

Instant Downloads

Exam Questions And Answers PDF

Try Demo Before You Buy

Certification Exams with Helpful Questions And Answers

Fortinet NSE 5 - FortiWeb 8.0 Administrator Questions and Answers

Question 1

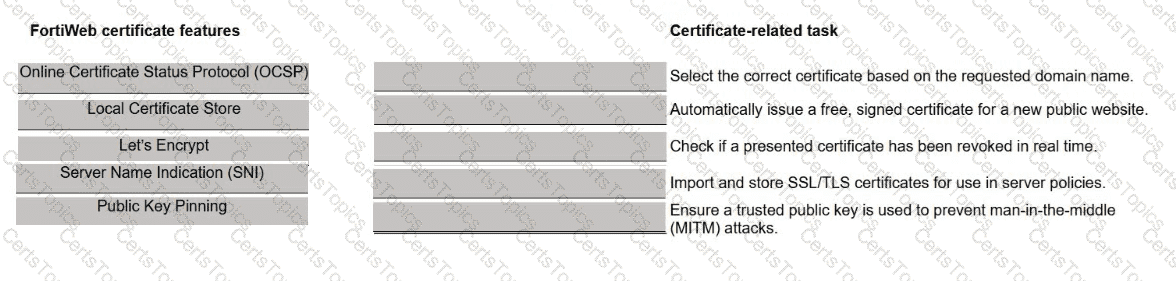
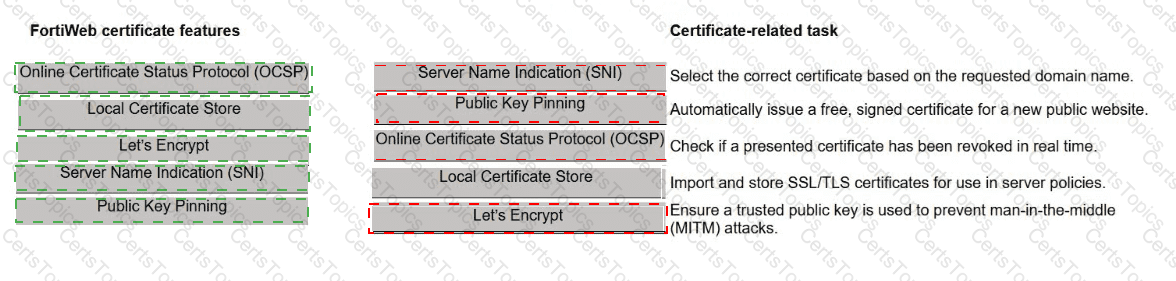
You are working on securing HTTPS communication across different services using FortiWeb. Your task is to configure and validate digital certificates for various traffic and communication needs.

Match each FortiWeb certificate feature to the certificate-related task that supports the feature.

Options:

Buy Now
Question 2

A third-party penetration test reveals that users can bypass login controls through a mobile API. Your current FortiWeb configuration includes zero trust network access (ZTNA) profiles and cookie security, but API protection and client management are not enabled. The security team asks you to recommend the most effective way to close this gap.

Which FortiWeb adjustment would best prevent future unauthorized API access?

Options:

A.

Switch to a reverse-proxy mode to bypass cookie-based controls.

B.

Enable API protection and client management to enforce identity checks on mobile API traffic.

C.

Replace ZTNA with bot protection to reduce false positives.

D.

Log only API traffic and rely on FortiAnalyzer for future alerts.

Question 3

You are a FortiWeb administrator investigating an SQL injection attack on your company’s customer portal. The network firewall and intrusion prevention system (IPS) did not stop the attack.

You decide to deploy a web application firewall (WAF) to help prevent this type of attack.

Which two actions can you take to block application-layer threats? (Choose two.)

Options:

A.

Focus on client-side risks, such as protecting user browsers.

B.

Inspect general network traffic equally between clients and servers.

C.

Detect and block threats like SQL injection, cross-site scripting (XSS), and other Layer 7 attacks.

D.

Filter and analyze HTTP/S requests to block attacks targeting the web server.