Pre-Winter Sale 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: save70

CompTIA CS0-004 Exam With Confidence Using Practice Dumps

Exam Code:
CS0-004
Exam Name:
CompTIA Cybersecurity Analyst CySA+ V4 (New Version)
Certification:
Vendor:
Questions:
82
Last Updated:
Sep 9, 2026
Exam Status:
Stable
CompTIA CS0-004

CS0-004: CompTIA CySA+ Exam 2025 Study Guide Pdf and Test Engine

Are you worried about passing the CompTIA CS0-004 (CompTIA Cybersecurity Analyst CySA+ V4 (New Version)) exam? Download the most recent CompTIA CS0-004 braindumps with answers that are 100% real. After downloading the CompTIA CS0-004 exam dumps training , you can receive 99 days of free updates, making this website one of the best options to save additional money. In order to help you prepare for the CompTIA CS0-004 exam questions and verified answers by IT certified experts, CertsTopics has put together a complete collection of dumps questions and answers. To help you prepare and pass the CompTIA CS0-004 exam on your first attempt, we have compiled actual exam questions and their answers. 

Our (CompTIA Cybersecurity Analyst CySA+ V4 (New Version)) Study Materials are designed to meet the needs of thousands of candidates globally. A free sample of the CompTIA CS0-004 test is available at CertsTopics. Before purchasing it, you can also see the CompTIA CS0-004 practice exam demo.
CompTIA Cybersecurity Analyst CySA+ V4 (New Version) Questions and Answers

Question 1

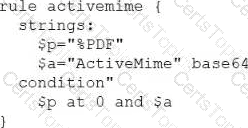
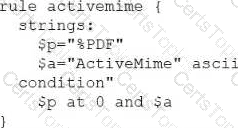
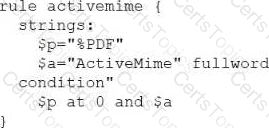
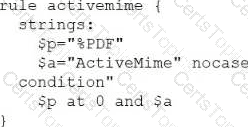
A security analyst must identify documents that contain encoded ActiveMime payloads in a directory containing thousands of files. The analyst runs the following command: grep -rail ActiveMime *

The command returns no output.

Which of the following Yet Another Recursive Acronym (YARA) rules should the analyst use to find the suspicious files?

A)

B)

C)

D)

Options:

A.

Option A

B.

Option B

C.

Option C

D.

Option D

Buy Now
Question 2

An analyst must provide a visualization of data received from threat intelligence sources. The data includes the Internet Protocols, services, and tools used by threat actors.

Which of the following is the best framework for the analyst to follow to display this data?

Options:

A.

Diamond Model of Intrusion Analysis

B.

Exploit Prediction Scoring System

C.

Cyber Kill Chain

D.

MITRE Adversarial Tactics, Techniques, and Common Knowledge and Detection, Denial, and Disruption Framework Empowering Network Defense

Question 3

Which of the following should a cybersecurity analyst utilize when a notification is inaccurate?

Options:

A.

Data enrichment

B.

Dashboard creation

C.

Threat hunting

D.

Alert tuning