Pre-Winter Sale 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: save70

CS0-004 Exam Dumps : CompTIA Cybersecurity Analyst CySA+ V4 (New Version)

PDF
CS0-004 pdf
 Real Exam Questions and Answer
 Last Update: Sep 9, 2026
 Question and Answers: 82
 Compatible with all Devices
 Printable Format
 100% Pass Guaranteed
$27  $90
CS0-004 exam
PDF + Testing Engine
CS0-004 PDF + engine
 Both PDF & Practice Software
 Last Update: Sep 9, 2026
 Question and Answers: 82
 Discount Offer
 Download Free Demo
 24/7 Customer Support
$42  $140
Testing Engine
CS0-004 Engine
 Desktop Based Application
 Last Update: Sep 9, 2026
 Question and Answers: 82
 Create Multiple Test Sets
 Questions Regularly Updated
  90 Days Free Updates
  Windows and Mac Compatible
$31.5  $105

Verified By IT Certified Experts

CertsTopics.com Certified Safe Files

Up-To-Date Exam Study Material

99.5% High Success Pass Rate

100% Accurate Answers

Instant Downloads

Exam Questions And Answers PDF

Try Demo Before You Buy

Certification Exams with Helpful Questions And Answers

CompTIA Cybersecurity Analyst CySA+ V4 (New Version) Questions and Answers

Question 1

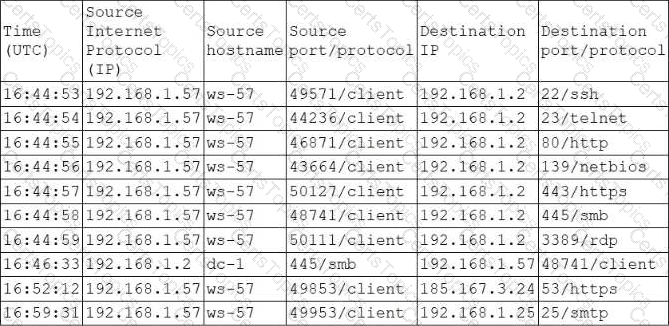
An analyst reviews the following log entries:

Which of the following conclusions should the analyst reach? (Choose two.)

Options:

A.

Host ws-57 is performing a network scan against dc-1.

B.

Domain Controller dc-1 is performing a network scan against ws-57.

C.

Host ws-57 delivered a phishing email via Simple Mail Transfer Protocol.

D.

Host ws-57 is communicating on a service using a non-standard port.

E.

Domain Controller dc-1 is infected with ransomware and initiating connections with ws-57.

F.

Domain Controller dc-1 is communicating using a non-standard port.

Buy Now
Question 2

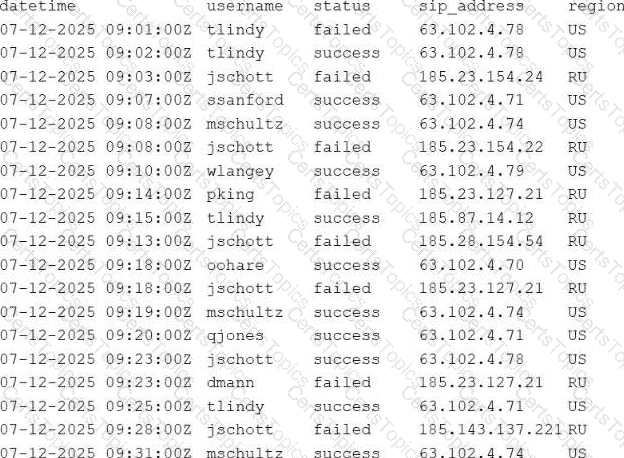
A security analyst analyzes the output of a web application access log for a company based in the United States.

Given the following output:

Which of the following users should be investigated first?

Options:

A.

jschott

B.

dmann

C.

mschultz

D.

tlindy

Question 3

A security analyst runs an Nmap scan against a host with multiple open ports using the following command:

nmap 10.10.10.1 -p-

The following output is obtained after the scan:

Starting Nmap 7.95 ( ) at 2025-07-15 15:55 UTC

Note: Host seems down.

Nmap done: 1 IP address (0 hosts up) scanned in 3.16 seconds

Which of the following is the most accurate way to scan the target IP for open ports?

Options:

A.

nmap 10.10.10.1 -p80, 443, 445, 9999, 135, 22, 21 -b --traceroute

B.

nmap -sn -p- 10.10.10.1

C.

nmap -p- -Pn 10.10.10.1

D.

nmap 10.10.10.1/24 -p- -R -O --script=ssl-enum-ciphers