
A security analyst runs an Nmap scan against a host with multiple open ports using the following command:
nmap 10.10.10.1 -p-
The following output is obtained after the scan:
Starting Nmap 7.95 ( ) at 2025-07-15 15:55 UTC
Note: Host seems down.
Nmap done: 1 IP address (0 hosts up) scanned in 3.16 seconds
Which of the following is the most accurate way to scan the target IP for open ports?
Which of the following best describes why operational technology (OT) devices use compensating controls?
Which of the following best explains why sensitive data should be encrypted at rest on laptops?
A security team deploys a new scanning solution that requires root, domain administrator, and local server administrator permissions on all systems.
Which of the following is the best way to help mitigate the risk for this level of access?
A cybersecurity analyst is reviewing static application security testing scan results and notices a finding for hard-coded credentials.
Which of the following should the analyst recommend to the application team to resolve this concern?
A vulnerability analyst conducts a security assessment on the Remote Desktop Protocol (RDP) security posture within the environment.
The analyst issues the following command for the assessment: nmap -p 3389 --script rdp* 10.0.0.0/24 The analyst receives responses, which are divided into one of the two categories, from 13 out of the 254 hosts:
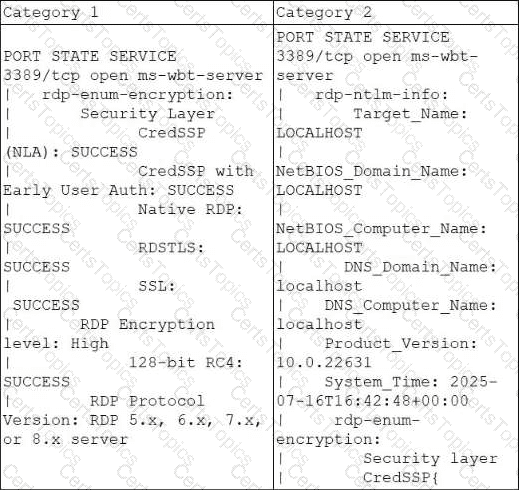
Which of the following conclusions can the analyst make about the output on Category 2?
Which of the following is the best reason to heavily segment business-critical assets from within the network?
A vendor releases details of a new vulnerability. When an analyst reviews the scheduled scans, no vulnerabilities are identified. The vulnerability is only discovered after a configuration change.
Which of the following scan types did the analyst configure?
A server was recently compromised. A security analyst needs to collect artifacts for further analysis before disconnecting the server from the network.
Which of the following artifacts should the analyst collect first?
Which of the following best describes a type of risk that exists after mitigations or controls are enacted and implemented?
The Chief Information Security Officer wants to improve internal security measures by continuously validating and verifying access to the production environment.
Which of the following concepts best describes this practice?
Before merging with a software company, the acquiring company's legal team requires a detailed software scan to determine if all code base is using open-source or paid licensed libraries. The vulnerability management analyst needs to provide this report.
Which of the following scan methods will best meet this requirement?
A security operations center (SOC) analyst investigates the results of a password spray test conducted by the vulnerability management team.
The analyst must:
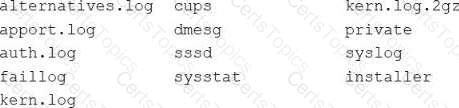
Identify Linux systems that have successful and unsuccessful logins with username "User1".
Create an output report named "linux-events" of all the events to a flat file.
The analyst issues the following console command:
ls /var/log/
The shortened output of the command is below:
Which of the following commands should the analyst use to meet the report output requirements?
Which of the following will inhibit remediation when attempting to resolve a vulnerability?
A security operations center (SOC) manager makes significant updates to the incident response plan and wants to test these updates with all stakeholders collaboratively.
Which of the following is the best way to accomplish this task?
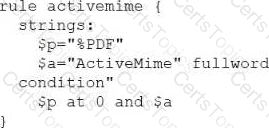
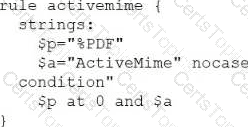
A security analyst must identify documents that contain encoded ActiveMime payloads in a directory containing thousands of files. The analyst runs the following command: grep -rail ActiveMime *
The command returns no output.
Which of the following Yet Another Recursive Acronym (YARA) rules should the analyst use to find the suspicious files?
A)
B)
C)
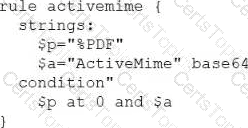
D)
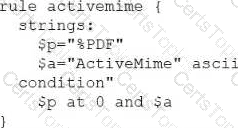
A security architect reviews a report from a third-party incident response consultant and observes the following:
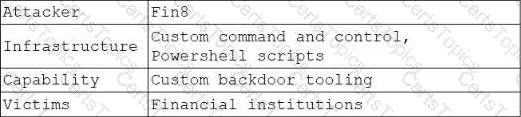
Which of the following frameworks did the consultant use to perform analysis?
An analyst reviews the following log entries:
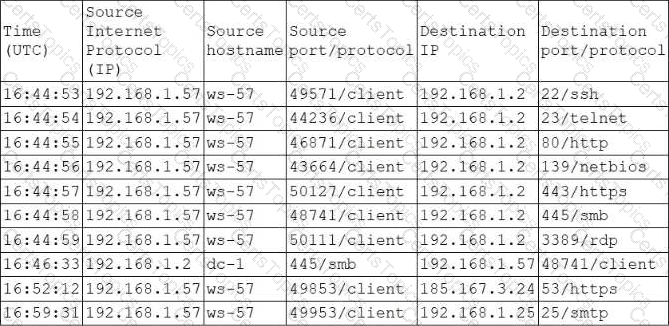
Which of the following conclusions should the analyst reach? (Choose two.)
A security analyst analyzes the output of a web application access log for a company based in the United States.
Given the following output:
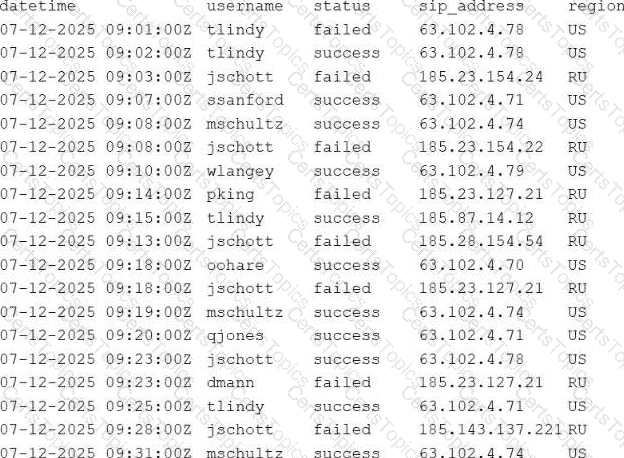
Which of the following users should be investigated first?
Which of the following describes the main benefits of MITRE ATT & CK Navigator?
A security analyst isolates a Windows 11 workstation from the network after known malware is detected. The list of security information and event management (SIEM) events during the malware installation and timeline does not identify a specific user who was logged in. The security analyst uses the local administrative account to log in and would like a list of logins to the machine.
Which of the following PowerShell commands should the analyst use?
An analyst must provide a visualization of data received from threat intelligence sources. The data includes the Internet Protocols, services, and tools used by threat actors.
Which of the following is the best framework for the analyst to follow to display this data?
Which of the following contains stakeholder contact information for incident response reporting?
Which of the following should a cybersecurity analyst utilize when a notification is inaccurate?
Copyright © 2021-2026 CertsTopics. All Rights Reserved
