
Weekend Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: big75certs

Cisco 200-901 Exam With Confidence Using Practice Dumps

Exam Code:
200-901
Exam Name:
Automating Networks Using Cisco Platforms
Certification:
Vendor:
Questions:
481
Last Updated:
Oct 3, 2026
Exam Status:
Stable
Cisco 200-901

200-901: CCNA Automation Exam 2025 Study Guide Pdf and Test Engine

Are you worried about passing the Cisco 200-901 (Automating Networks Using Cisco Platforms) exam? Download the most recent Cisco 200-901 braindumps with answers that are 100% real. After downloading the Cisco 200-901 exam dumps training , you can receive 99 days of free updates, making this website one of the best options to save additional money. In order to help you prepare for the Cisco 200-901 exam questions and verified answers by IT certified experts, CertsTopics has put together a complete collection of dumps questions and answers. To help you prepare and pass the Cisco 200-901 exam on your first attempt, we have compiled actual exam questions and their answers. 

Our (Automating Networks Using Cisco Platforms) Study Materials are designed to meet the needs of thousands of candidates globally. A free sample of the CompTIA 200-901 test is available at CertsTopics. Before purchasing it, you can also see the Cisco 200-901 practice exam demo.

Automating Networks Using Cisco Platforms Questions and Answers

Question 1

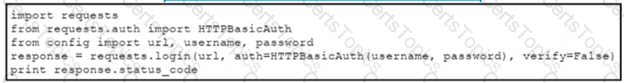
Refer to the exhibit.

The script returns an output of 401. To use the supplied URL. an HTTP GET request must Be sent with an Authorization header. The header value is a BaseG4 encoded concatenation of the username and password. Which action must be taken to return an output of 200?

Options:

A.

Change the verify=False setting in the request to verify=True to enable HTTP Basic authentication

B.

Modify the method from LOGIN to GET and supply the username ;password value as JSON payload

C.

Verify that the username and password values imported from the configuration file ate still valid.

D.

Insert an Authorization header with the values username password from the supplied configuration file.

Buy Now
Question 2

Which OWASP threat takes advantage of a web application that the user has already authenticated to execute an attack?

Options:

A.

phishing

B.

DoS

C.

brute force attack

D.

CSRF

Question 3

Which type of threat occur when an attacker can send hostile data to an interpreter within an application?

Options:

A.

Cross-site scripting

B.

Sensitive data exposure

C.

Broken authentication

D.

Injection