
Weekend Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: big75certs

Cisco 200-201 Exam With Confidence Using Practice Dumps

Exam Code:
200-201
Exam Name:
Understanding Cisco Cybersecurity Operations Fundamentals
Certification:
Vendor:
Questions:
476
Last Updated:
Nov 7, 2026
Exam Status:
Stable
Cisco 200-201

200-201: CCNA Cybersecurity Exam 2025 Study Guide Pdf and Test Engine

Are you worried about passing the Cisco 200-201 (Understanding Cisco Cybersecurity Operations Fundamentals) exam? Download the most recent Cisco 200-201 braindumps with answers that are 100% real. After downloading the Cisco 200-201 exam dumps training , you can receive 99 days of free updates, making this website one of the best options to save additional money. In order to help you prepare for the Cisco 200-201 exam questions and verified answers by IT certified experts, CertsTopics has put together a complete collection of dumps questions and answers. To help you prepare and pass the Cisco 200-201 exam on your first attempt, we have compiled actual exam questions and their answers. 

Our (Understanding Cisco Cybersecurity Operations Fundamentals) Study Materials are designed to meet the needs of thousands of candidates globally. A free sample of the CompTIA 200-201 test is available at CertsTopics. Before purchasing it, you can also see the Cisco 200-201 practice exam demo.

Understanding Cisco Cybersecurity Operations Fundamentals Questions and Answers

Question 1

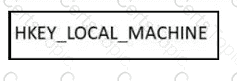
Refer to the exhibit.

Which component is identifiable in this exhibit?

Options:

A.

Trusted Root Certificate store on the local machine

B.

Windows PowerShell verb

C.

Windows Registry hive

D.

local service in the Windows Services Manager

Buy Now
Question 2

What does cyber attribution identify in an investigation?

Options:

A.

cause of an attack

B.

exploit of an attack

C.

vulnerabilities exploited

D.

threat actors of an attack

Question 3

An engineer runs a suspicious file in a sandbox analysis tool to see the outcome. The analysis report shows that outbound callouts were made post infection.

Which two pieces of information from the analysis report are needed to investigate the callouts? (Choose two.)

Options:

A.

signatures

B.

host IP addresses

C.

file size

D.

dropped files

E.

domain names