
Power Up Your Study Prep: Black Friday 75% Discount! Use coupon code below to save! - Ends in 0d 00h 00m 00s - Coupon code: big75certs

Amazon Web Services SCS-C03 Exam With Confidence Using Practice Dumps

Exam Code:
SCS-C03
Exam Name:
AWS Certified Security – Specialty
Certification:
Questions:
231
Last Updated:
Nov 11, 2026
Exam Status:
Stable
Amazon Web Services SCS-C03

SCS-C03: AWS Certified Specialty Exam 2025 Study Guide Pdf and Test Engine

Are you worried about passing the Amazon Web Services SCS-C03 (AWS Certified Security – Specialty) exam? Download the most recent Amazon Web Services SCS-C03 braindumps with answers that are 100% real. After downloading the Amazon Web Services SCS-C03 exam dumps training , you can receive 99 days of free updates, making this website one of the best options to save additional money. In order to help you prepare for the Amazon Web Services SCS-C03 exam questions and verified answers by IT certified experts, CertsTopics has put together a complete collection of dumps questions and answers. To help you prepare and pass the Amazon Web Services SCS-C03 exam on your first attempt, we have compiled actual exam questions and their answers. 

Our (AWS Certified Security – Specialty) Study Materials are designed to meet the needs of thousands of candidates globally. A free sample of the CompTIA SCS-C03 test is available at CertsTopics. Before purchasing it, you can also see the Amazon Web Services SCS-C03 practice exam demo.
AWS Certified Security – Specialty Questions and Answers

Question 1

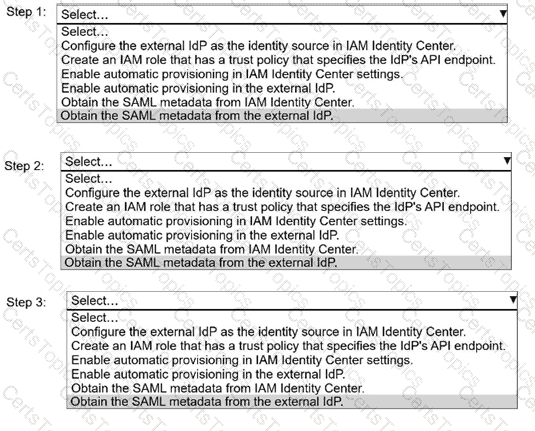
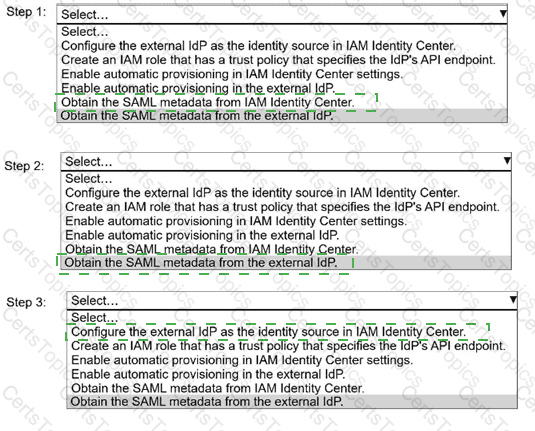
A security engineer needs to implement AWS IAM Identity Center with an external identity provider (IdP).

Select and order the correct steps from the following list to meet this requirement. Select each step one time or not at all. (Select and order THREE.)

. Configure the external IdP as the identity source in IAM Identity Center.

. Create an IAM role that has a trust policy that specifies the IdP ' s API endpoint.

. Enable automatic provisioning in IAM Identity Center settings.

. Enable automatic provisioning in the external IdP.

. Obtain the SAML metadata from IAM Identity Center.

. Obtain the SAML metadata from the external IdP.

Options:

Buy Now
Question 2

A company operates an Amazon EC2 instance that is registered as a target of a Network Load Balancer (NLB). The NLB is associated with a security group. The security group allows inbound TCP traffic on port 22 from 10.0.0.0/23.

The company maps the NLB to two subnets that share the same network ACL and route table. The route table has a route for 0.0.0.0/0 to an internet gateway. The network ACL has one inbound rule that has a priority of 20 and that allows TCP traffic on port 22 from 10.0.0.0/16.

A security engineer receives an alert that there is an unauthorized SSH session on the EC2 instance. The unauthorized session originates from 10.0.1.5. The company ' s incident response procedure requires unauthorized SSH sessions to beimmediately interrupted. The instance must remain running, and its memory must remain intact.

Which solution will meet these requirements?

Options:

A.

Restart the EC2 instance from either the AWS Management Console or the AWS CLI.

B.

Add a new inbound rule that has a priority of 10 to the network ACL to deny TCP traffic on port 22 from 10.0.1.5.

C.

Remove the security group rule that allows inbound TCP traffic on port 22 from 10.0.0.0/16.

D.

Update the route table to remove the route to the internet gateway.

Question 3

A company uses Amazon API Gateway to present REST APIs to users. An API developer wants to analyze API access patterns without the need to parse the log files.

Which combination of steps will meet these requirements with the LEAST effort? (Select TWO.)

Options:

A.

Configure access logging for the required API stage.

B.

Configure an AWS CloudTrail trail destination for API Gateway events. Configure filters on the userIdentity, userAgent, and sourceIPAddress fields.

C.

Configure an Amazon S3 destination for API Gateway logs. Run Amazon Athena queries to analyze API access information.

D.

Use Amazon CloudWatch Logs Insights to analyze API access information.

E.

Select the Enable Detailed CloudWatch Metrics option on the required API stage.
