
Pre-Winter Sale 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: save70

212-82 Exam Dumps : Certified Cybersecurity Technician (CCT)

PDF
212-82 pdf
 Real Exam Questions and Answer
 Last Update: Sep 14, 2026
 Question and Answers: 161 With Explanation
 Compatible with all Devices
 Printable Format
 100% Pass Guaranteed
$25.5  $84.99
212-82 exam
PDF + Testing Engine
212-82 PDF + engine
 Both PDF & Practice Software
 Last Update: Sep 14, 2026
 Question and Answers: 161
 Discount Offer
 Download Free Demo
 24/7 Customer Support
$40.5  $134.99
Testing Engine
212-82 Engine
 Desktop Based Application
 Last Update: Sep 14, 2026
 Question and Answers: 161
 Create Multiple Test Sets
 Questions Regularly Updated
  90 Days Free Updates
  Windows and Mac Compatible
$30  $99.99

Verified By IT Certified Experts

CertsTopics.com Certified Safe Files

Up-To-Date Exam Study Material

99.5% High Success Pass Rate

100% Accurate Answers

Instant Downloads

Exam Questions And Answers PDF

Try Demo Before You Buy

Certification Exams with Helpful Questions And Answers

Certified Cybersecurity Technician (CCT) Questions and Answers

Question 1

A major metropolitan municipal corporation had deployed an extensive loT network for managing various facilities in the city. A recent cyber attack has paralyzed the city’s vital services, bringing them to a complete halt. The Security Operations Center (SOC) has captured the network traffic during the attack and stored It as loT_capture.pcapng in the Documents folder of the Attacker Machine-1. Analyze the capture file and identify the command that was sent to the loT devices over the network. (Practical Question)

Options:

A.

Woodland_Blaze_ Warninggil

B.

Woodland_Blaze_Warning999

C.

Nature_Blaze_Warning555

D.

Forest_Fire_Alert444

Buy Now
Question 2

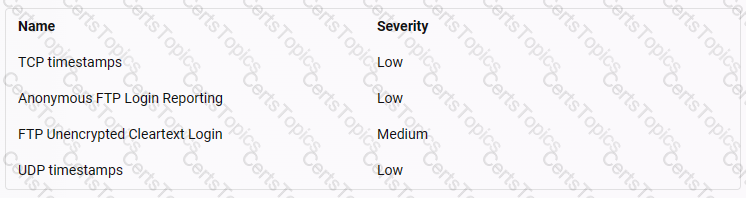
You are Harris working for a web development company. You have been assigned to perform a task for vulnerability assessment on the given IP address 20.20.10.26. Select the vulnerability that may affect the website according to the severity factor.

Hint: Greenbone web credentials: admin/password

Options:

A.

TCP timestamps

B.

Anonymous FTP Login Reporting

C.

FTP Unencrypted Cleartext Login

D.

UDP timestamps

Question 3

Mark, a security analyst, was tasked with performing threat hunting to detect imminent threats in an organization's network. He generated a hypothesis based on the observations in the initial step and started the threat-hunting process using existing data collected from DNS and proxy logs.

Identify the type of threat-hunting method employed by Mark in the above scenario.

Options:

A.

Entity-driven hunting

B.

TTP-driven hunting

C.

Data-driven hunting

D.

Hybrid hunting