(Full question statement start from here)
You enable Dynamic Host Configuration Protocol (DHCP) snooping on a VLAN and configure a FortiSwitch port astrustedfor DHCP snooping. What additional step is required to configure the port as trusted forDynamic ARP Inspection (DAI)? (Choose one answer)
Which two statements about the FortiLink authorization process are true? (Choose two.)
You need to mirror traffic from a source port on Switch A to a monitoring device on Switch C. For that purpose, you’re configuring Remote Switched Port Analyzer (RSPAN).1Due to the nature of RSPAN, what is the best practice when setting it up? (Choose one answer)
What happens when a routed VLAN interface (RVI) is configured on a FortiSwitch port or trunk? (Choose one answer)
Refer to the exhibit.
What two conclusions can be made regarding DHCP snooping configuration? (Choose two.)
When Dynamic Host Configuration Protocol (DHCP) snooping is enabled on a FortiSwitch VLAN, which two statements are true? (Choose two answers)
Refer to the exhibit.
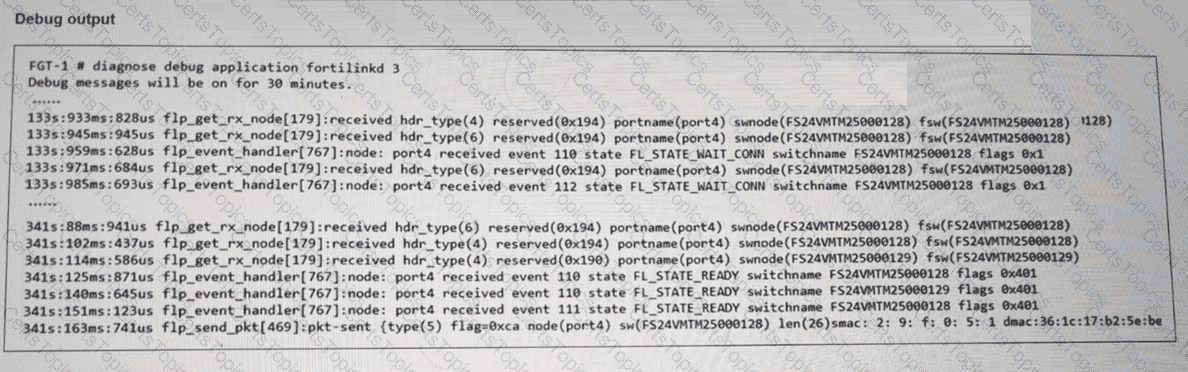
You have just authorized a new FortiSwitch on your FortiGate, and it appears online in the GUI. To verify that FortiLink connectivity is healthy, what should you check next? (Choose one answer)
Which packet capture method allows FortiSwitch to capture traffic on trunks and management interfaces?
Which two are valid traffic processing actions that a FortiSwitch access control list (ACL) can apply to matching traffic? (Choose two answers)
Exhibit.
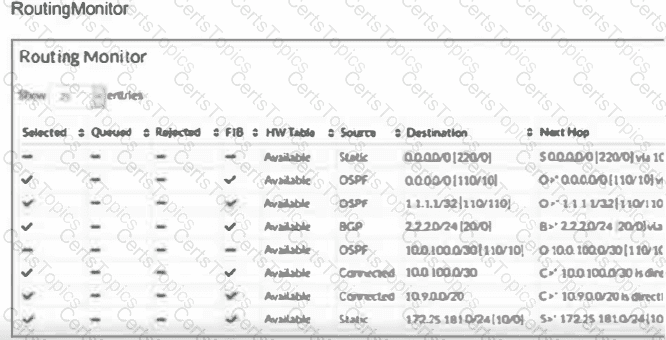
Two routes are not installed in the forwarding information base (FIB) as shown in the exnibit. Which two statements about these two route entries are true? (Choose two.)
Refer to the exhibit.
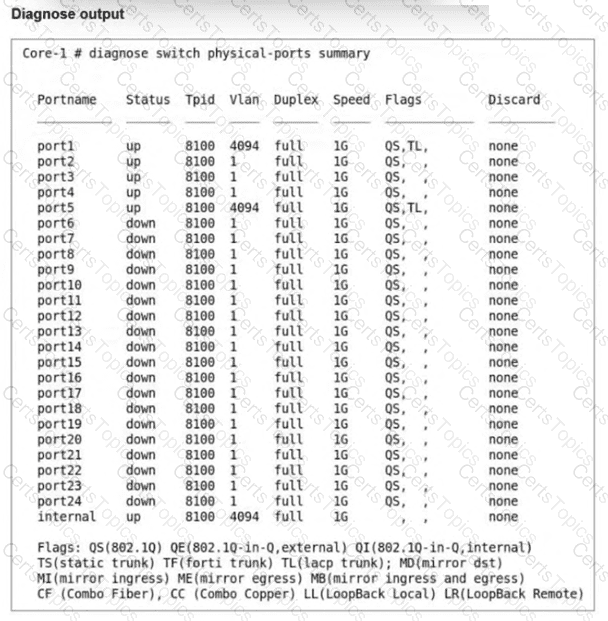
The command diagnose switch physical-ports summary is executed on FortiSwitch.
Based on the VLAN assignments shown in the output, what is the most likely management configuration of this FortiSwitch? (Choose one answer)
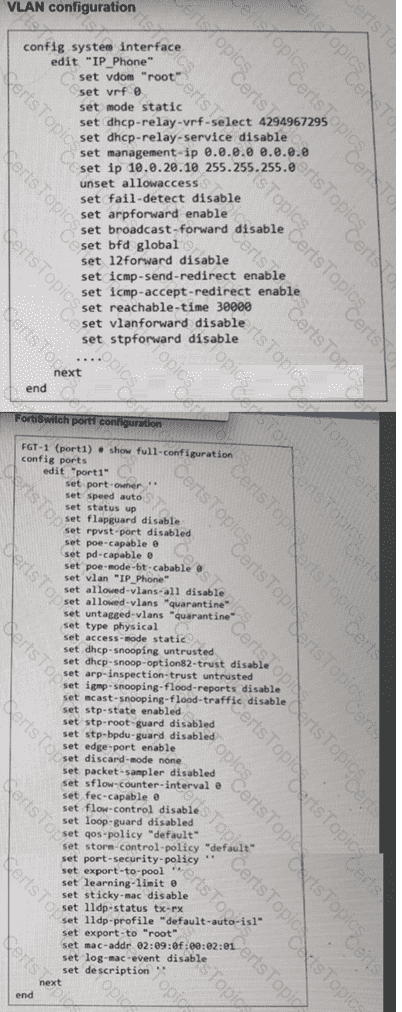
Refer to the exhibits. An IP phone is connected to port1 of FortiSwitch Access-1. The IP phone tags its traffic with VLAN ID 20. On FortiGate, VLAN IP_Phone (VLAN ID 20) has been configured, and port1 of Access-1 is set with VLAN 20 as the native VLAN. However, the IP phone cannot reach the network. The exhibit shows the partial VLAN configuration and the port1 configuration on Access-1.
Which configuration change must you make on FortiSwitch to allow ingress and egress traffic for the IP phone? (Choose one answer)
Refer to the exhibit.
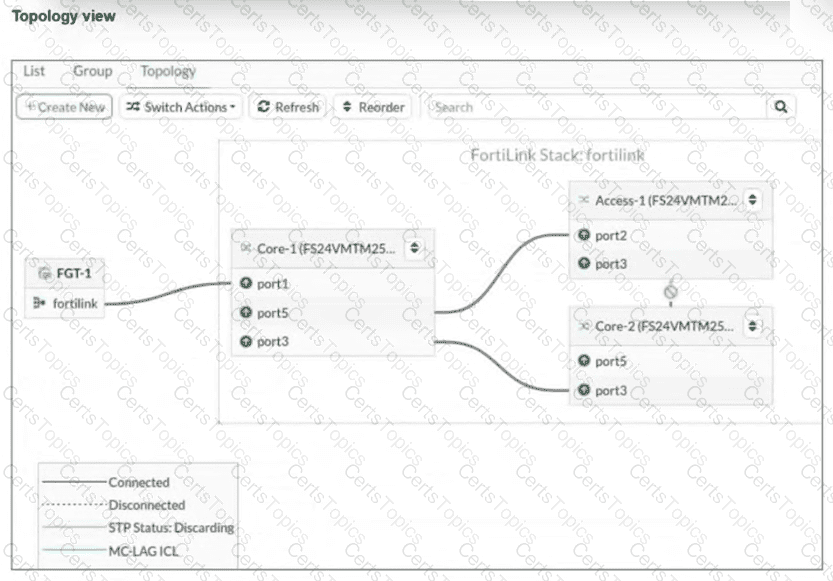
You just connected three FortiSwitch devices:Core-1,Core-2, andAccess-1. Core-1 and Core-2 both connect to Access-1 for redundancy. All switches are managed by FortiGate, which uses port4 as the FortiLink interface. After you enable the uplink ports on Core-2, you notice that port3 on Access-1 enters the Discarding STP state. What is the most likely cause of this behavior? (Choose one answer)
Refer to the exhibit.
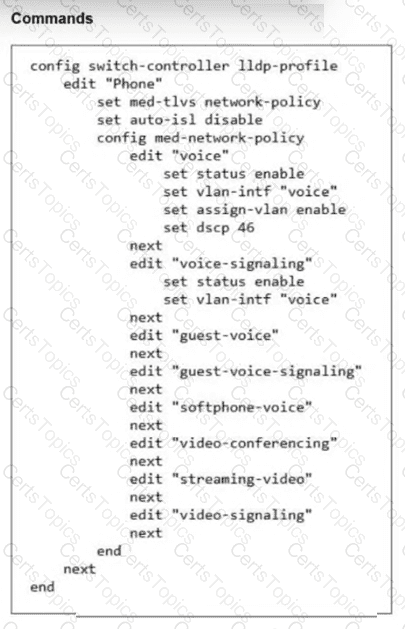
The LLDP profile shown in the exhibit was configured to detect IP phones and automatically assign them to the appropriate VLAN. You apply this LLDP profile on a FortiSwitch port. Which configuration should you enable on the FortiSwitch profile to collect detailed information about all the connected IP phones? (Choose one answer)
What feature can network administrators use to segment network operations and the administration of managed FortiSwitch devices on FortiGate?
Refer to the exhibit.
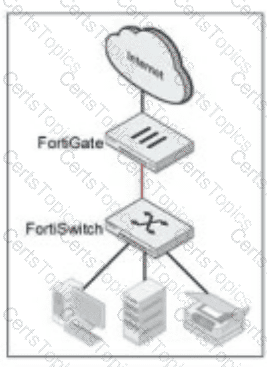
Which two configurations can you use for the FortiLink interface in a basic single FortiGate-single FortiSwitch topology? (Choose two.)
Which two statements about 802.1X authentication on FortiSwitch ports are true? (Choose two.)
Which drop policy mode, if assigned to a congested port, will drop incoming packets until there is no congestion on the egress port?
You are managing FortiSwitch ports from a FortiGate device with multiple VDOMs. Which two methods can you use to assign FortiSwitch ports to VDOMs? (Choose two answers)
Refer to the exhibit.
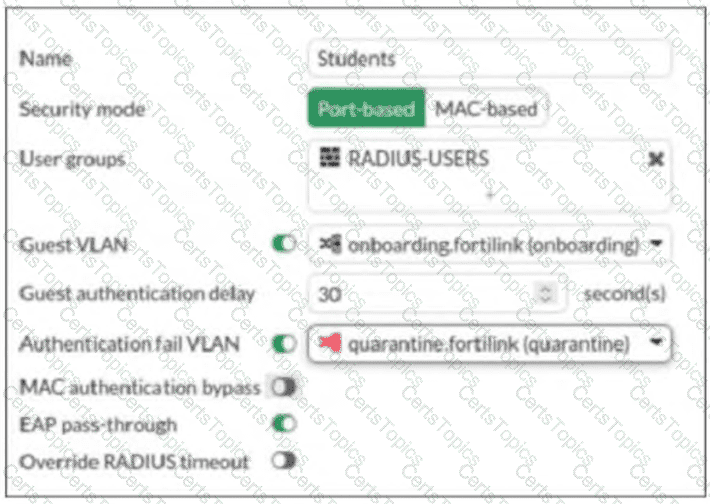
The security port policy is configured as shown in the exhibit. Which behavior occurs if a device connected to the port that does not support 802.1X? (Choose one answer)
(Full question statement start from here)
What is one key advantage of using a sniffer profile on FortiSwitch compared to using the sniffer command? (Choose one answer)
Which two types of Layer 3 interfaces can participate in dynamic routing on FortiSwitch? (Choose two.)
Which statement about using MAC, IP, and protocol-based VLANs on FortiSwitch is true?
Refer to the exhibit.
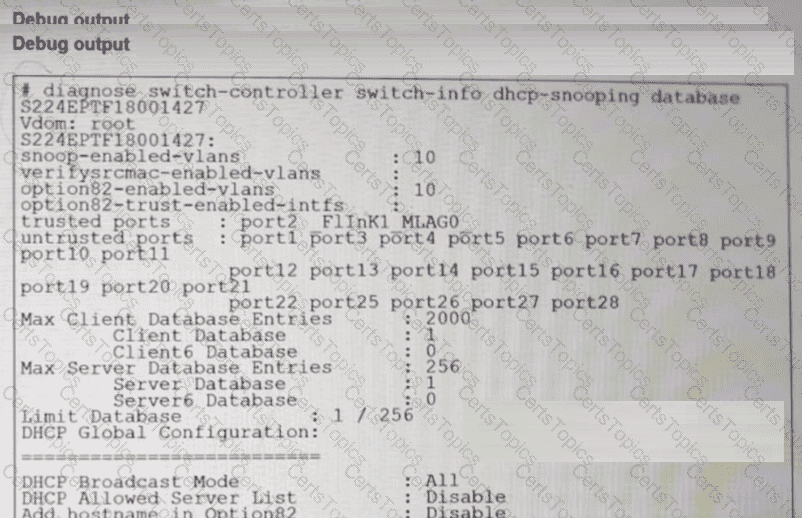
After reviewing the CLI command output, which two conclusions can you make about the Dynamic Host Configuration Protocol (DHCP) snooping configuration? (Choose two answers)
Refer to the exhibits.
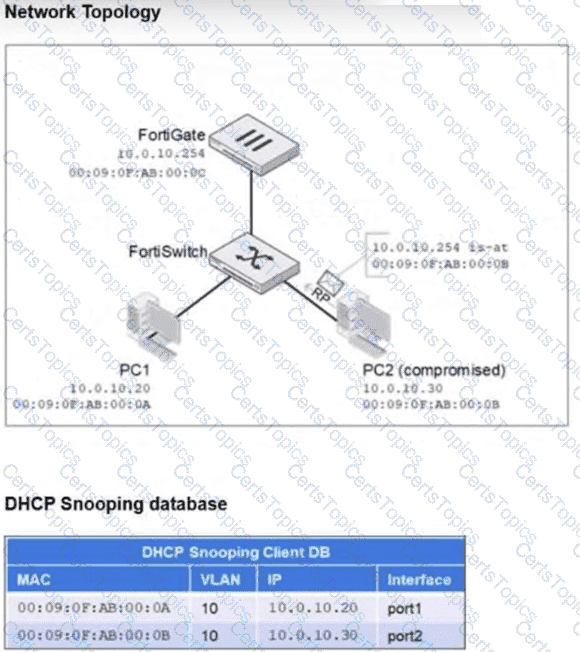
All three FortiSwitch-connected ports are configured in VLAN 10. FortiGate acts as the Dynamic Host Configuration Protocol (DHCP) server and is connected to a DHCP snooping trusted trunk port. PC1 and PC2 are connected to ports configured as untrusted for Dynamic ARP Inspection (DAI), and no static bindings are configured in the IP source guard (IPSG) database. PC2 is compromised and attempts to spoof the FortiGate IP address by sending forged Address Resolution Protocol (ARP) replies with its own MAC address. What will FortiSwitch do with the ARP packets from PC2? (Choose one answer)
Refer to the exhibit.
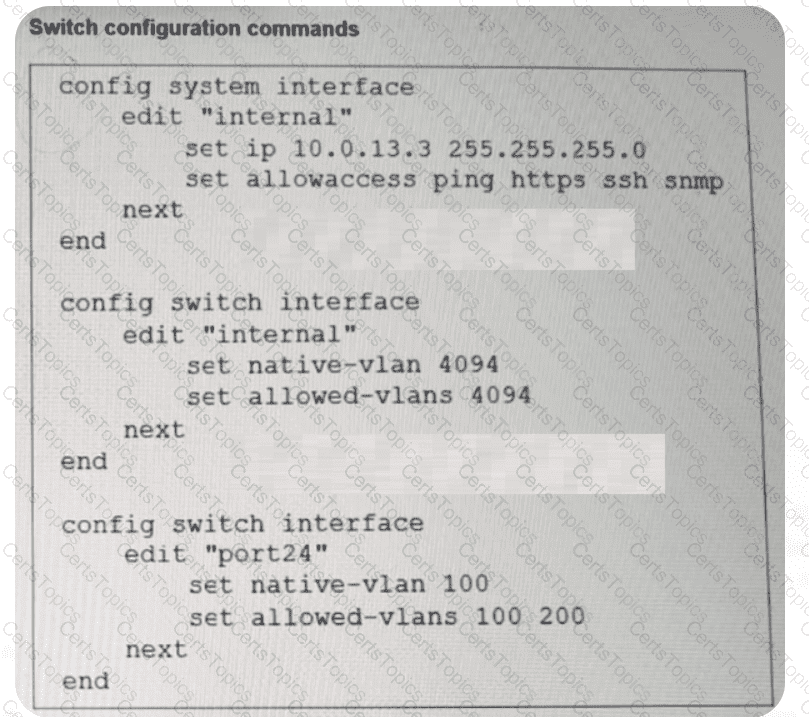
Port24 is the only uplink port connected to the network where you need access to FortiSwitch management services. However, FortiSwitch is not accessible on its management interface with IP address 10.0.13.3. Based on the configuration shown in the exhibit, which two actions should you take to fix the issue and access FortiSwitch? (Choose two answers)
(Full question statement start from here)
You are deploying a FortiSwitch virtual stack in a network that contains Cisco devices. You want the Cisco devices toautomatically discover the FortiSwitch devices and exchange device information. Which two protocols must be enabled on the FortiSwitch devices to achieve this? (Choose two answers)
Refer to the exhibit.
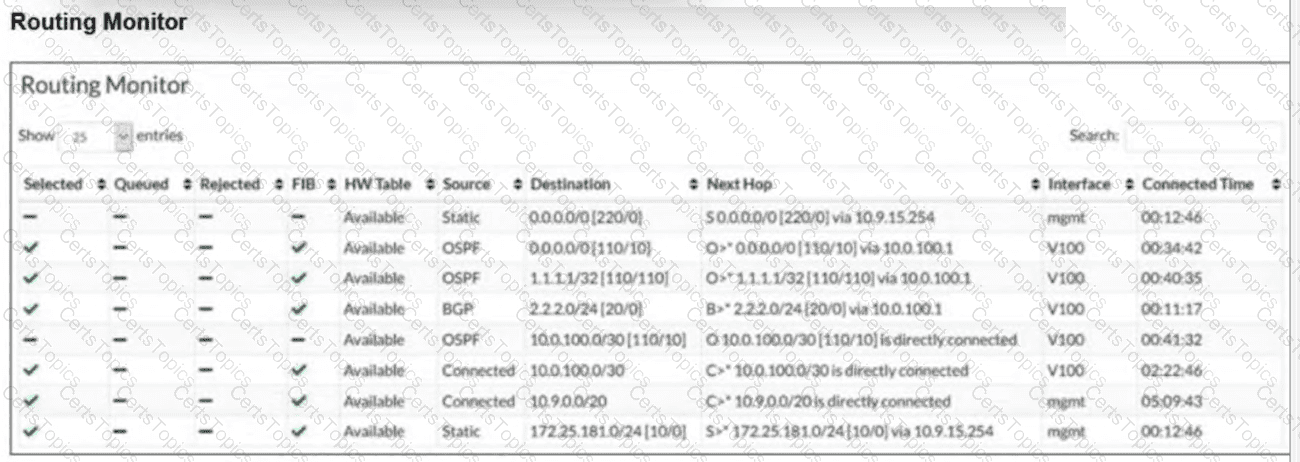
and an OSPF route with destination 0.0.0.0/0 [110/10]. The OSPF route is marked with a checkmark in the FIB column, while the Static route has a dash.]
The routing monitor displays multiple route entries, but only some are installed in the forwarding information base (FIB). After analyzing the two route entries with the destination 0.0.0.0/0, which statement correctly describe why one of these routes is not installed in the FIB? (Choose one answer)
Which LLDP-MED Type-Length-Values does FortiSwitch collect from endpoints to track network devices and determine their characteristics?
Which two requirements must be met before FortiGate can manage a FortiSwitch stack? (Choose two answers)
Which statement about 802.1X security profiles using MAC-based authentication mode is true?
On supported FortiSwitch models, which access control list (ACL) stage is recommended for applying actions before the switch performs any layer 2 or layer 3 processing? (Choose one answer)
Exhibit.
The exhibit shows the current status of the ports on the managed FortiSwitch.
Access-1.
Why would FortiGate display a serial number in the Native VLAN column associated with the port23 entry?
Refer to the exhibit.
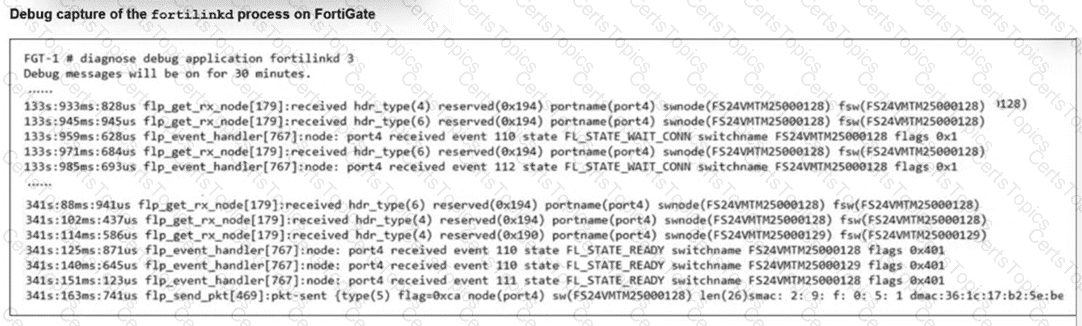
A periodic heartbeat message sent from a managed FortiSwitch and corresponding acknowledgments from FortiGate is shown. What does this behavior indicate? (Choose one answer)
Copyright © 2021-2026 CertsTopics. All Rights Reserved