Halloween Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: big75certs

New Release NSE5_FSW_AD-7.6 Fortinet Network Security Expert Questions

Fortinet NSE 5 - FortiSwitch 7.6 Administrator Questions and Answers

Question 5

Refer to the exhibit.

What two conclusions can be made regarding DHCP snooping configuration? (Choose two.)

Options:

A.

Maximum value to accept clients DHCP request is configured as per DHCP server range.

B.

FortiSwitch is configured to trust DHCP replies coming on FortiLink interface.

C.

DHCP clients that are trusted by DHCP snooping configured is only one.

D.

Global configuration for DHCP snooping is set to forward DHCP client requests on all ports in the VLAN.

Question 6

When Dynamic Host Configuration Protocol (DHCP) snooping is enabled on a FortiSwitch VLAN, which two statements are true? (Choose two answers)

Options:

A.

DHCP replies are accepted only on trusted ports.

B.

DHCP snooping blocks all unicast traffic.

C.

Option 82 can be inserted into DHCP requests.

D.

DHCP requests are dropped if sent from trusted ports.

Question 7

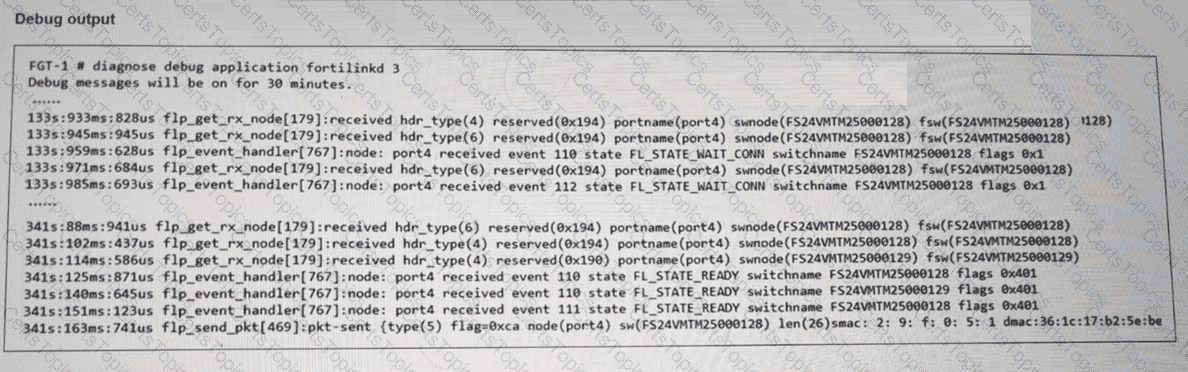
Refer to the exhibit.

You have just authorized a new FortiSwitch on your FortiGate, and it appears online in the GUI. To verify that FortiLink connectivity is healthy, what should you check next? (Choose one answer)

Options:

A.

Check that the switch automatically disables all unused ports.

B.

Look for FortiLink heartbeat messages sent from FortiSwitch to FortiGate every few seconds and confirm FortiGate acknowledges them.

C.

Verify that FortiGate has pushed a new firmware image to FortiSwitch immediately.

D.

Ensure the FortiSwitch is automatically sending log events to FortiAnalyzer.

Question 8

Which packet capture method allows FortiSwitch to capture traffic on trunks and management interfaces?

Options:

A.

SPAN

B.

Sniffer profile

C.

sFlow

D.

TCP dump