Halloween Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: big75certs

Fortinet NSE5_FSW_AD-7.6 Online Access

Fortinet NSE 5 - FortiSwitch 7.6 Administrator Questions and Answers

Question 17

Which two statements about 802.1X authentication on FortiSwitch ports are true? (Choose two.)

Options:

A.

All hosts behind an authenticated port are allowed access after a successful authentication.

B.

A security policy is used to apply 802.1 authentication on a port.

C.

A local user database must be used to authenticate devices using the 802.1X authentication protocol.

D.

All devices connecting to FortiSwitch must support 802.1X authentication.

Question 18

Which drop policy mode, if assigned to a congested port, will drop incoming packets until there is no congestion on the egress port?

Options:

A.

Tail-drop mode

B.

Weighted round robin mode.

C.

Random early detection mode

D.

Strict mode

Question 19

You are managing FortiSwitch ports from a FortiGate device with multiple VDOMs. Which two methods can you use to assign FortiSwitch ports to VDOMs? (Choose two answers)

Options:

A.

Assigning the port directly to a specific VDOM for dedicated physical isolation

B.

Use FortiGate policies to control inter-VDOM traffic for FortiSwitch ports

C.

Use interface role mapping to dynamically assign FortiSwitch ports to VDOMs based on Dynamic Host Configuration Protocol (DHCP) scope

D.

Using a virtual port pool (VPP) to create virtualized ports that can be assigned to different VDOMs

Question 20

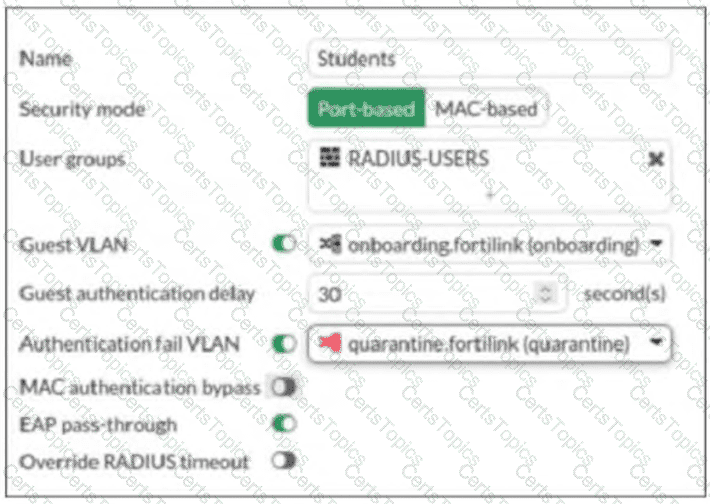
Refer to the exhibit.

The security port policy is configured as shown in the exhibit. Which behavior occurs if a device connected to the port that does not support 802.1X? (Choose one answer)

Options:

A.

The device is blocked from accessing the network.

B.

The device is placed into the onboarding VLAN.

C.

The device is placed into the quarantine VLAN.

D.

The device is assigned to the default management VLAN.