
Which two are valid traffic processing actions that a FortiSwitch access control list (ACL) can apply to matching traffic? (Choose two answers)
Exhibit.
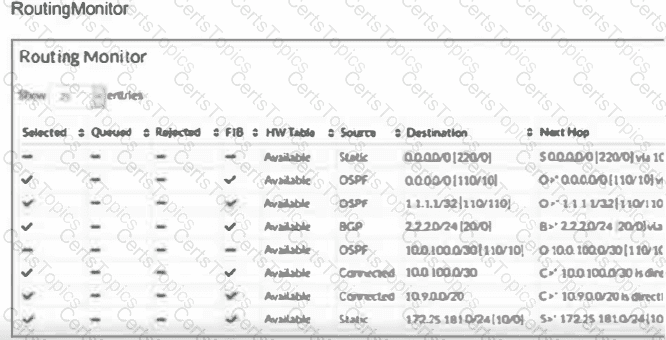
Two routes are not installed in the forwarding information base (FIB) as shown in the exnibit. Which two statements about these two route entries are true? (Choose two.)
Refer to the exhibit.
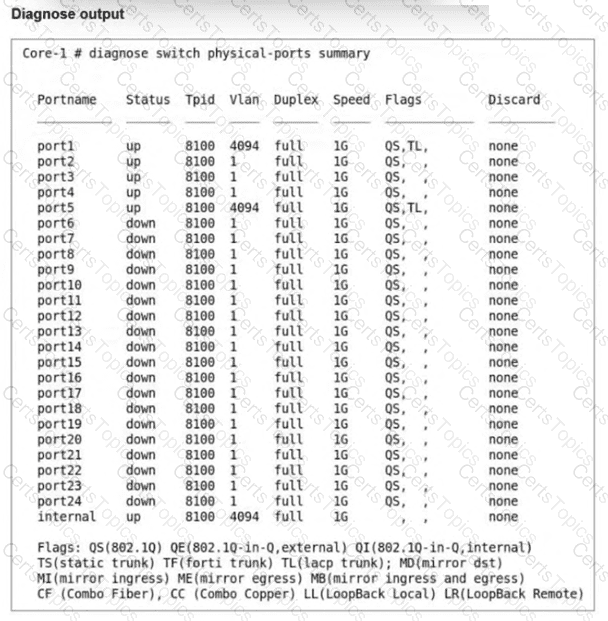
The command diagnose switch physical-ports summary is executed on FortiSwitch.
Based on the VLAN assignments shown in the output, what is the most likely management configuration of this FortiSwitch? (Choose one answer)
Refer to the exhibits. An IP phone is connected to port1 of FortiSwitch Access-1. The IP phone tags its traffic with VLAN ID 20. On FortiGate, VLAN IP_Phone (VLAN ID 20) has been configured, and port1 of Access-1 is set with VLAN 20 as the native VLAN. However, the IP phone cannot reach the network. The exhibit shows the partial VLAN configuration and the port1 configuration on Access-1.
Which configuration change must you make on FortiSwitch to allow ingress and egress traffic for the IP phone? (Choose one answer)
Copyright © 2021-2026 CertsTopics. All Rights Reserved
