Halloween Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: big75certs

Note! Following FCSS_EFW_AD-7.4 Exam is Retired now. Please select the alternative replacement for your Exam Certification. The new exam code is FCSS_EFW_AD-7.6

Verified By IT Certified Experts

CertsTopics.com Certified Safe Files

Up-To-Date Exam Study Material

99.5% High Success Pass Rate

100% Accurate Answers

Instant Downloads

Exam Questions And Answers PDF

Try Demo Before You Buy

Certification Exams with Helpful Questions And Answers

FCSS - Enterprise Firewall 7.4 Administrator Questions and Answers

Question 1

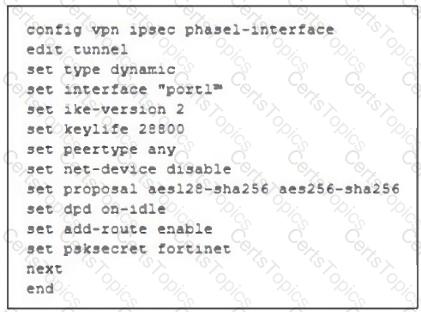
Refer to the exhibit, which contains a partial VPN configuration.

What can you conclude from this VPN IPsec phase 1 configuration?

Options:

A.

This configuration is the best for networks with regular traffic intervals, providing a balance between connectivity assurance and resource utilization.

B.

Peer IDs are unencrypted and exposed, creating a security risk.

C.

FortiGate will not add a route to its routing or forwarding information base when the dynamic tunnel is negotiated.

D.

A separate interface is created for each dial-up tunnel, which can be slower and more resource intensive, especially in large networks.

Buy Now
Question 2

A company that acquired multiple branches across different countries needs to install new FortiGate devices on each of those branches. However, the IT staff lacks sufficient knowledge to implement the initial configuration on the FortiGate devices.

Which three approaches can the company take to successfully deploy advanced initial configurations on remote branches? (Choose three.)

Options:

A.

Use metadata variables to dynamically assign values according to each FortiGate device.

B.

Use provisioning templates and install configuration settings at the device layer.

C.

Use the Global ADOM to deploy global object configurations to each FortiGate device.

D.

Apply Jinja in the FortiManager scripts for large-scale and advanced deployments.

E.

Add FortiGate devices on FortiManager as model devices, and use ZTP or LTP to connect to FortiGate devices.

Question 3

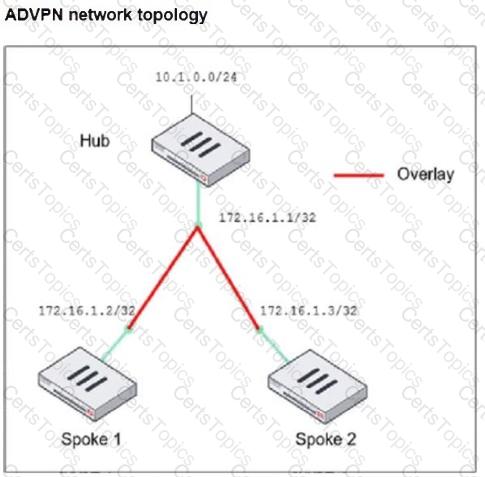
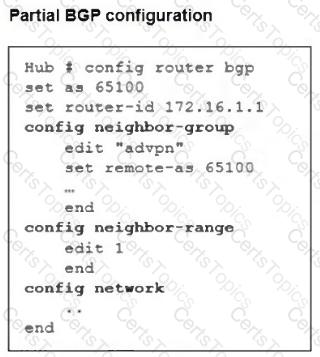
Refer to the exhibit, which shows the ADVPN network topology and partial BGP configuration.

Which two parameters must an administrator configure in the config neighbor range for spokes shown in the exhibit? (Choose two.)

Options:

A.

set max-neighbor-num 2

B.

set neighbor-group advpn

C.

set route-reflector-client enable

D.

set prefix 172.16.1.0 255.255.255.0