
Halloween Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: big75certs

MuleSoft MCIA-Level-1 Exam With Confidence Using Practice Dumps

Exam Code:
MCIA-Level-1
Exam Name:
MuleSoft Certified Integration Architect - Level 1
Vendor:
Questions:
273
Last Updated:
Oct 29, 2026
Exam Status:
Stable
MuleSoft MCIA-Level-1

MCIA-Level-1: MuleSoft Certified Architect Exam 2025 Study Guide Pdf and Test Engine

Are you worried about passing the MuleSoft MCIA-Level-1 (MuleSoft Certified Integration Architect - Level 1) exam? Download the most recent MuleSoft MCIA-Level-1 braindumps with answers that are 100% real. After downloading the MuleSoft MCIA-Level-1 exam dumps training , you can receive 99 days of free updates, making this website one of the best options to save additional money. In order to help you prepare for the MuleSoft MCIA-Level-1 exam questions and verified answers by IT certified experts, CertsTopics has put together a complete collection of dumps questions and answers. To help you prepare and pass the MuleSoft MCIA-Level-1 exam on your first attempt, we have compiled actual exam questions and their answers. 

Our (MuleSoft Certified Integration Architect - Level 1) Study Materials are designed to meet the needs of thousands of candidates globally. A free sample of the CompTIA MCIA-Level-1 test is available at CertsTopics. Before purchasing it, you can also see the MuleSoft MCIA-Level-1 practice exam demo.
MuleSoft Certified Integration Architect - Level 1 Questions and Answers

Question 1

An organization has several APIs that accept JSON data over HTTP POST. The APIs are all publicly available and are associated with several mobile applications and web applications. The organization does NOT want to use any authentication or compliance policies for these APIs, but at the same time, is worried that some bad actor could send payloads that could somehow compromise the applications or servers running the API implementations. What out-of-the-box Anypoint Platform policy can address exposure to this threat?

Options:

A.

Apply a Header injection and removal policy that detects the malicious data before it is used

B.

Apply an IP blacklist policy to all APIs; the blacklist will Include all bad actors

C.

Shut out bad actors by using HTTPS mutual authentication for all API invocations

D.

Apply a JSON threat protection policy to all APIs to detect potential threat vectors

Buy Now
Question 2

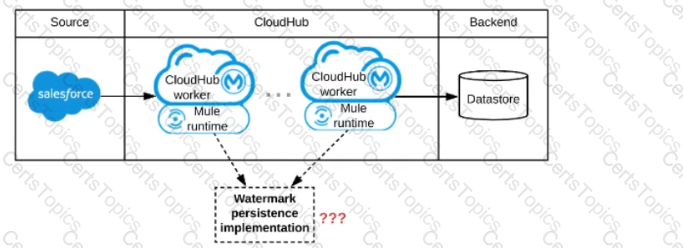
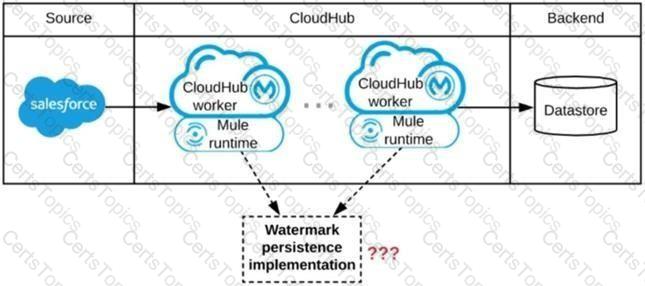
Refer to the exhibit.

A Mule application is being designed to be deployed to several CIoudHub workers. The Mule application's integration logic is to replicate changed Accounts from Satesforce to a backend system every 5 minutes.

A watermark will be used to only retrieve those Satesforce Accounts that have been modified since the last time the integration logic ran.

What is the most appropriate way to implement persistence for the watermark in order to support the required data replication integration logic?

Options:

A.

Persistent Anypoint MQ Queue

B.

Persistent Object Store

C.

Persistent Cache Scope

D.

Persistent VM Queue

Question 3

As a part of project requirement, Java Invoke static connector in a mule 4 application needs to invoke a static method in a dependency jar file. What are two ways to add the dependency to be visible by the connectors class loader?

(Choose two answers)

Options:

A.

In the Java Invoke static connector configuration, configure a path and name of the dependency jar file

B.

Add the dependency jar file to the java classpath by setting the JVM parameters

C.

Use Maven command to include the dependency jar file when packaging the application

D.

Configure the dependency as a shared library in the project POM

E.

Update mule-artefact.json to export the Java package
