
When using SOAR to automate a response with a zero trust approach, which of the following represents a valid order of operations?
A detection engineer is using a threat defense informed strategy to define use cases. Which Splunk app would best facilitate their use case development process by cross referencing detections with the MITRE ATT & CK Framework?
The SOC manager has a desire to measure mean time to acknowledge finding (notable event) in order to meet a desired service-level objective. Which two fields can be used to measure the difference?
Which fields are used to determine asset priority, when priority is assigned through an asset and identity lookup?
In a contextualization playbook, a URL is transmitted to a sandbox for examination and disposition recommendation. What underlying HTTP method is used to transmit this data to the sandbox?
When developing security metrics, why would a Key Performance Indicator (KPI) that focuses on total perimeter firewall blocks be an ineffective metric?
How can an engineer verify if results will return for a potential detection based on historical events within the organization?
How does Mission Control decipher which response template to assign to findings?
An automation engineer for the Wonderland SOC has configured a new asset and is getting an HTTP 403 response code. Which of the following is a possible cause of the error code?
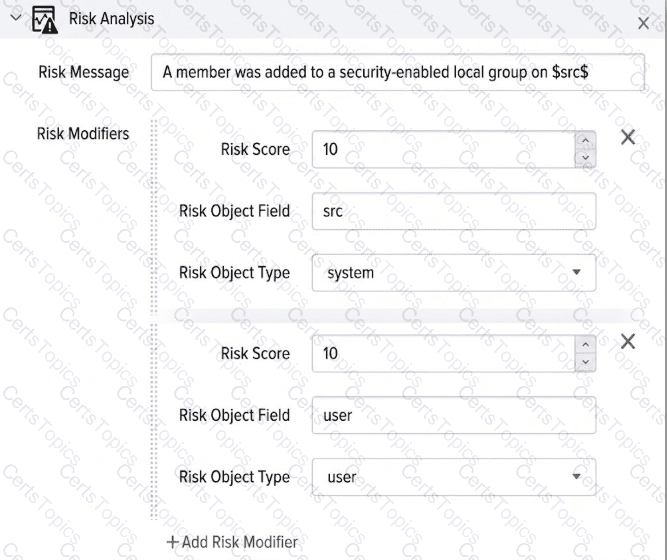
Based on this example image, if it is detected that a member has been added to a security-enabled local group, how many risk events will be created?
Which Splunk feature makes SPL searches shorter and reusable by inserting it into search strings?
Consider the following series of events:
4:00 GMT Detection runs for interval 3:30–4:00
4:30 GMT Detection runs for interval 4:00–4:30
4:35 GMT Event 1 occurs on an endpoint
4:45 GMT Event 1 is indexed
5:00 GMT Detection runs for interval 4:30–5:00
5:05 GMT Event 1 finding is added to ES with timestamp 4:35
5:24 GMT Event 2 occurs on an endpoint
5:30 GMT Detection runs for interval 5:00–5:30
5:35 GMT Event 2 is indexed
6:00 GMT Detection runs for interval 5:30–6:00
What is the problem with the detection schedule chosen and how can it be solved?
MITRE D3FEND is designed to compliment MITRE ' s list of adversarial tactics, techniques, and common knowledge (ATT & CK). Which tactics are associated with MITRE D3FEND in order to detect, deny, and disrupt adversarial efforts?
What is the primary purpose of data indexing in Splunk?
Which field in the risk index is used to describe the activity within a finding?
For detections that leverage a CIM data model, which aspect of the configuration is responsible for determining which indexes are being searched?
When creating a new playbook to be called directly from Mission Control or Enterprise Security, which type of playbook must be used?
When creating a case in Splunk SOAR, which action should be taken to correlate various findings (risk notables) to ensure all are actioned?
When developing security metrics, why would a Key Performance Indicator (KPI) that focuses on total perimeter firewall blocks be an ineffective metric?
Which action improves the effectiveness of notable events in Enterprise Security?
Once an engineer has determined that a new detection will fire, what is the next priority for that detection?
What document can be helpful in understanding the prioritization of risk when comparing entities in an organization?
Which search command was used to generate the result in the image below?
Which Splunk Enterprise Security add-on facilitates the ingestion of Threat Intelligence data?
Which stats event field created by an adaptive response action allows for troubleshooting the correlation search that created the notable event?
There are multiple methods for communicating data with a REST endpoint. In the URL shown, what is the name of the key-value pairs represented after the question mark in the URL?
In the context of Splunk ' s Common Information Model (CIM), which construct ensures that events from different data sources appear in the applicable data model?
An engineer receives a report that the “Traffic over time by action” dashboard is not populating. It has been confirmed that the relevant logs are being ingested properly and they are CIM compliant. What other configuration may be missing?
Which of the following is the most efficient search to return a list of all visible indexes and the sourcetypes contained within them?
When building detections using the Authentication Data Model, which values are recommended for use against the action field?
What field is used by default to direct data into CIM data model datasets?
Copyright © 2021-2026 CertsTopics. All Rights Reserved
