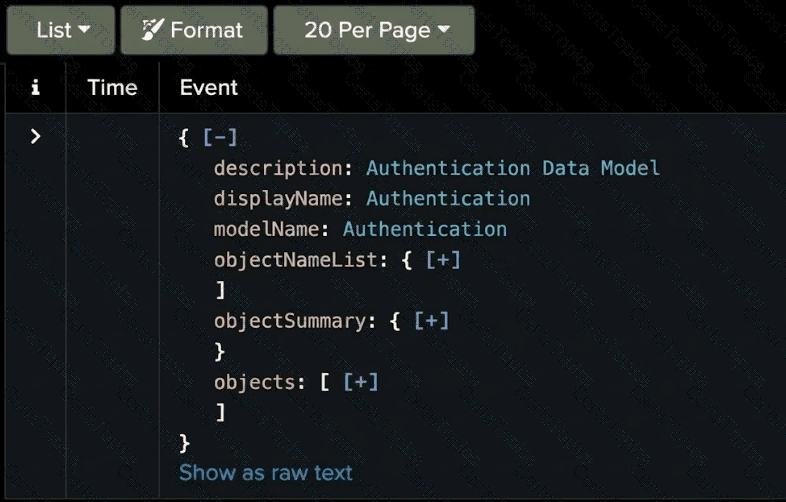
The command is datamodel . The exhibit shows structured information describing the Authentication Data Model , including fields such as description, displayName, modelName, objectNameList, objectSummary, and objects. This type of output is characteristic of the Splunk datamodel search command, which can return metadata and structural information about configured data models.
A representative search is:
| datamodel Authentication
The command allows engineers to inspect data-model definitions and understand the objects or datasets that compose a model. This is particularly useful when validating CIM-related configuration, determining available datasets, and developing searches that rely on normalized data.
The metadata command instead returns indexed metadata concerning hosts, sources, or sourcetypes and would not produce the data-model definition structure visible in the exhibit. datatype is not the appropriate Splunk search command for inspecting data-model definitions, and cim is not the command represented by this output.
The visible values description: Authentication Data Model, displayName: Authentication, and modelName: Authentication are the strongest indicators that the command queried a Splunk data model.
Study Guide topics: Data Models, Common Information Model (CIM), datamodel command, Authentication Data Model, dataset inspection, normalized security data.