
An automation engineer for the Wonderland SOC has configured a new asset and is getting an HTTP 403 response code. Which of the following is a possible cause of the error code?
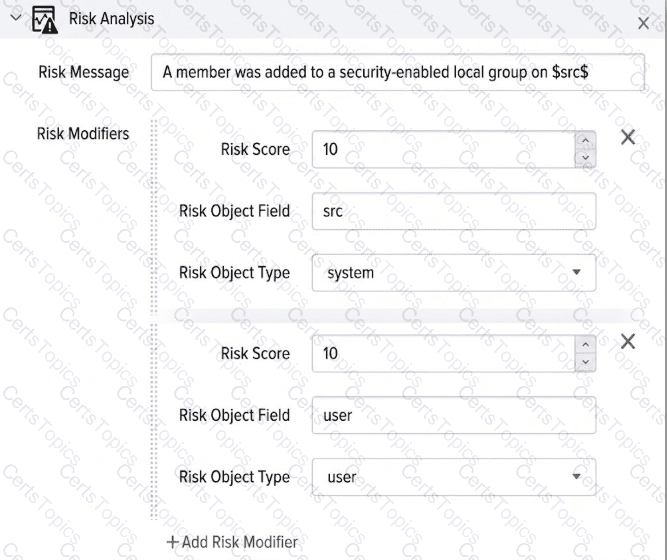
Based on this example image, if it is detected that a member has been added to a security-enabled local group, how many risk events will be created?
Which Splunk feature makes SPL searches shorter and reusable by inserting it into search strings?
Consider the following series of events:
4:00 GMT Detection runs for interval 3:30–4:00
4:30 GMT Detection runs for interval 4:00–4:30
4:35 GMT Event 1 occurs on an endpoint
4:45 GMT Event 1 is indexed
5:00 GMT Detection runs for interval 4:30–5:00
5:05 GMT Event 1 finding is added to ES with timestamp 4:35
5:24 GMT Event 2 occurs on an endpoint
5:30 GMT Detection runs for interval 5:00–5:30
5:35 GMT Event 2 is indexed
6:00 GMT Detection runs for interval 5:30–6:00
What is the problem with the detection schedule chosen and how can it be solved?
Copyright © 2021-2026 CertsTopics. All Rights Reserved
