You have a Microsoft Sentinel workspace named Workspace1
You have 100 on-premises servers that run Linux and have the Azure Monitor Agent installed.
You need to collect Syslog events from the Linux servers. The solution must meet the following requirements:
•Ensure that filtering occurs before data is written to Workspace1
•Reduce ingestion costs by excluding low value Syslog messages.
What should you include in the solution?
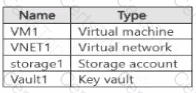
You have an Azure subscription that contains the resources shown in the following table.
You plan to use Microsoft Defender for Cloud.
Which resources can be protected by using Microsoft Defender for Cloud?
HOTSPOT
You have an Azure subscription that contains the following virtual machines:
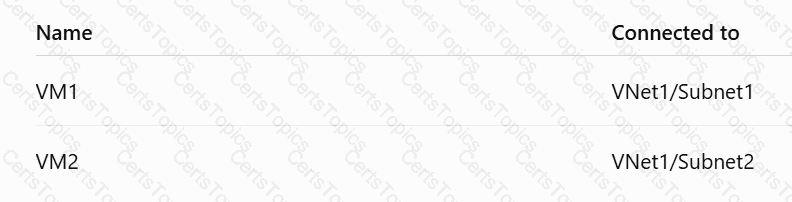
Subnet1 and Subnet2 have associated network security groups (NSGs). The NSGs contain an outbound rule with the following configuration:
Port: Any
Source: Any
Priority: 100
Action: Deny
Protocol: Any
Destination: Storage
The subscription contains a storage account named storage1.
You create a private endpoint named Private1 with the following settings:
Resource type: Microsoft.Storage/storageAccounts
Resource: storage1
Target sub-resource: blob
Virtual network: VNet1
Subnet: Subnet1
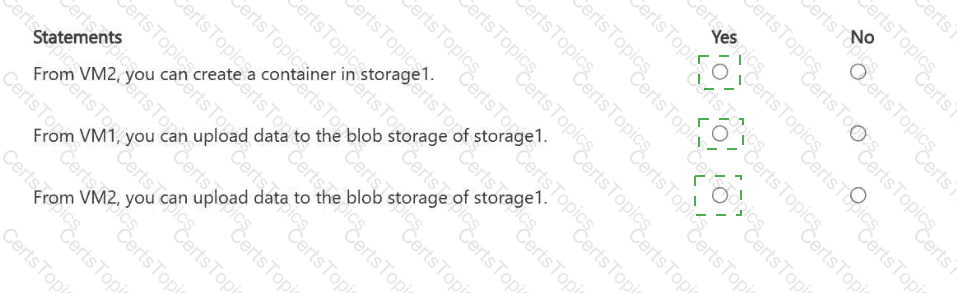
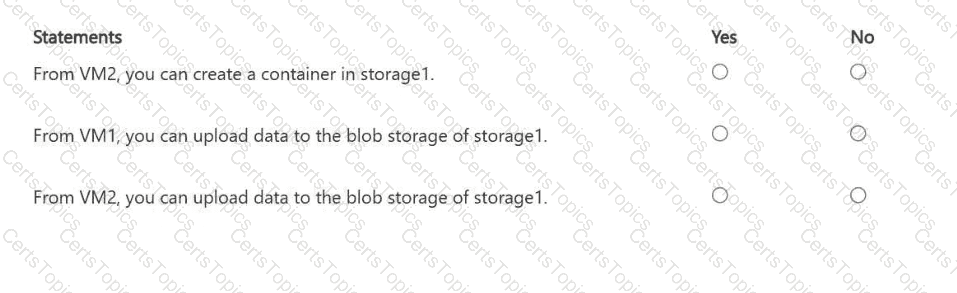
For each statement, select Yes if the statement is true. Otherwise, select No.
You have an Azure subscription that contains an Azure API Management instance named ContosoAPI1. ContosoAPI1 is configured with the Basic v2 pricing tier.
You need to configure SSL 3.0 support for ContosoAPI1.
What should you do first in the Azure portal?
Copyright © 2021-2026 CertsTopics. All Rights Reserved