You have an Azure virtual network that contains 100 virtual machines and an Azure Firewall instance named FW1.
All the traffic from the virtual machines is routed through FW1.
You need to ensure that FW1 allows access to only a URL of updates contoso.com and blocks all other outbound traffic.
What should you use?
You use Azure Virtual Network Manager to manage multiple virtual networks in a network group named Group1
You discover that the virtual machines in Group1 are accessible from the internet by using TCP port 3389.
You need to block inbound TCP 3389 from the internet across all the virtual networks in Group1 The solution must minimize administrative effort.
What should you use?
You have a Microsoft Entra tenant.
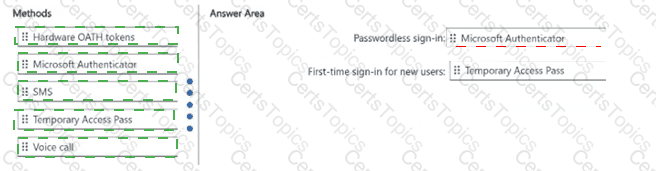
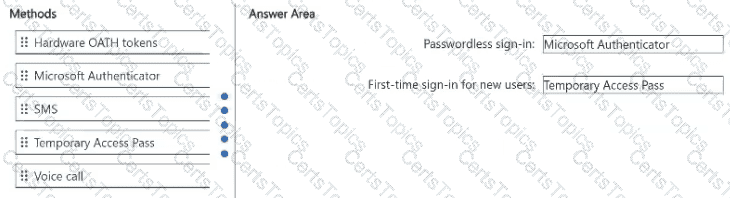
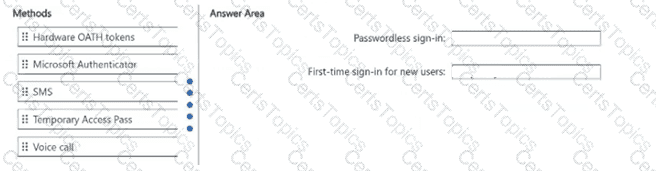
You need to implement password less authentication. The solution must meet the following requirements:
•Users can sign in without a password by using a mobile device.
•New users that sign in for the first time must use a helpdesk issued sign in method that expires.
Which authentication method should you enable for each requirement? To answer, drag the appropriate methods to the correct requirements. Each method may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
You have an Azure Logic Apps Consumption workflow that uses a Request trigger. All supported authentication methods are enabled on the Request trigger
You need to ensure that the endpoint accepts only OAuth-based requests. The solution must minimize costs.
What should you do?
Copyright © 2021-2026 CertsTopics. All Rights Reserved