Halloween Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: big75certs

Note! Following NSE7_LED-7.0 Exam is Retired now. Please select the alternative replacement for your Exam Certification.

Verified By IT Certified Experts

CertsTopics.com Certified Safe Files

Up-To-Date Exam Study Material

99.5% High Success Pass Rate

100% Accurate Answers

Instant Downloads

Exam Questions And Answers PDF

Try Demo Before You Buy

Certification Exams with Helpful Questions And Answers

Fortinet NSE 7 - LAN Edge 7.0 Questions and Answers

Question 1

Which EAP method requires the use of a digital certificate on both the server end and the client end?

Options:

A.

EAP-TTLS

B.

PEAP

C.

EAP-GTC

D.

EAP-TLS

Buy Now
Question 2

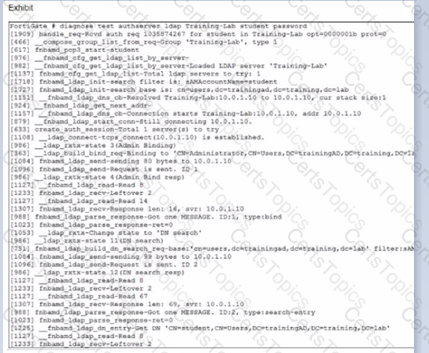
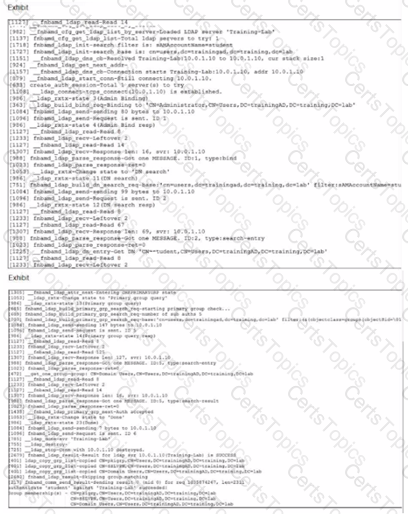
Refer to the exhibit.

Examine the partial debug output shown in the exhibit.

Which two statements about the debug output are true? (Choose1 two.)

Options:

A.

The LDAP DN search did not match any LDAP user.

B.

The credentials provided for student are correct.

C.

The Training-Lab LDAP server is configured to use regular bind.

D.

The connection to the Training-Lab LDAP server timed out.

Question 3

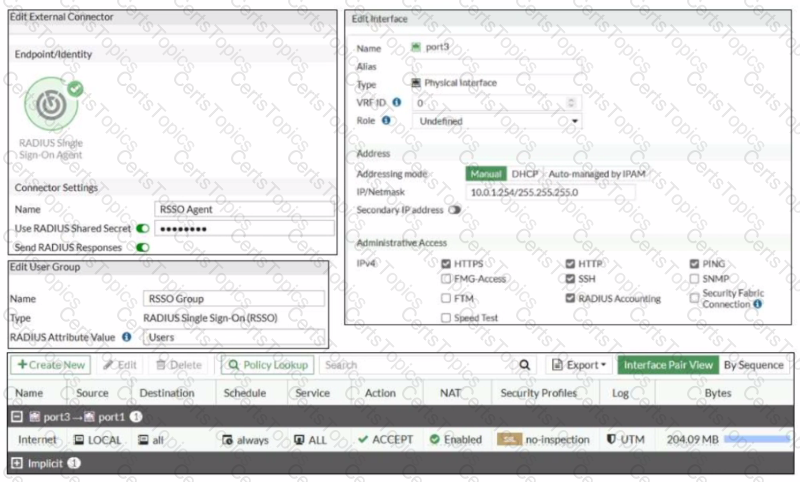
Refer to the exhibit

Examine the FortiGate RSSO configuration shown in the exhibit

FortiGate is configured to receive RADIUS accounting messages on port3 to authenticate RSSO users The users are located behind port3 and the internet link is connected to port1 FortiGate is processing incoming RADIUS accounting messages successfully and RSSO users are getting associated with the RSSO Group user group However all the users are able to access the internet, and the administrator wants to restrict internet access to RSSO users only

Which configuration change should the administrator make to fix the problem?

Options:

A.

Change the RADIUS Attribute Value selling to match the name of the RADIUS attribute containing the group membership information of the RSSO users

B.

Add RSSO Group to the firewall policy

C.

Enable Security Fabric Connection on port3

D.

Create a second firewall policy from port3 lo port1 and select the target destination subnets