Halloween Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: big75certs

Note! Following NSE5_FSM-6.3 Exam is Retired now. Please select the alternative replacement for your Exam Certification.

Verified By IT Certified Experts

CertsTopics.com Certified Safe Files

Up-To-Date Exam Study Material

99.5% High Success Pass Rate

100% Accurate Answers

Instant Downloads

Exam Questions And Answers PDF

Try Demo Before You Buy

Certification Exams with Helpful Questions And Answers

Fortinet NSE 5 - FortiSIEM 6.3 Questions and Answers

Question 1

Which process converts raw log data to structured data?

Options:

A.

Data classification

B.

Data validation

C.

Data parsing

D.

Data enrichment

Buy Now
Question 2

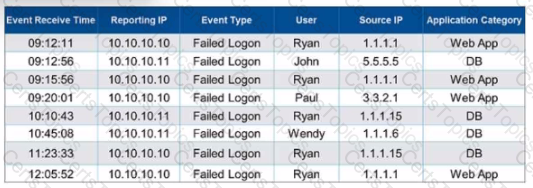
Refer to the exhibit.

If events are grouped by User. Source IP. and Application Category attributes in FortiSiEM. how many results will be displayed?

Options:

A.

Three results will be displayed.

B.

Five results will be displayed.

C.

No results will be displayed.

D.

Seven results will be displayed.

Question 3

Refer to the exhibit.

A FortiSIEM is continuously receiving syslog events from a FortiGate firewall The FortiSlfcM administrator is trying to search the raw event logs for the last two hours that contain the keyword tcp . However, the administrator is getting no results from the search.

Based on the selected filters shown in the exhibit, why are there no search results?

Options:

A.

The keyword is case sensitive Instead of typing TCP in the Value field. the administrator should type tcp.

B.

In the Time section, the administrator selected the Relative Last option, and in the drop-down lists, selected 2 and Hours as the lime period The time period should be 24 hours.

C.

The administrator selected - in the Operator column That a the wrong operator.

D.

The administrator selected AND in the Next drop-down list. This is the wrong boolean operator.