
Winter Sale 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: save70

CPEH-001 Exam Dumps : Certified Professional Ethical Hacker (CPEH)

PDF
CPEH-001 pdf
 Real Exam Questions and Answer
 Last Update: Nov 4, 2026
 Question and Answers: 736 With Explanation
 Compatible with all Devices
 Printable Format
 100% Pass Guaranteed
$27  $89.99
CPEH-001 exam
PDF + Testing Engine
CPEH-001 PDF + engine
 Both PDF & Practice Software
 Last Update: Nov 4, 2026
 Question and Answers: 736
 Discount Offer
 Download Free Demo
 24/7 Customer Support
$42  $139.99
Testing Engine
CPEH-001 Engine
 Desktop Based Application
 Last Update: Nov 4, 2026
 Question and Answers: 736
 Create Multiple Test Sets
 Questions Regularly Updated
  90 Days Free Updates
  Windows and Mac Compatible
$31.5  $104.99

Verified By IT Certified Experts

CertsTopics.com Certified Safe Files

Up-To-Date Exam Study Material

99.5% High Success Pass Rate

100% Accurate Answers

Instant Downloads

Exam Questions And Answers PDF

Try Demo Before You Buy

Certification Exams with Helpful Questions And Answers

Certified Professional Ethical Hacker (CPEH) Questions and Answers

Question 1

What type of vulnerability/attack is it when the malicious person forces the user’s browser to send an authenticated request to a server?

Options:

A.

Cross-site request forgery

B.

Cross-site scripting

C.

Session hijacking

D.

Server side request forgery

Buy Now
Question 2

The intrusion detection system at a software development company suddenly generates multiple alerts regarding attacks against the company's external webserver, VPN concentrator, and DNS servers. What should the security team do to determine which alerts to check first?

Options:

A.

Investigate based on the maintenance schedule of the affected systems.

B.

Investigate based on the service level agreements of the systems.

C.

Investigate based on the potential effect of the incident.

D.

Investigate based on the order that the alerts arrived in.

Question 3

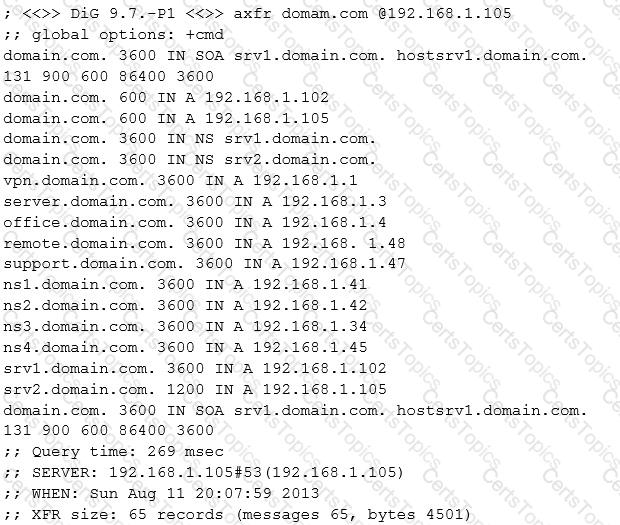
Look at the following output. What did the hacker accomplish?

Options:

A.

The hacker used whois to gather publicly available records for the domain.

B.

The hacker used the "fierce" tool to brute force the list of available domains.

C.

The hacker listed DNS records on his own domain.

D.

The hacker successfully transferred the zone and enumerated the hosts.