Halloween Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: big75certs

Note! Following CEH-001 Exam is Retired now. Please select the alternative replacement for your Exam Certification.

Verified By IT Certified Experts

CertsTopics.com Certified Safe Files

Up-To-Date Exam Study Material

99.5% High Success Pass Rate

100% Accurate Answers

Instant Downloads

Exam Questions And Answers PDF

Try Demo Before You Buy

Certification Exams with Helpful Questions And Answers

Certified Ethical Hacker (CEH) Questions and Answers

Question 1

Which of the following statements would NOT be a proper definition for a Trojan Horse?

Options:

A.

An authorized program that has been designed to capture keyboard keystroke while the user is unaware of such activity being performed

B.

An unauthorized program contained within a legitimate program. This unauthorized program performs functions unknown (and probably unwanted) by the user

C.

A legitimate program that has been altered by the placement of unauthorized code within it; this code performs functions unknown (and probably unwanted) by the user

D.

Any program that appears to perform a desirable and necessary function but that (because of unauthorized code within it that is unknown to the user) performs functions unknown (and definitely unwanted) by the user

Buy Now
Question 2

Jason's Web server was attacked by a trojan virus. He runs protocol analyzer and notices that the trojan communicates to a remote server on the Internet. Shown below is the standard "hexdump" representation of the network packet, before being decoded. Jason wants to identify the trojan by looking at the destination port number and mapping to a trojan-port number database on the Internet. Identify the remote server's port number by decoding the packet?

Options:

A.

Port 1890 (Net-Devil Trojan)

B.

Port 1786 (Net-Devil Trojan)

C.

Port 1909 (Net-Devil Trojan)

D.

Port 6667 (Net-Devil Trojan)

Question 3

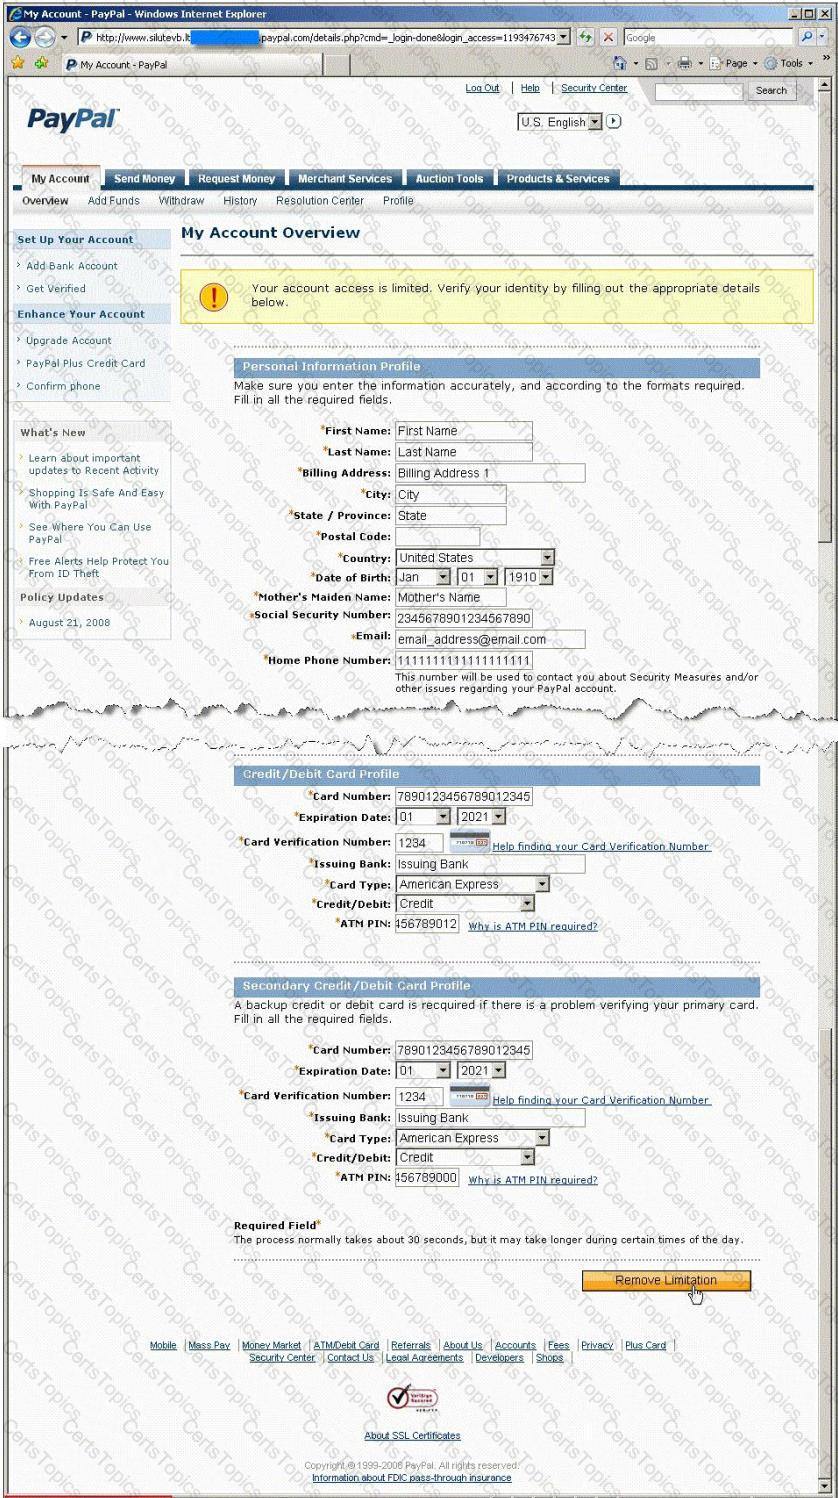
In this attack, a victim receives an e-mail claiming from PayPal stating that their account has been disabled and confirmation is required before activation. The attackers then scam to collect not one but two credit card numbers, ATM PIN number and other personal details.

Ignorant users usually fall prey to this scam. Which of the following statement is incorrect related to this attack?

Options:

A.

Do not reply to email messages or popup ads asking for personal or financial information

B.

Do not trust telephone numbers in e-mails or popup ads

C.

Review credit card and bank account statements regularly

D.

Antivirus, anti-spyware, and firewall software can very easily detect these type of attacks

E.

Do not send credit card numbers, and personal or financial information via e-mail