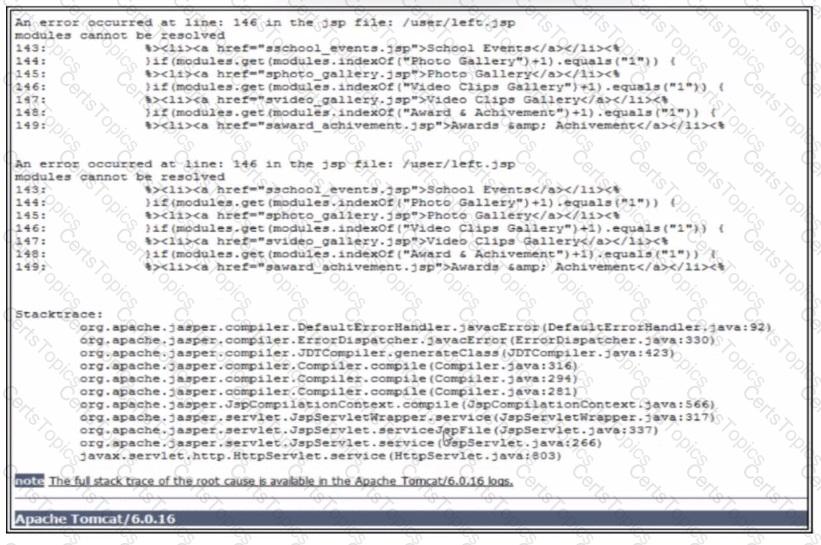
The correct answers areA. Service and version of the web serverandC. Technology used by the application. The error message shown in the exhibit is a classic example ofverbose error handling, which unintentionally discloses sensitive internal details about the web application stack.
First, the error page explicitly referencesApache Tomcat/6.0.16at the bottom. This directly exposes theweb server/service and its exact version, makingOption Acorrect. From an attacker’s perspective, this is valuable intelligence because it allows them to search forknown vulnerabilities, exploits, or misconfigurationsspecific to that version of Tomcat. Older versions of Tomcat, in particular, have a long history of publicly documented security flaws.
Second, the stack trace references components such as:
org.apache.jasper.compiler.*
.jsp files (e.g., /user/left.jsp)
javax.servlet.http.HttpServlet
These details clearly reveal thetechnology stack used by the application, namelyJava Server Pages (JSP)running onApache Tomcat with Apache Jasper. This confirmsOption Cas correct. Exposing application technology helps attackers tailor attacks such as deserialization exploits, JSP injection attempts, or framework-specific vulnerabilities.
Option B is incorrect because the error message doesnotstate or imply that Apache Jasper is vulnerable to path injection; it merely shows a compilation/runtime error. Option D is incorrect because the error page provides no information about theclient-side browser version—all disclosed details relate to server-side processing.
From a professional security and threat hunting perspective, verbose error messages significantlyincrease attack surface visibility. Best practices dictate that production systems should returngeneric error messagesto users while logging detailed stack traces internally. This scenario reinforces why proper error handling and information disclosure controls are critical defensive measures.
In summary, the penetration test error message exposes:
Theweb server service and version
Theapplication technology stack
Therefore, the correct answers areA and C.