Pre-Winter Sale 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: save70

Fortinet FCSS_LED_AR-7.6 Exam With Confidence Using Practice Dumps

Exam Code:
FCSS_LED_AR-7.6
Exam Name:
Fortinet NSE 6 - LAN Edge 7.6 Architect
Vendor:
Questions:
47
Last Updated:
Sep 24, 2026
Exam Status:
Stable
Fortinet FCSS_LED_AR-7.6

FCSS_LED_AR-7.6: Fortinet Certified Solution Specialist Exam 2025 Study Guide Pdf and Test Engine

Are you worried about passing the Fortinet FCSS_LED_AR-7.6 (Fortinet NSE 6 - LAN Edge 7.6 Architect) exam? Download the most recent Fortinet FCSS_LED_AR-7.6 braindumps with answers that are 100% real. After downloading the Fortinet FCSS_LED_AR-7.6 exam dumps training , you can receive 99 days of free updates, making this website one of the best options to save additional money. In order to help you prepare for the Fortinet FCSS_LED_AR-7.6 exam questions and verified answers by IT certified experts, CertsTopics has put together a complete collection of dumps questions and answers. To help you prepare and pass the Fortinet FCSS_LED_AR-7.6 exam on your first attempt, we have compiled actual exam questions and their answers. 

Our (Fortinet NSE 6 - LAN Edge 7.6 Architect) Study Materials are designed to meet the needs of thousands of candidates globally. A free sample of the CompTIA FCSS_LED_AR-7.6 test is available at CertsTopics. Before purchasing it, you can also see the Fortinet FCSS_LED_AR-7.6 practice exam demo.
Fortinet NSE 6 - LAN Edge 7.6 Architect Questions and Answers

Question 1

A conference center wireless network provides guest access through a captive portal, allowing unregistered users to self-register and connect to the network. The IT team has been tasked with updating the existing configuration to enforce captive portal authentication over a secure HTTPS connection. Which two steps should the administrator take to implement this change? (Choose two.)

Options:

A.

Enable HTTP redirect in the user authentication settings.

B.

Create a new SSID with the HTTPS captive portal URL.

C.

Disable HTTP administrative access on the guest SSID to enforce HTTPS connection.

D.

Update the captive portal URL to use HTTPS on FortiGate and FortiAuthenticator.

Buy Now
Question 2

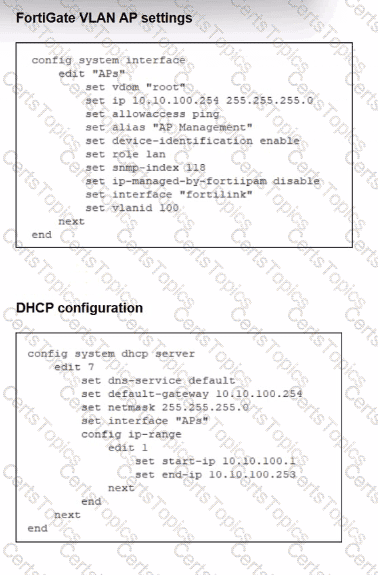
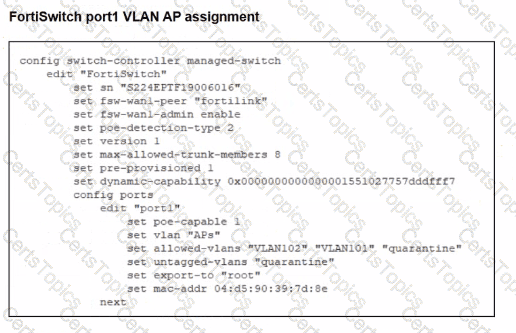
Refer to the exhibits.

A FortiSwitch is successfully managed by a FortiGate. FortiAP is connected to port1 of the managed FortiSwitch. On FortiGate, the VLAN AP is configured to detect and manage FortiAP, along with a DHCP server for the VLAN AP. Additionally, the VLAN AP is assigned to port1 of FortiSwitch. However. FortiGate is unable to detect or manage FortiAP.

Which FortiGate misconfiguration is preventing the detection of FortiAP?

Options:

A.

Security Fabric is disabled in the administrative access options of the VLAN.

B.

The FortiAP firmware is incompatible with the FortiGate firmware version.

C.

The VLAN is not tagged correctly on the FortiSwitch uplink port.

D.

The CAPWAP ports (UDP 5246 and 5247) are not open on FortiGate.

Question 3

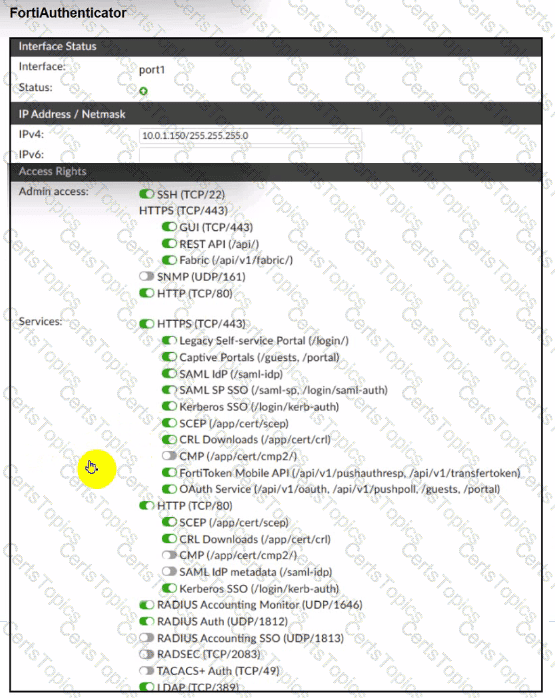
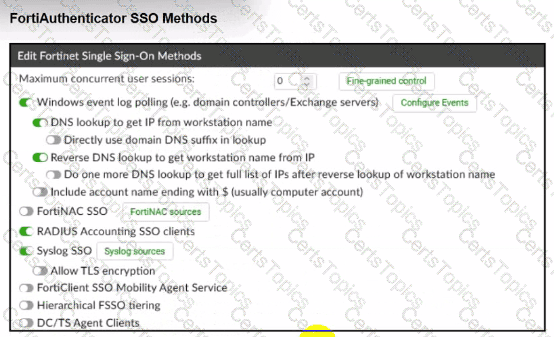
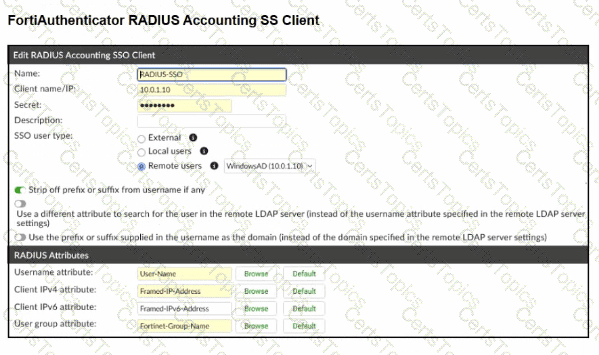
Refer to the exhibits.

A company has multiple FortiGate devices deployed and wants to centralize user authentication and authorization. The administrator decides to use FortiAuthenticator to convert RSSO messages to FSSO, allowing all FortiGate devices to receive user authentication updates.

After configuring FortiAuthenticator to receive RADIUS accounting messages, users can authenticate, but FortiGate does not enforce the correct policies based on user groups. Upon investigation, the administrator discovers that FortiAuthenticator is receiving RADIUS accounting messages from the RADIUS server and successfully queries LDAP for user group information. But, FSSO updates are not being sent to FortiGate devices and FortiGate firewall policies based on FSSO user groups are not being applied.

What is the most likely reason FortiGate is not receiving FSSO updates?

Options:

A.

The RADIUS Username and Client IPv4 attributes are not defined on FortiAuthenticator.

B.

The LDAP server is not configured to retrieve group memberships for RSSO users.

C.

FortiAuthenticator is missing the FSSO user group attribute in the configuration.

D.

The FortiAuthenticator interface is not enabled to receive RADIUS accounting messages.