
Weekend Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: big75certs

Download Latest CS0-004 Questions

Page: 2 / 6
Total 82 questions

CompTIA Cybersecurity Analyst CySA+ V4 (New Version) Questions and Answers

Question 5

A cybersecurity analyst is reviewing static application security testing scan results and notices a finding for hard-coded credentials.

Which of the following should the analyst recommend to the application team to resolve this concern?

Options:

A.

Implement a privileged access management solution.

B.

Enable single sign-on.

C.

Obfuscate application programming interface keys.

D.

Integrate secrets management.

Question 6

A vulnerability analyst conducts a security assessment on the Remote Desktop Protocol (RDP) security posture within the environment.

The analyst issues the following command for the assessment: nmap -p 3389 --script rdp* 10.0.0.0/24 The analyst receives responses, which are divided into one of the two categories, from 13 out of the 254 hosts:
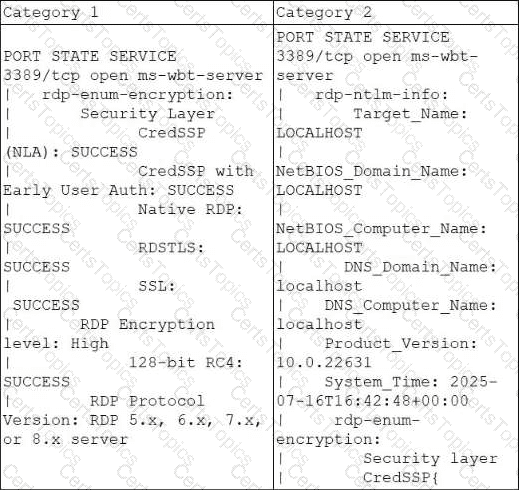
Which of the following conclusions can the analyst make about the output on Category 2?

Options:

A.

The systems are joined to an Active Directory domain and using New Technology LAN Manager (NTLM) as an authentication method.

B.

The systems are not joined to an Active Directory domain and are using Kerberos as an authentication method.

C.

The systems are not joined to an Active Directory domain and are using NTLM as an authentication method.

D.

The systems are joined to an Active Directory domain and are using Kerberos as an authentication method.

Question 7

Which of the following is the best reason to heavily segment business-critical assets from within the network?

Options:

A.

Legacy systems

B.

Degraded functionality

C.

Asset obfuscation

D.

Proprietary server

Question 8

A vendor releases details of a new vulnerability. When an analyst reviews the scheduled scans, no vulnerabilities are identified. The vulnerability is only discovered after a configuration change.

Which of the following scan types did the analyst configure?

Options:

A.

External

B.

Credentialed

C.

Agent-based

D.

Network

Page: 2 / 6
Total 82 questions
