
Power Up Your Study Prep: Black Friday 75% Discount! Use coupon code below to save! - Ends in 0d 00h 00m 00s - Coupon code: big75certs

Cisco 300-215 Exam With Confidence Using Practice Dumps

Exam Code:
300-215
Exam Name:
Conducting Forensic Analysis and Incident Response Using Cisco CyberOps Technologies (CBRFIR v1.2)
Certification:
Vendor:
Questions:
184
Last Updated:
Nov 17, 2026
Exam Status:
Stable
Cisco 300-215

300-215: CyberOps Professional Exam 2025 Study Guide Pdf and Test Engine

Are you worried about passing the Cisco 300-215 (Conducting Forensic Analysis and Incident Response Using Cisco CyberOps Technologies (CBRFIR v1.2)) exam? Download the most recent Cisco 300-215 braindumps with answers that are 100% real. After downloading the Cisco 300-215 exam dumps training , you can receive 99 days of free updates, making this website one of the best options to save additional money. In order to help you prepare for the Cisco 300-215 exam questions and verified answers by IT certified experts, CertsTopics has put together a complete collection of dumps questions and answers. To help you prepare and pass the Cisco 300-215 exam on your first attempt, we have compiled actual exam questions and their answers. 

Our (Conducting Forensic Analysis and Incident Response Using Cisco CyberOps Technologies (CBRFIR v1.2)) Study Materials are designed to meet the needs of thousands of candidates globally. A free sample of the CompTIA 300-215 test is available at CertsTopics. Before purchasing it, you can also see the Cisco 300-215 practice exam demo.

Conducting Forensic Analysis and Incident Response Using Cisco CyberOps Technologies (CBRFIR v1.2) Questions and Answers

Question 1

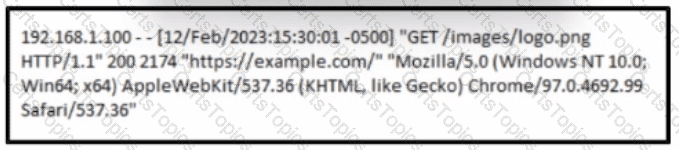
Rotor to the exhibit.

A cybersecurity analyst must analyst the logs from an Apache server for the client. The concern is that an offboarded employee home IP address was potentially used to access the company web server via a still active VPN connection Based on this log entry, what should an analyst conclude?

Options:

A.

An ex employee planted malware on the server

B.

A file was downloaded from the server

C.

A worker uploaded a file to the server

D.

An employee has accessed a web page on the server

Buy Now
Question 2

An insider scattered multiple USB flash drives with zero-day malware in a company HQ building. Many employees connected the USB flash drives to their workstations. An attacker was able to get access to endpoints from outside, steal user credentials, and exfiltrate confidential information from internal web resources. Which two steps prevent these types of security incidents in the future? (Choose two.)

Options:

A.

Automate security alerts on connected USB flash drives to workstations.

B.

Provide security awareness training and block usage of external drives.

C.

Deploy antivirus software on employee workstations to detect malicious software.

D.

Encrypt traffic from employee workstations to internal web services.

E.

Deploy MFA authentication to prevent unauthorized access to critical assets.

Question 3

The Linux system administrator of a company suspects that physical unauthorized access was granted to a local Linux terminal. The administrator wants to examine the suspected machine for potential unauthorized use and to get information about even/ account in this terminal including when the password last changed The administrator logs in as a root user Which file should be examined to get the information?

Options:

A.

/etc/users

B.

/etc/auth

C.

/etc/shadow

D.

/etc/passwd