
A hospital uses an AOS-10 architecture managed through HPE Aruba Networking Central. The customer has deployed a pair of HPE Aruba Networking 9000 Series gateways with Security licenses at every clinic. The gateways run IDS/IPS in IDS mode.
The Security Dashboard displays several recent events with the same signature, as shown below:
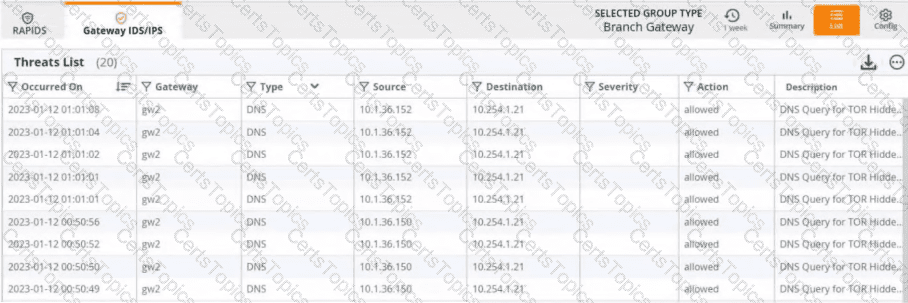
Occurred On: 2023-01-12 | Gateway: gw2 | Type: DNS | Source: 10.1.36.152 | Destination: 10.254.1.21 | Action: allowed | Description: DNS Query for TOR Hidden...
Which action could provide valuable context about the incident?
You want to use HPE Aruba Networking ClearPass Device Insight tags as conditions in CPPM role-mapping or enforcement-policy rules.
Which guidelines should you follow?
You are helping a company add HPE Aruba Networking ClearPass to its network, which uses HPE Aruba Networking infrastructure devices.
The company already has a Windows domain and Windows CA. The Windows CA issues certificates to domain computers, domain users, and servers such as domain controllers.
ClearPass cluster IP addressing and hostnames
Publisher = 10.47.47.5
Subscriber 1 = 10.47.47.6
Subscriber 2 = 10.47.47.7
Virtual IP with Subscriber 1 and Subscriber 2 = 10.47.47.8
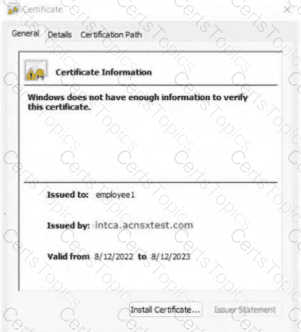
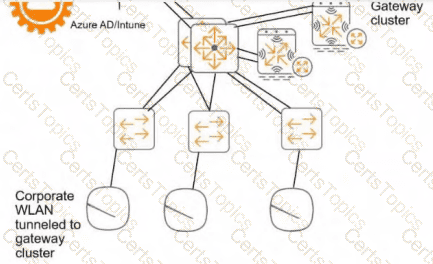
Refer to the scenario.
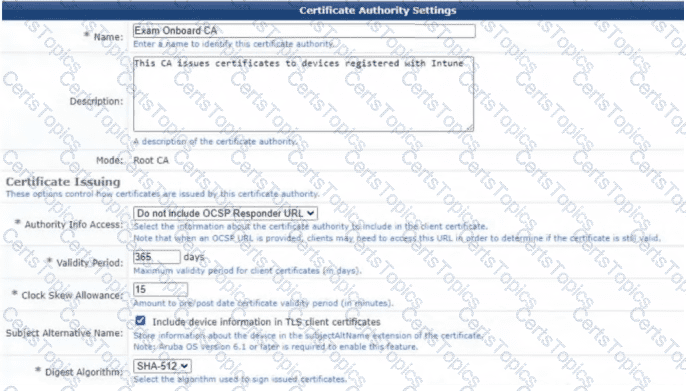
You have begun creating a CA to meet the customer's requirements for issuing certificates to mobile clients, as shown in the exhibit below.
Certificate Authority Settings:
Name: Exam Onboard CA
Mode: Root CA
Authority Info Access: Do not include OCSP Responder URL
Validity Period: 365 days
Clock Skew Allowance: 15
Subject Alternative Name: [X] Include device information in TLS client certificates
Digest Algorithm: SHA-512
What change will help meet those requirements and the requirements for authenticating clients?
A company has HPE Aruba Networking gateways and plans to begin implementing gateway IDS/IPS. The customer has chosen Block as the Fail Strategy.
What could you recommend to help reduce unexpected outages caused by this particular fail strategy?
Copyright © 2021-2026 CertsTopics. All Rights Reserved
