
You created a war room and want to run a connector action to look up the reputation of a domain. Then, you need to save the output for your team to review. However, there is a lot of output, and you want to limit the amount of information attached to the war room. How do you accomplish this? Choose one answer.
Refer to the exhibit.
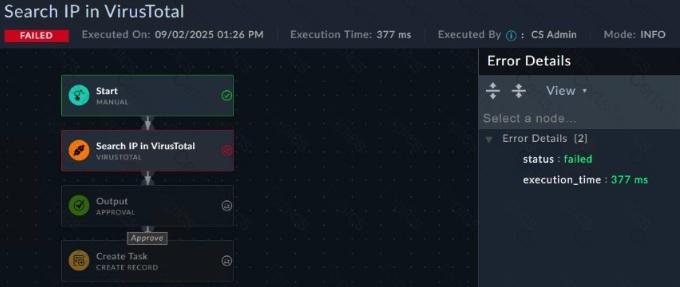
You created a new playbook and executed it as a test. However, it failed to run. You want to investigate, but you do not see details about the error. What is the reason for the lack of details?
Refer to the exhibit.
You notice that the custom event handler you configured to detect SMTP reconnaissance activities is creating a large number of events. This is overwhelming your notification system.
How can you fix this?
Review the following incident report:
Attackers leveraged a phishing email campaign targeting your employees.
The email likely impersonated a trusted source, such as the IT department, and requested login credentials.
An unsuspecting employee clicked a malicious link in the email, leading to the download and execution of a Remote Access Trojan (RAT).
The RAT provided the attackers with remote access and a foothold in the compromised system.
Which two MITRE ATT & CK tactics does this incident report capture? (Choose two.)
Copyright © 2021-2026 CertsTopics. All Rights Reserved
