
Cisco Related Exams
300-745 Exam
An agricultural company wants to enhance the cybersecurity posture by implementing a defense-in-depth strategy to protect against polymorphic malware threats. Currently, the company’s security infrastructure relies solely on a stateful traditional edge firewall that does not provide adequate protection against malware variants. Which technology must be added to the company’s security architecture to achieve the goal?
A developer is building new API functions for a cloud-based application. Before writing the code, the developer wants to ensure that destructive actions, including deleting and updating data, are properly protected by access control identifying sensitive fields such as those that contain passwords or personally identifiable information. Which approach must be used to score the risks proactively?
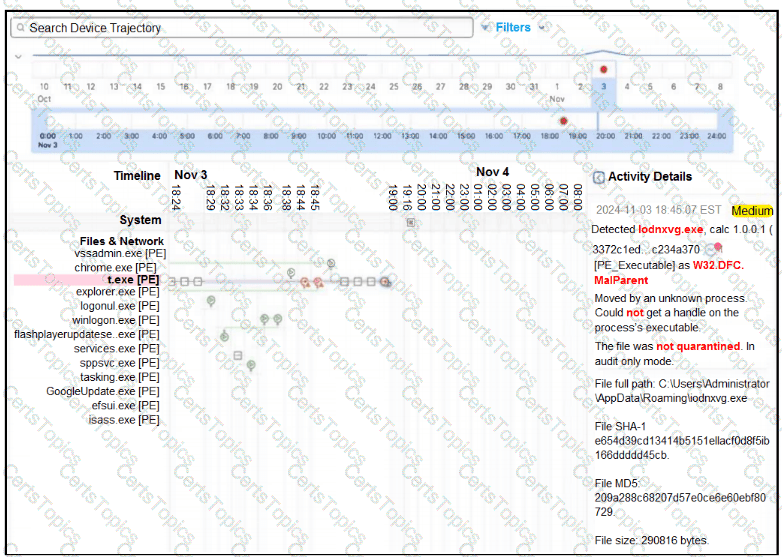
Refer to the exhibit.

A retail company recently deployed a file inspection feature using secure endpoint. The file inspection must detect and prevent the execution of malicious files on machines. During testing, logs showed that certain malicious files are still being executed despite the presence of the security measure. To understand why the threats are not being blocked, it is essential to investigate the configuration of secure endpoint policies. Which configuration is allowing the files to execute?